'Claudy Day' Flaws in Anthropic Claude Enable Data Theft via Fake Search Ads
Emerging Technology Risk · 6 sources · Updated 4mo ago · First seen Mar 18, 2026
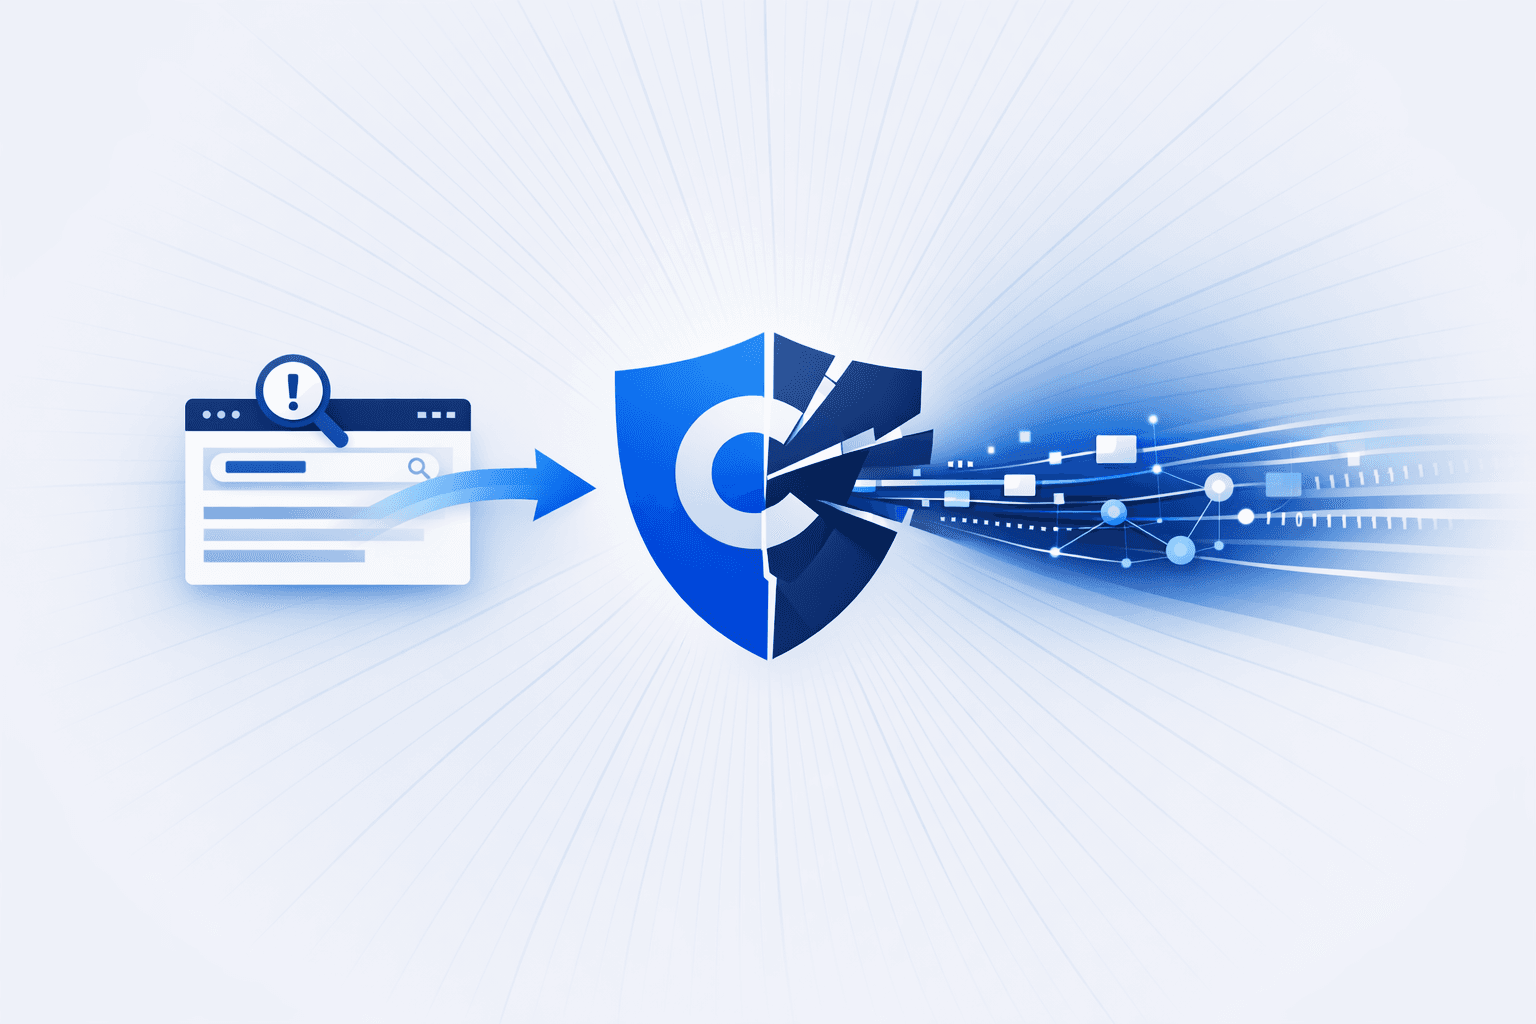
Researchers at Oasis Security disclosed an attack chain dubbed "Claudy Day" that combines three flaws in Anthropic’s Claude platform to enable covert data theft. The chain starts with attacker-controlled Google search results or fake Claude ads that abuse an open redirect on claude.com, leading victims to what appears to be a legitimate Claude page. From there, a pre-filled chat URL can carry hidden prompt-injection instructions embedded in HTML so the user sees benign text while Claude processes malicious commands in the background.
According to the reports, the chained flaws allow attackers to silently instruct Claude to search prior conversations for sensitive information and exfiltrate it through the Anthropic Files API, creating an end-to-end path from victim luring to unauthorized data exposure. The issue is notable because it does not require extra tooling, integrations, or MCP servers; built-in Claude features are sufficient for exploitation. A separate report about Claude autonomously exploiting vulnerable websites is not the same incident, and a report on the SideWinder espionage campaign is unrelated.