Active Exploitation of FortiClient EMS Authentication Bypass Enables Remote Code Execution
Active Exploitation · 14 sources · Updated 5mo ago · First seen Apr 4, 2026
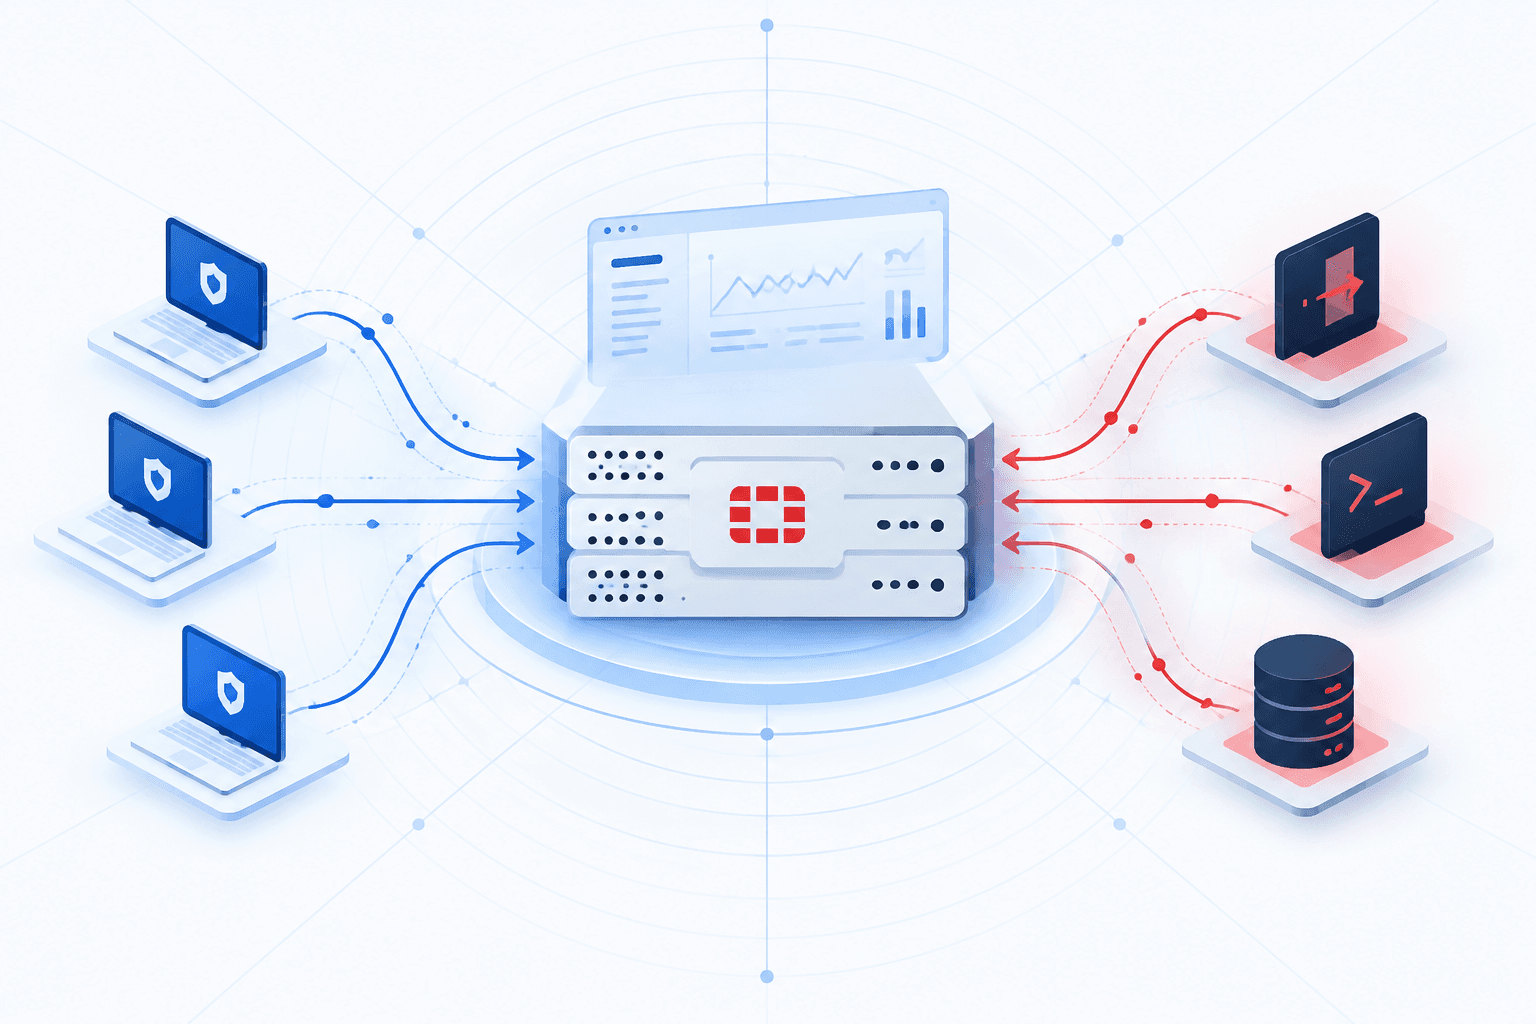
Fortinet disclosed a critical FortiClient Endpoint Management Server flaw, CVE-2026-35616, caused by improper access control in the EMS API that lets a remote, unauthenticated attacker bypass authentication and authorization and potentially execute code or commands on the host. Fortinet and CISA said the bug is being actively exploited as a zero-day, with affected versions identified as FortiClientEMS 7.4.5 through 7.4.6; the vendor directed customers to upgrade to 7.4.7 or apply available hotfixes.
Reporting and public tooling indicate attackers have been scanning for exposed EMS instances and targeting enterprise environments including government, healthcare, and cryptocurrency organizations. Security researchers published detection guidance and an exposure-checking tool for internet-facing systems, while defenders were urged to restrict external access to EMS, review logs for suspicious API activity, and assess whether exploitation may have been paired with other recently disclosed FortiClient EMS weaknesses such as CVE-2026-21643.