Fake Microsoft Teams Installers Deliver ValleyRAT via DLL Sideloading
Malware Intelligence · 3 sources · Updated 4mo ago · First seen Apr 10, 2026
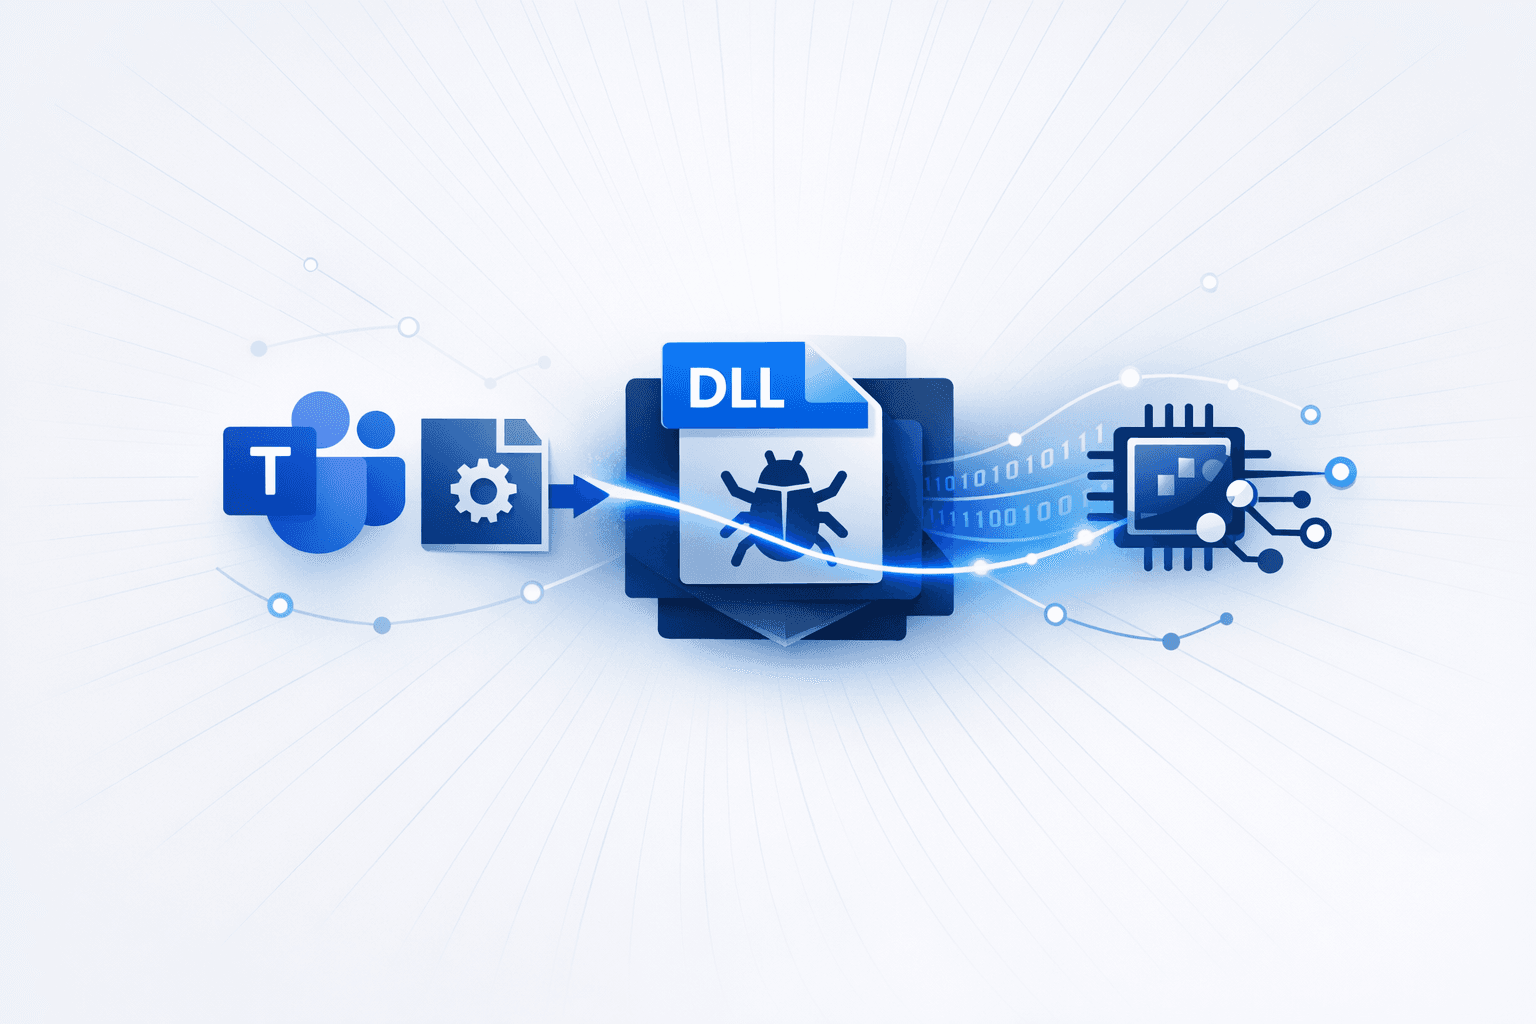
A malware campaign is using fake Microsoft Teams download pages promoted on X to lure corporate users into installing trojanized ZIP archives that deploy ValleyRAT. Researchers said the infection chain relies on an NSIS installer and DLL sideloading through Tencent’s legitimate GameBox.exe, then uses PowerShell to add Windows Defender exclusions, hide files, and establish persistence through unauthorized service creation and registry artifacts including _CCGDAT.
Once executed, the loader decrypts staged payloads from user.dat in memory using AES and XOR, with additional evasion through API hashing and reflective loading. The final ValleyRAT payload captures keystrokes, clipboard contents, and active-window activity before exfiltrating data to command-and-control infrastructure at 103.215.77.17; researchers said the campaign shows Chinese-language artifacts and behavioral overlaps that likely tie it to the SilverFox APT cluster.