
Loading story…
Breakglass Intelligence mapped nine live customer panels tied to the Needle malware-as-a-service operation, expanding the known infrastructure from a single publicly disclosed panel to a broader fleet spread across five ASNs and multiple hosting providers. All verified panels exposed a consistent Needle fingerprint on TCP port 3000, including a React/Vite single-page application and a responsive /api/v2/health endpoint. Two neighboring systems in the 178.16.54.0/23 OMEGATECH Netherlands range were assessed as likely vendor-operated infrastructure rather than standard customer-hosted tenants.
Artifacts published with the investigation showed each panel served a separately compiled Vite bundle with distinct filenames, sizes, and SHA-256 hashes, reinforcing the assessment that Needle operates as a multi-tenant MaaS platform rather than a single shared deployment. Uptime data suggested new panels were brought online steadily from March 30 through April 21 at a cadence of roughly one every one to three days, while four additional candidate IPs from a tipster-provided list were unresponsive and retained for monitoring as possible rotated, firewalled, or migrated nodes. The released dataset included panel metadata, HTTP responses, health-check results, bundle hashes, reproduction material, and captured JavaScript operator-panel UI bundles for the browser-stealer panel, but did not include authenticated admin access, server-side code, exploitation, victim data, or analysis of other Needle-associated payload stages.
TTPs, infrastructure, and targeting history in one profile.
4 events from the most recent confirmed update back to the earliest known activity.
Breakglass Intelligence released raw artifacts, panel metadata, HTTP responses, health-check results, bundle hashes, reproduction scripts, and captured JavaScript bundles from the April 22 investigation. The materials documented that each live panel served a distinct compiled Vite bundle, reinforcing the assessment that Needle operates as a true multi-tenant MaaS platform.
On April 22, 2026, Breakglass Intelligence confirmed nine live Needle customer panels exposed on TCP port 3000 across five ASNs and multiple hosting providers. Four additional candidate IPs were unresponsive and retained for monitoring as possible rotated, firewalled, or migrated infrastructure.
An earlier report published on April 20, 2026 described a public Needle malware-as-a-service panel and associated malware components, establishing the initial public disclosure that prompted follow-on investigation.
Uptime-derived deployment estimates indicate Needle infrastructure expanded steadily between March 30 and April 21, 2026, with new panels coming online roughly every one to three days. This suggests active customer onboarding consistent with a multi-tenant MaaS operation.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 23 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
2 references tracked. Mallory keeps watching after this page renders.
intel.breakglass.tech
Open sourcegithub.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Researchers uncovered a newly identified malware-as-a-service operation called **Evil Stealer** after its backend infrastructure was left exposed on Njalla-hosted systems, including an unauthenticated status API on port `8888` and a raw Next.js panel on port `3000`. The exposed API revealed a sequential counter showing **310,194 processed credential logs** within roughly six days, while the panel’s JavaScript also contained a cryptocurrency wallet drainer. Investigators linked the operation to domains including `evilmirror[.]net` and `ofmhubintel[.]com`, the latter tied to an **OnlyFans creator scraper**, indicating the actor was pursuing multiple monetization streams beyond credential theft. The operator was identified with high confidence through poor operational security in a promotional video whose unstripped XMP metadata exposed the Windows username **"moros"**, a Russian-language filename, and timestamps consistent with **UTC+3 / Moscow time**. Additional artifacts, including Russian keyboard indicators, shared registrar and hosting details, matching SSH HASSH fingerprints, and common Ubuntu templates, supported the assessment that the same Russian-speaking actor ran the linked infrastructure. Researchers also observed nearby suspicious services on the same hosting environment, including phishing and TLS interception infrastructure, although attribution for those adjacent systems was weaker; the malware payload and delivery chain for Evil Stealer itself had not yet been publicly identified.
Jun 29, 2026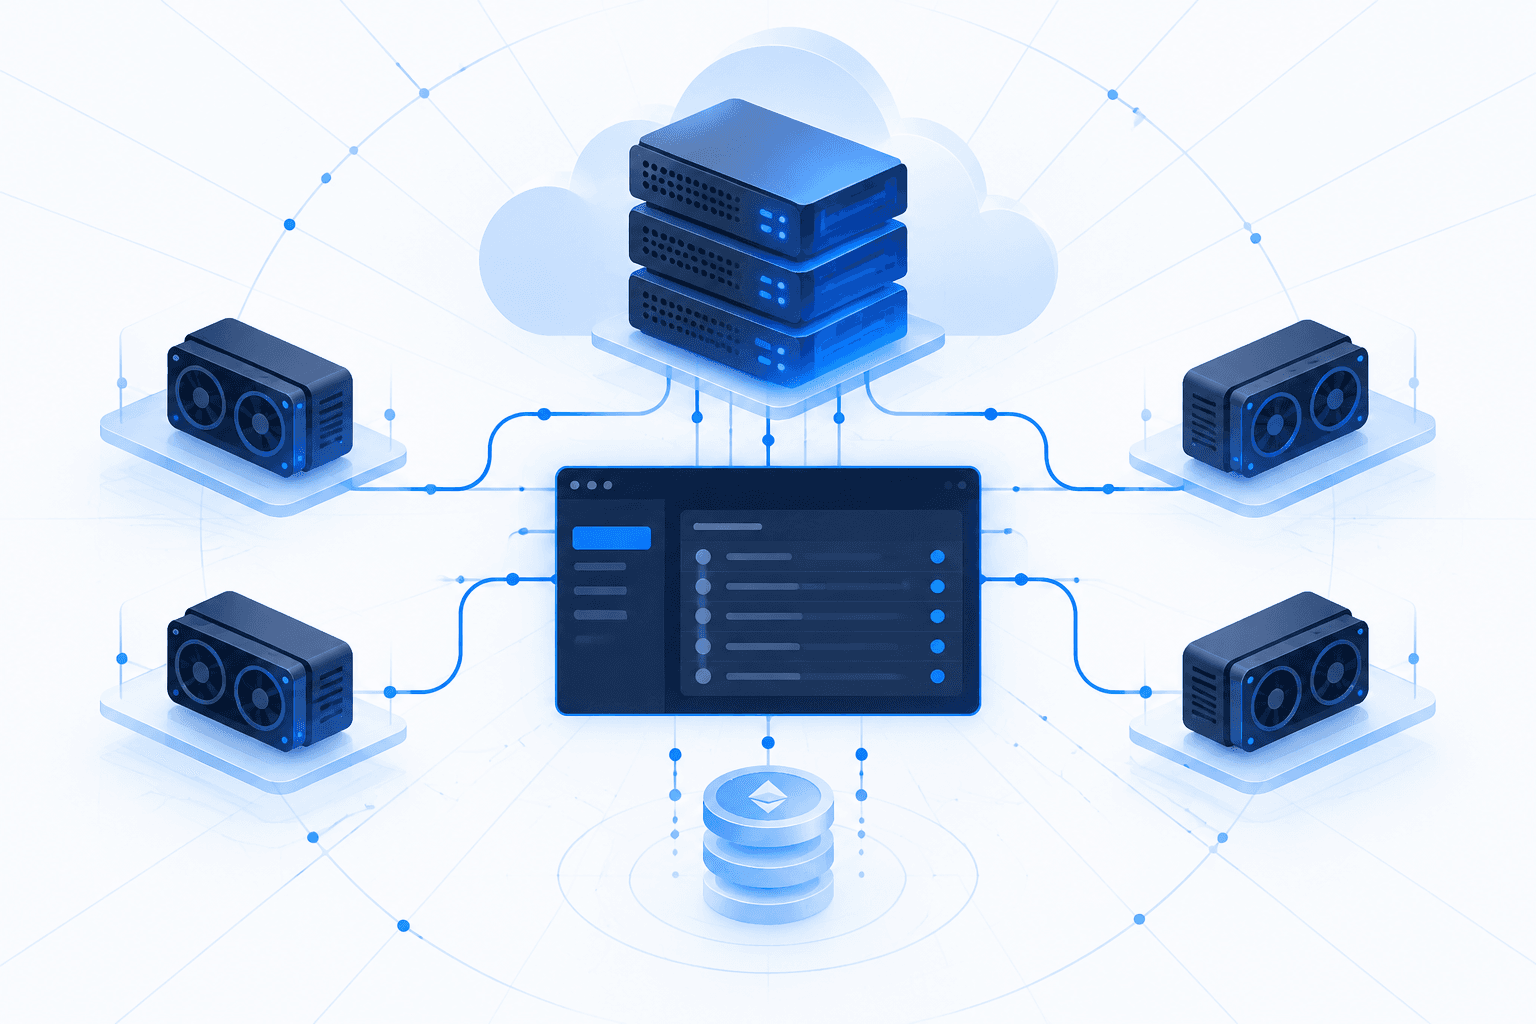
CloudSEK reported that an exposed **VHX Harvester v0.1.0** FastAPI panel at `69.48.229.140` was being used to prepare a cryptojacking operation against hosts on the vast.ai GPU-rental marketplace. The panel allegedly enumerated GPU hosts, scanned exposed services, harvested metadata and environment variables, deployed bridge agents into co-resident containers to probe Docker bridge networks, and obtained one root shell on a Jupyter Notebook instance. Its source code also described planned credential harvesting, stored-XSS attacks against Caddy authentication portals, Jupyter compromise, and cryptocurrency mining; no miner deployment had been observed. As of September 25, CloudSEK reported 297 discovered hosts, 13,368 scanned endpoints, 416 findings, and 25 bridge agents. The infrastructure was linked to 85 malicious `@prime0` npm packages published within minutes and impersonating 29 popular libraries through generated misspellings. Package installation reportedly beaconed host information to `69.48.229.140:8080`, while at least one package could poll the server every 30 seconds for shell commands. CloudSEK assessed that scoped package names were intended to influence npm search and autocomplete rather than capture ordinary unscoped installation typos, and cautioned that shared C2 infrastructure does not prove the npm packages enabled the GPU operation. The `@prime0` scope was removed; organizations should investigate dependency manifests and lockfiles for `@prime0` references, review potential execution on affected developer or build hosts, and validate reported indicators before blocking or SIEM ingestion.
Sep 29, 2026
Cybersecurity researchers disclosed a **persistent cross-site scripting (XSS)** vulnerability in the web-based administration panel used to operate the **StealC** information-stealer, enabling defenders to compromise the criminals’ own management interface. CyberArk researcher **Ari Novick** reported that insufficient input sanitization in the panel allowed injected JavaScript to execute in authenticated operator sessions, which in turn enabled collection of **system fingerprints**, monitoring of **active/live sessions**, and **exfiltration of session cookies** from StealC operators. Reporting indicates the access provided unusual visibility into StealC operator tradecraft and operational security failures, including the ability to infer operator environment details (e.g., IP/location and hardware characteristics when an operator accessed the panel without a VPN). StealC has been active since **January 2023** as a **malware-as-a-service (MaaS)** stealer and has been distributed via multiple lures and channels (including YouTube-based distribution and other social-engineering delivery methods); recent iterations included panel redesigns and added features such as Telegram notifications, and a subsequent **leak of the panel source code** helped create conditions for researchers to identify and exploit weaknesses in the operator infrastructure while withholding full exploit specifics to avoid rapid patching or copycat abuse.
Jun 29, 2026