Mallory
← Back to News
ransomware-group-operationperimeter-device-exposureinitial-access-methodinternet-facing-service-vulnerability

UNC2596 Exploits Exchange and FortiOS Flaws to Deploy Cuba Ransomware

Threat Actor Intelligence · 1 source · Updated 4mo ago · First seen May 25, 2026
UNC2596 Exploits Exchange and FortiOS Flaws to Deploy Cuba Ransomware

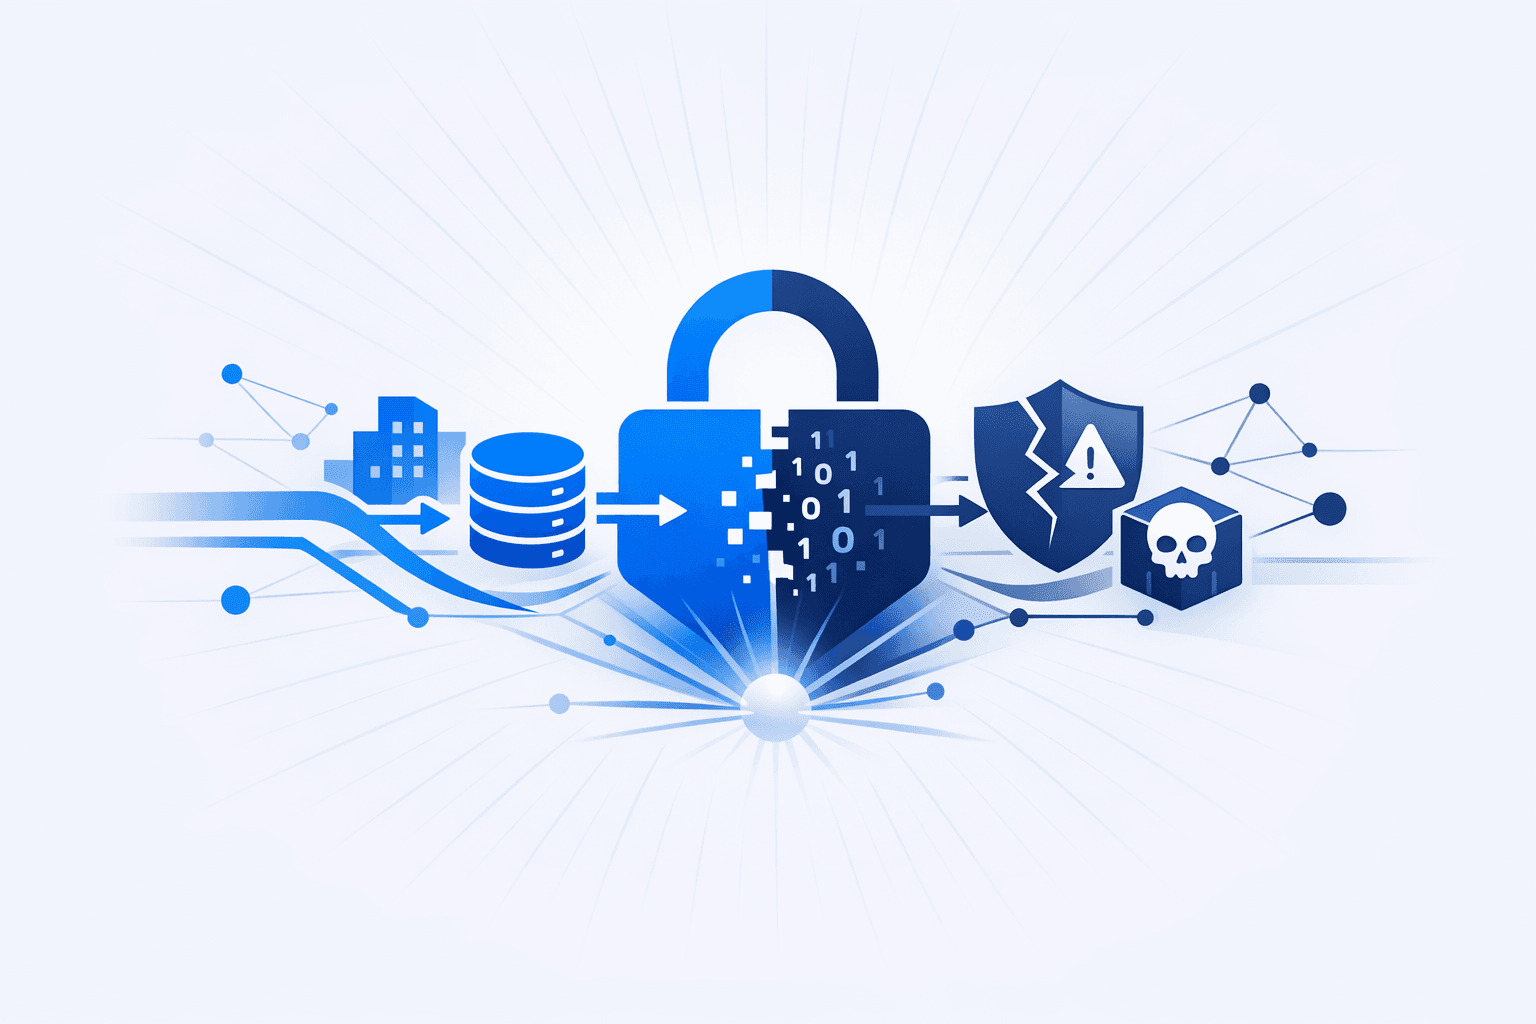
Mandiant reported that threat actor UNC2596 has been exploiting publicly known vulnerabilities in Microsoft Exchange and Fortinet FortiOS appliances to gain initial access and deploy Cuba ransomware. The activity shows the group chaining edge-device compromise with post-exploitation movement inside victim environments, using exposed enterprise infrastructure as an entry point before staging ransomware operations.

The intrusion pattern highlights how attackers continue to weaponize unpatched perimeter systems to reach internal networks and deliver financially motivated payloads. Mandiant linked the observed operations to Cuba ransomware deployment, underscoring the ongoing risk from internet-facing appliances and email infrastructure when critical vulnerabilities remain unremediated.
Know this adversaryTTPs, infrastructure, and targeting history in one profile.
Get the profile
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event · Mar 25, 2024
  1. Mar 25, 20243y ago

    Mandiant reports UNC2596 exploiting vulnerabilities to deploy Cuba ransomware

    Mandiant published research describing UNC2596 leveraging vulnerabilities to deploy Cuba ransomware, marking the public disclosure of the activity and associated threat reporting.

Do you run this?See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
Get the Full Actor Profile
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.