Cuba and Play Ransomware Exploit Exchange OWASSRF to Bypass ProxyNotShell Mitigations
Active Exploitation · 2 sources · Updated 1mo ago · First seen Nov 17, 2022
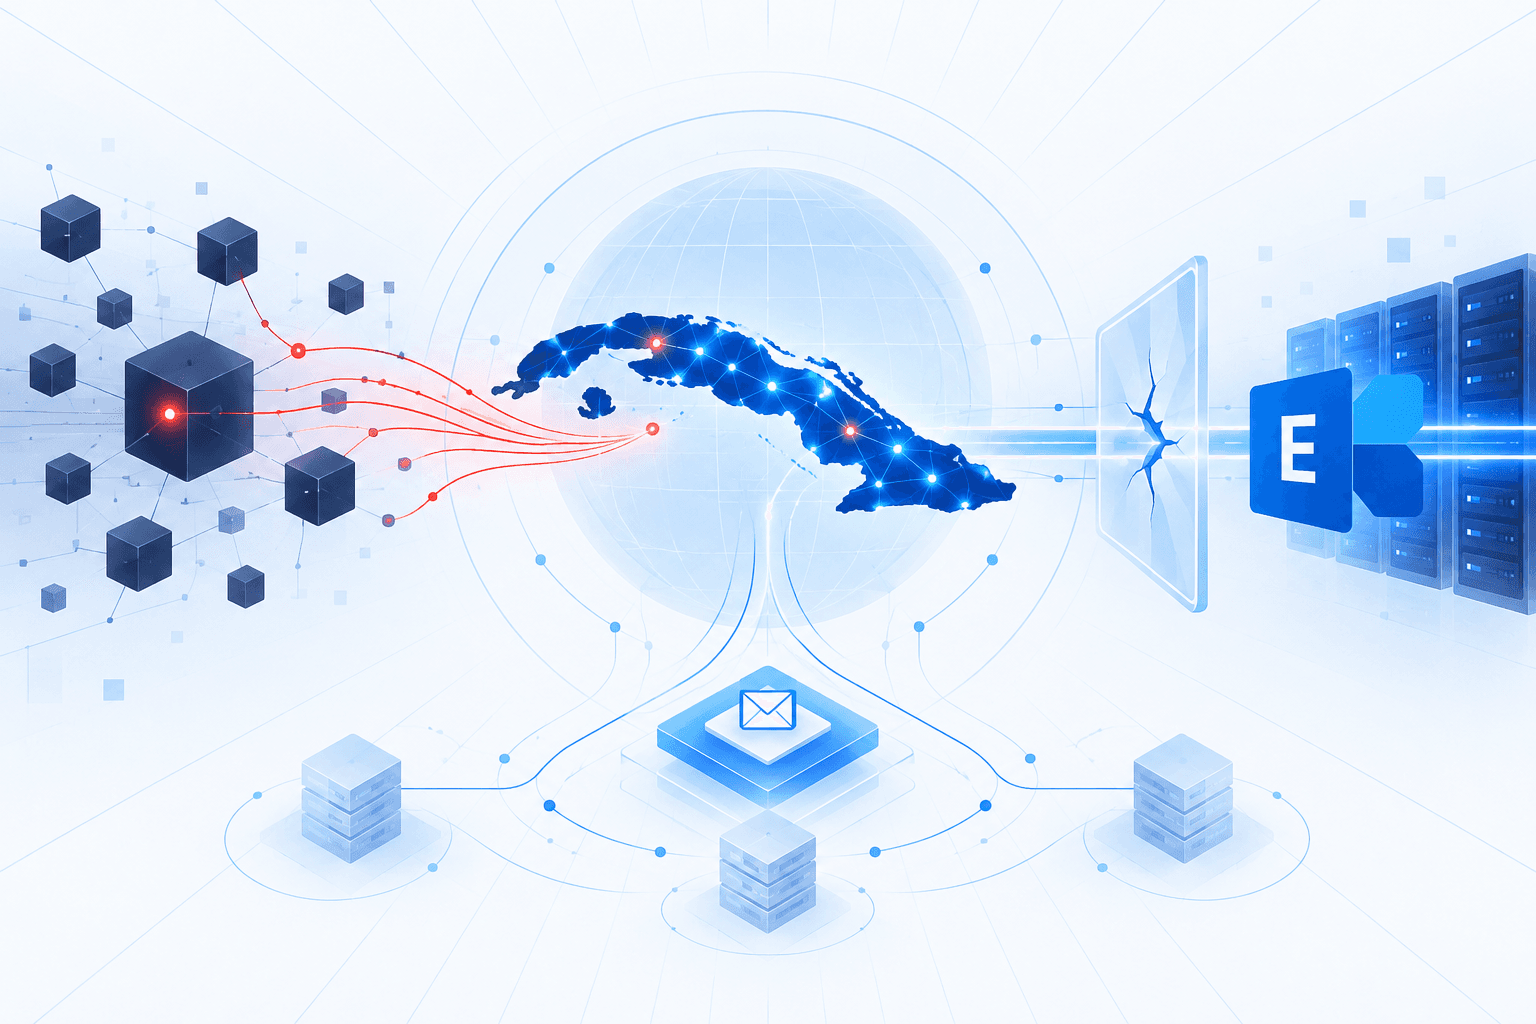
Microsoft reported that threat actors deploying Cuba and Play ransomware exploited CVE-2022-41080 to compromise unpatched Microsoft Exchange servers. Cuba-linked activity tracked as DEV-0671 began at least as early as November 17, 2022, while Play-linked exploitation began in late November. Play used the OWASSRF exploit to breach Rackspace, bypassing URL rewrite mitigations intended to block ProxyNotShell attacks; the exploit subsequently became publicly available.
Microsoft released patches addressing CVE-2022-41080 on November 8, 2022, before the reported exploitation began. CISA required Federal Civilian Executive Branch agencies to remediate the vulnerability by January 31, 2023. Organizations relying on ProxyNotShell URL rewrite rules remained exposed to this attack path and were urged to install current Exchange security updates or disable Outlook Web Access until patching was possible.