Android Devices Found Shipping With Firmware-Level Malware
Supply Chain Risk · 1 source · Updated 4mo ago · First seen May 25, 2026
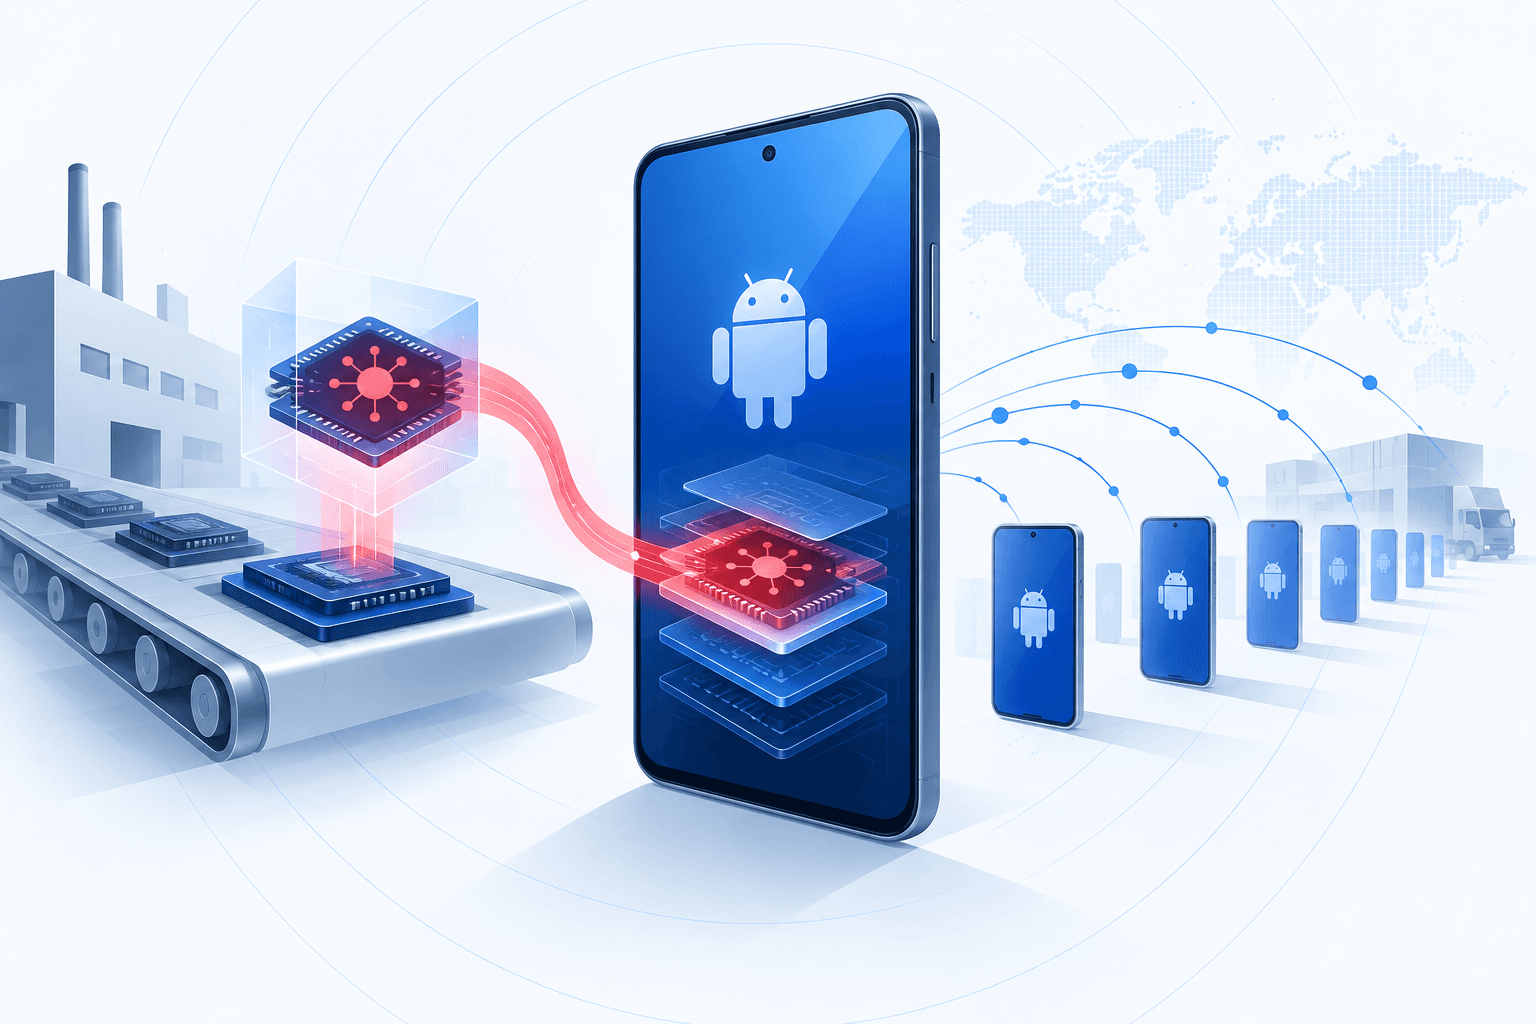
Sophos reported that some Android devices were delivered to users with malware already embedded at the firmware level, indicating compromise somewhere in the device supply chain rather than through a typical post-sale infection. Because the malicious code resides below the application layer, it can survive resets, evade standard mobile security controls, and give attackers persistent access to the device.
The finding raises concerns for enterprises that rely on Android endpoints for corporate access, especially where bring-your-own-device and low-cost handset procurement are common. Preinstalled firmware malware can expose credentials, communications, and managed applications from the moment a device is activated, making hardware sourcing, mobile threat defense, and strict device attestation critical parts of enterprise mobile security programs.