Midnight Mimosa Embeds Privileged Malware in Android Firmware Before Sale
Malware Intelligence · 3 sources · Updated 10d ago · First seen Oct 19, 2026
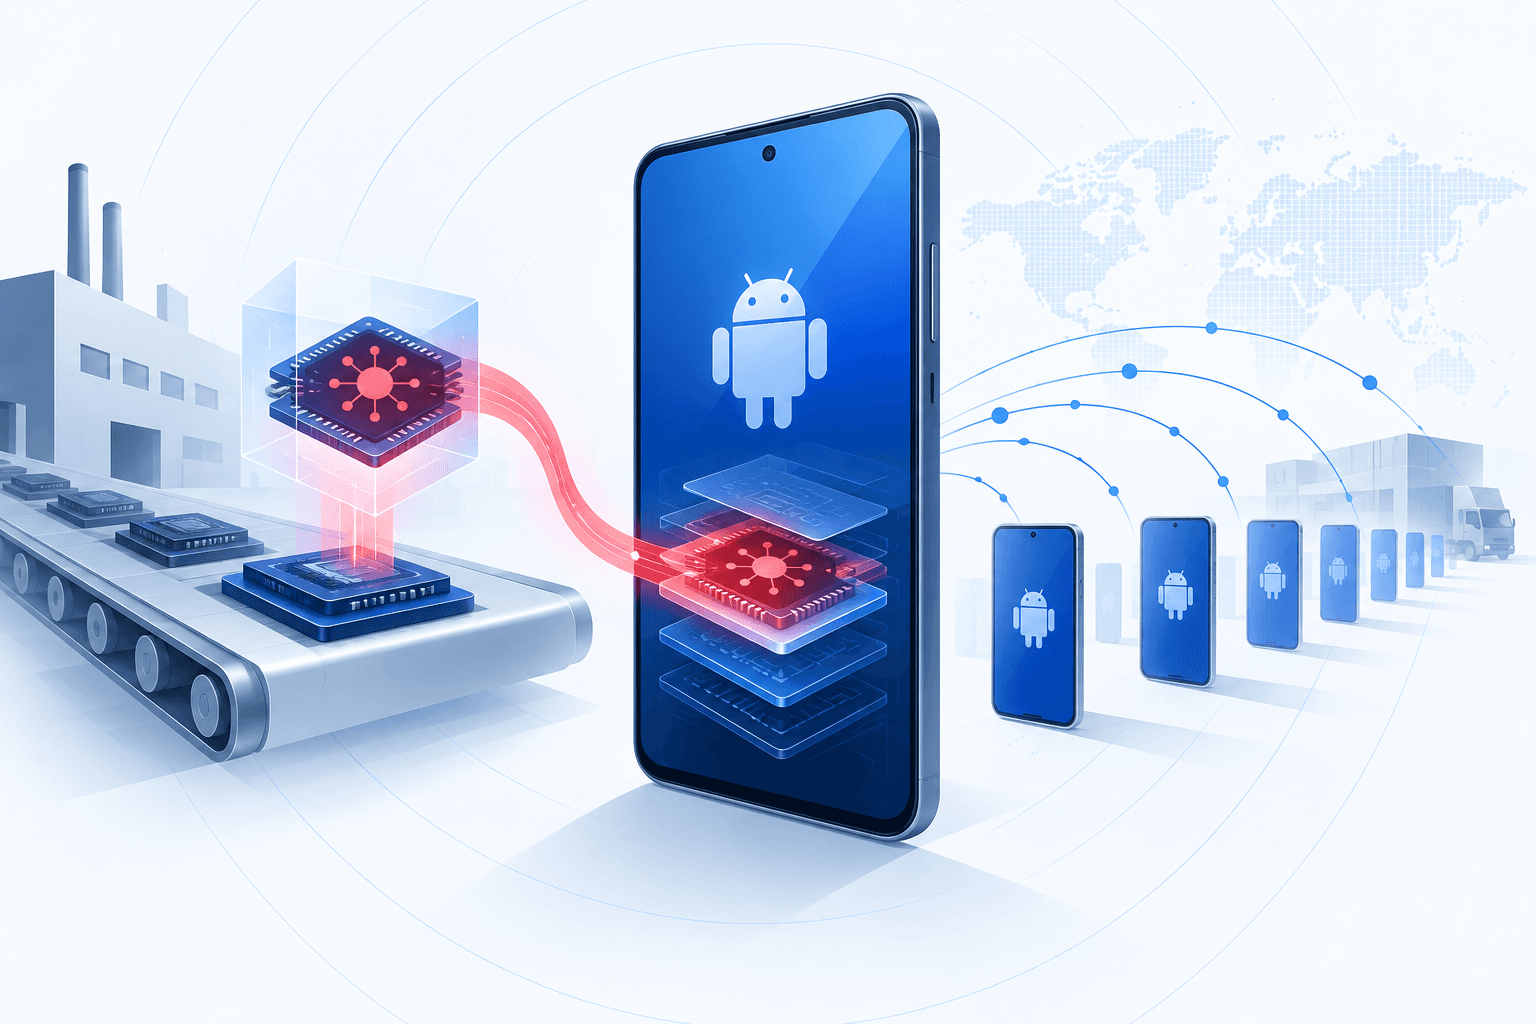
The Midnight Mimosa malware campaign embeds platform-signed, malicious system applications in the firmware of low-cost, MediaTek-based Android devices before purchase. Bitdefender observed thousands of infected devices across more than 150 countries over approximately two years and identified 13 related advertising-fraud applications distributed through Google Play. The firmware malware uses privileged access to download code, silently install additional payloads, and retrieve remotely controlled modules for advertising fraud and residential-proxy functionality. It temporarily disables the Google Play Store before installing payloads, apparently to evade detection; researchers did not establish that Google Play protections remain permanently disabled.
Researchers confirmed proxy capabilities but observed neither actual traffic relaying nor permission-based data theft during documented testing. The operators and precise supply-chain insertion point remain unknown. Removing visible applications alone may not eliminate the infection, because the firmware component can reinstall payloads. Organizations using unmanaged, BYOD, or inexpensive Android devices should assess device provenance, restrict suspect devices’ access to corporate resources, and avoid treating application removal as proof of remediation.