Attackers weaponize AI brands to spread phishing and malware
Social Engineering & Fraud · 13 sources · Updated 5mo ago · First seen Jun 8, 2026
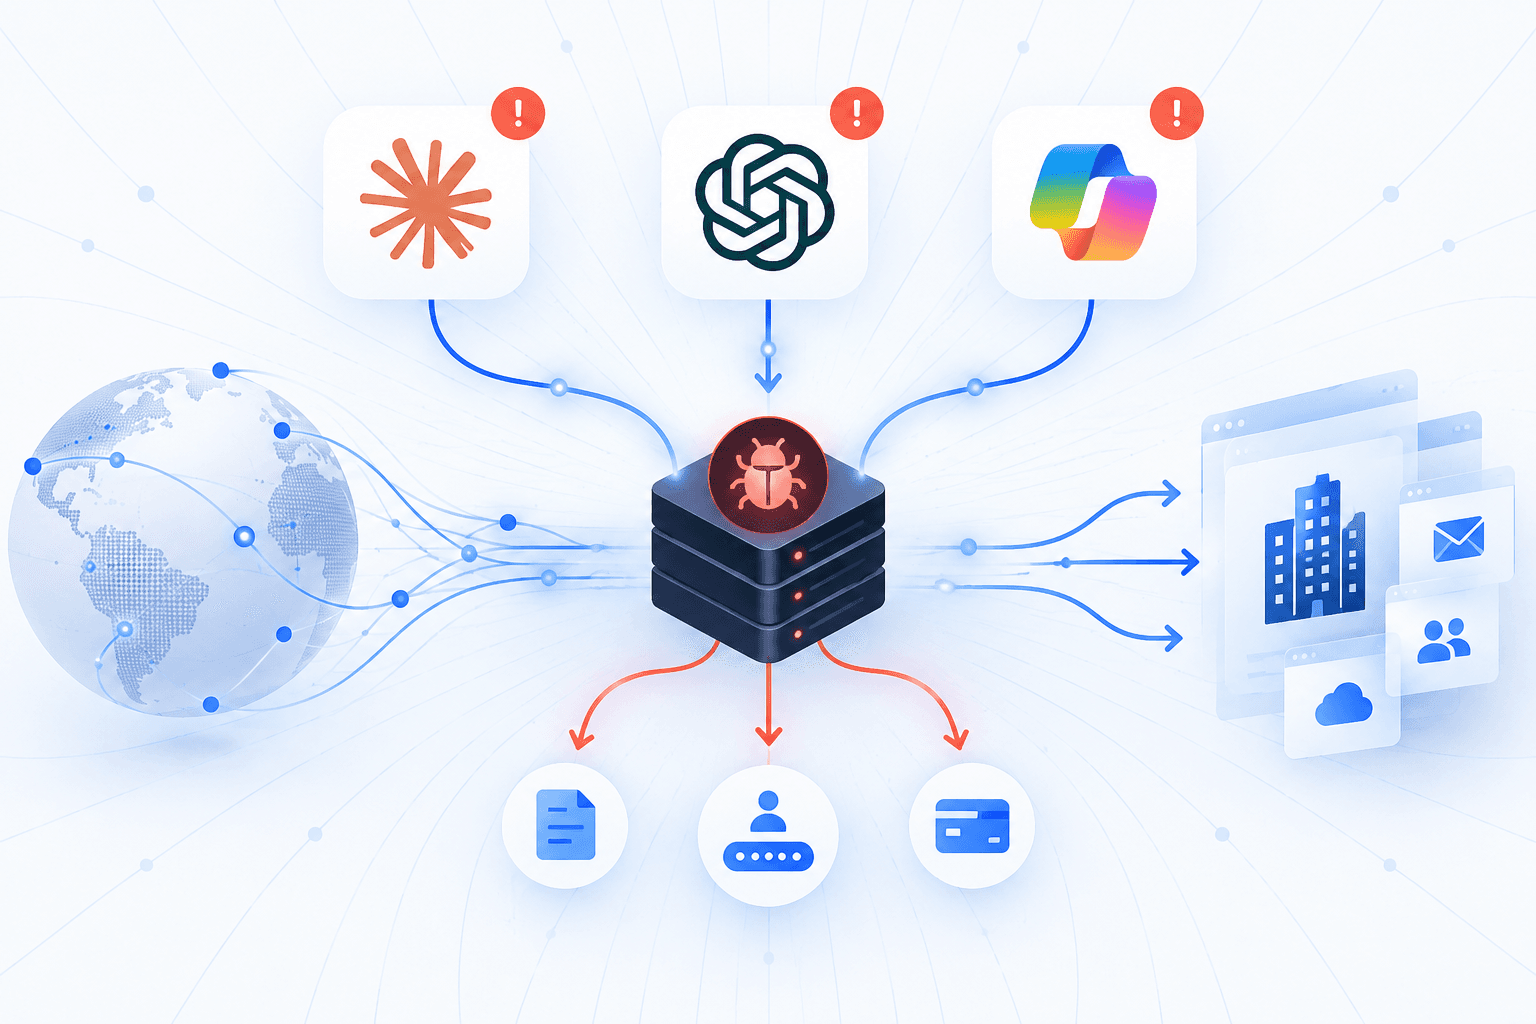
Microsoft Threat Intelligence reported that threat actors are exploiting the popularity of AI platforms including ChatGPT, Claude, DeepSeek, and Flux Pro AI to drive phishing, malvertising, and malware delivery rather than compromising the vendors themselves. One ChatGPT-themed campaign, aimed largely at South African users, used payment-update emails and redirect chains through legitimate services to a compromised site that harvested personal and credit card data. A separate Claude-themed operation targeted more than 2,000 organizations and likely used adversary-in-the-middle techniques to steal Microsoft sign-in credentials and authentication tokens.
Microsoft also linked large-scale AI-themed malvertising to Storm-3075, which pushed fake AI plugin downloads and delivered malware including Vidar Stealer, Lumma Stealer, Hijack Loader, and Oyster, with parts of the chain tied to Fox Tempest malware-signing services. In another case, attackers created a fake DeepSeek V4 GitHub repository within hours of the model’s launch, using copied benchmark data, official-looking branding, SEO tactics, and rotating payloads to distribute Vidar and GhostSocks malware before GitHub removed the infrastructure. Microsoft said it revoked certificates, disrupted Fox Tempest infrastructure with partners, and coordinated takedowns, while urging defenders to strengthen MFA, conditional access, browser protections, and endpoint and email defenses.