Mallory
← Back to News
extension-plugin-hijackidentity-impersonation-frauddata-exfiltration-methodai-platform-security

Malicious Perplexity-Themed Chrome Extension Hijacked Search Traffic

Supply Chain Risk · 9 sources · Updated 4mo ago · First seen Jun 29, 2026
Malicious Perplexity-Themed Chrome Extension Hijacked Search Traffic

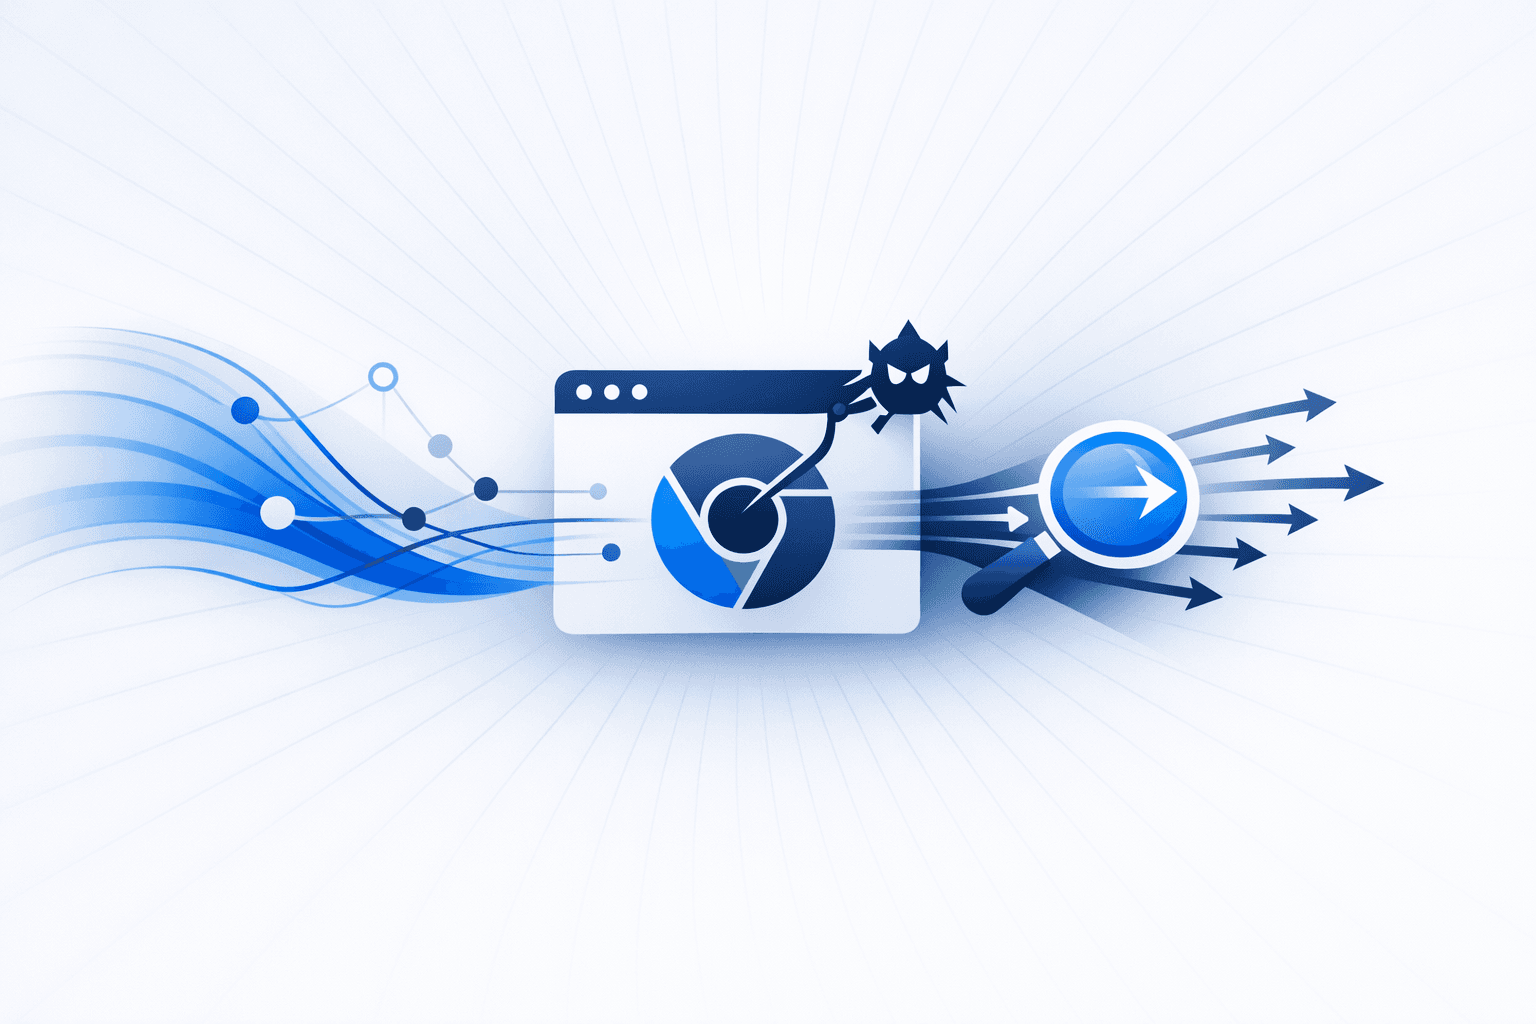
Microsoft Threat Intelligence disclosed that a malicious Chromium-based extension, "Search for perplexity ai," impersonated Perplexity AI and was distributed through the Chrome Web Store before Google removed it. The extension used the typosquatted domain perplexity-ai[.]online, changed the browser’s default search provider, intercepted Omnibox queries and live search suggestions, and then forwarded users to legitimate search engines so the activity appeared normal. It also opened an onboarding page at extension.tilda[.]ws/perplexityai to reinforce the fake branding.

Microsoft said the extension’s primary purpose was search interception and data collection rather than credential theft, although its permissions created significant privacy and security risk. By abusing Manifest V3 capabilities such as chrome_settings_overrides and declarativeNetRequest, the extension implemented a two-hop redirect chain that captured search terms, browser headers, user-agent strings, and source IP addresses through attacker-controlled infrastructure with server-side logging. Microsoft reported no definitive evidence of password theft, but said the collection of user browsing data was deliberate and covert.
Does this reach your builds?Trace attribution and downstream blast radius.
Trace the chain
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

2 events · Jun 29, 2026
  1. Jun 29, 20265mo ago

    Google removes malicious extension after Microsoft's disclosure

    After Microsoft responsibly disclosed the malicious extension to Google, Google removed "Search for perplexity ai" from the Chrome Web Store. The removal followed findings that the extension redirected omnibox queries and live search suggestions through attacker-controlled infrastructure.

    Chromium extension uses AI‑related branding to redirect browser search | Microsoft Security Blog
  2. Jun 29, 20265mo ago

    Microsoft identifies malicious 'Search for perplexity ai' extension

    Microsoft Threat Intelligence identified a malicious Chromium-based browser extension named "Search for perplexity ai" that spoofed Perplexity AI and intercepted browser search activity through the typosquatted domain perplexity-ai[.]online. Microsoft assessed its purpose as search traffic interception and data collection, including queries, headers, user-agent strings, and source IP addresses.

    Chromium extension uses AI‑related branding to redirect browser search | Microsoft Security Blog
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

2 linked
ChromiumChrome

Organizations

1 linked
Perplexity AI

Observables

7 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See attribution and downstream blast radius, and whether this package or vendor reaches your builds.
Trace the Supply Chain
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.