TypoPrompting Uses 186 Fake AI Domains to Deliver Malware and Hijack Browser Searches
Attack Tradecraft · 8 sources · Updated 16h ago · First seen Nov 12, 2026
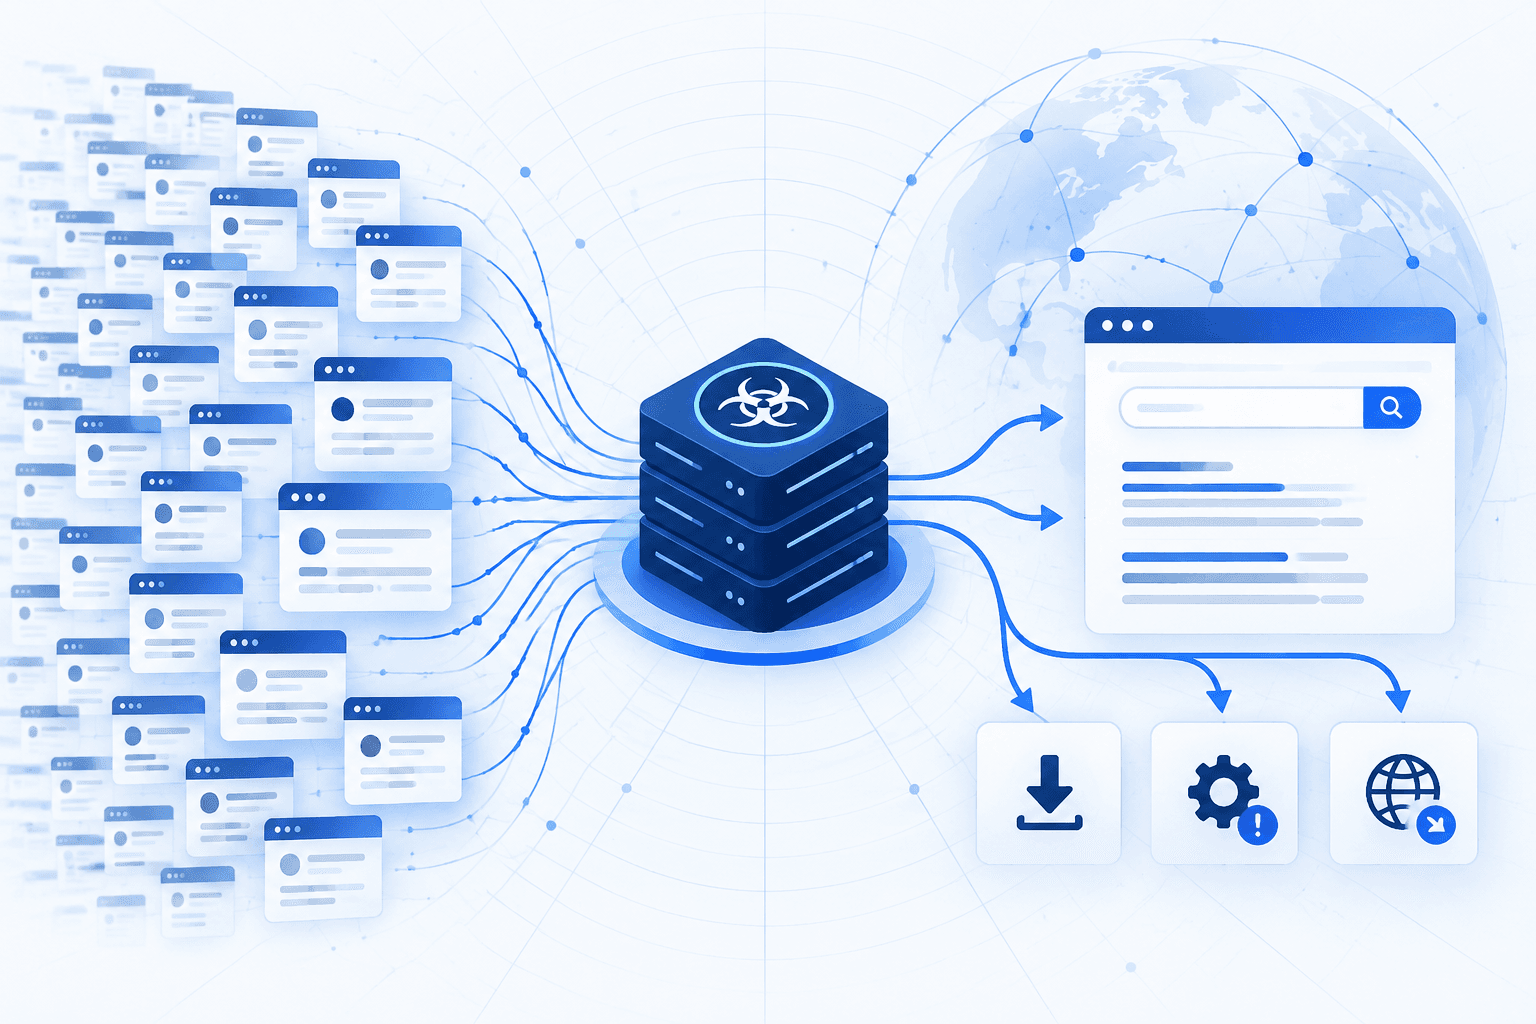
Island researchers identified TypoPrompting, a malware-delivery pattern using 186 lookalike domains impersonating 27 AI brands to funnel mistyped visits into ClickFix lures, browser-hijacking installers, and search-hijacking extensions. A Claude lookalike, cloude[.]ai, redirected visitors to a fake Cloudflare verification page that prompted them to run a hidden PowerShell script downloaded through a decimal-encoded IP address. Another route delivered Net Guard, a genuine Microsoft Store-signed package that researchers classified as browser-hijacking malware capable of executing remotely supplied JavaScript through browser DevTools, modifying browser profiles, changing search settings, and installing Chrome extensions.
A Perplexity lookalike led to a network of 30 linked search-hijacking extensions. Remaining Chrome Web Store listings collectively declared approximately 972,000 users as of November 3, 2026; that figure does not establish how many users encountered the malicious redirects. Hijacked searches could expose workplace queries containing internal hostnames, customer names, and project details to third parties. Researchers also found delivery infrastructure impersonating banking, insurance, telecommunications, and enterprise-software brands. Recommended defenses include approved service bookmarks, monitoring browser-to-shell execution, checking application provenance beyond digital signatures, and centrally enforcing browser search and extension policies.