Apple MIE Bypass on macOS Achieved via SMBClient and WebDAV Flaws
Attack Tradecraft · 2 sources · Updated 3mo ago · First seen Jul 27, 2026
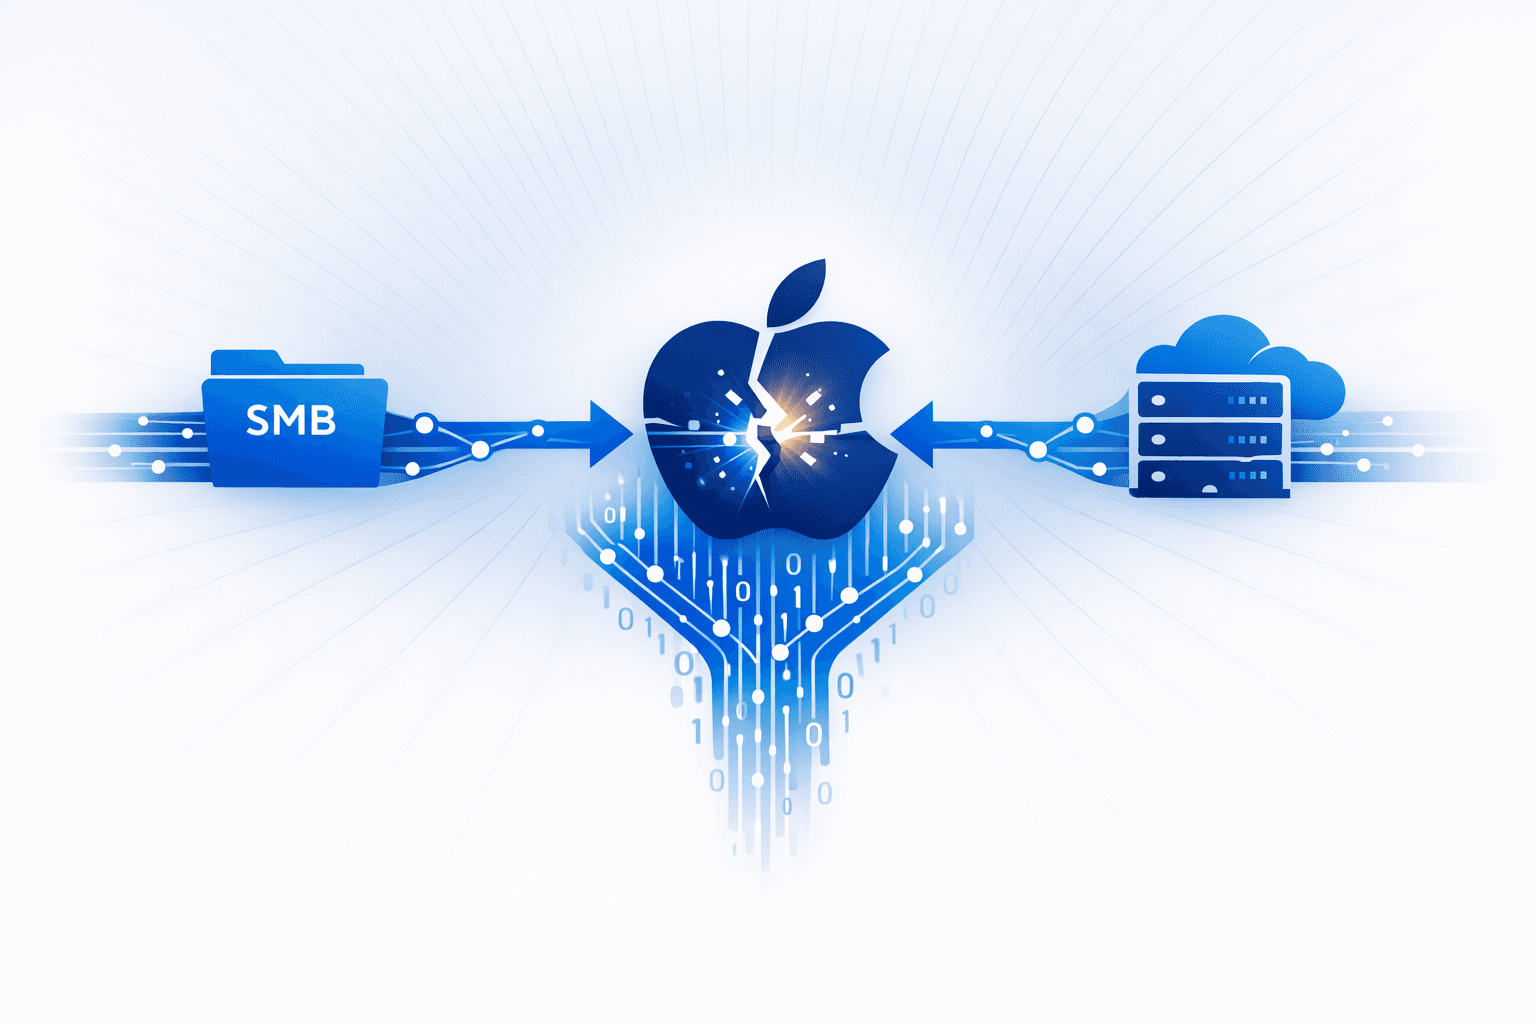
Researchers disclosed the first public bypass of Apple Memory Integrity Enforcement (MIE) on macOS 26.4.1 by chaining two vulnerabilities: CVE-2026-64704 in SMBClient and CVE-2026-64699 in webdavfs. The SMB flaw is a type confusion issue triggered when a macOS client connects to a malicious SMB server, causing the kernel to reinterpret a Resolve ID context as a lease context and misuse attacker-influenced kernel pointers. The WebDAV flaw is a kernel memory disclosure bug triggered by a crafted HTTP 206 response from a malicious WebDAV server, leaking uninitialized kernel memory to userspace.
The researchers said the combined exploit chain produces arbitrary kernel read/write primitives and ultimately kernel code execution, allowing an unprivileged user to escalate privileges to root despite Apple’s layered kernel protections. Apple has patched both issues in macOS 26.6, and the disclosure was accompanied by a public exploit-development challenge and notice of a planned Black Hat USA presentation detailing the technique.