Hidden Prompt Injection in Word Copilot Enables Self-Propagating AI Worms
Emerging Technology Risk · 10 sources · Updated 3mo ago · First seen Jul 29, 2026
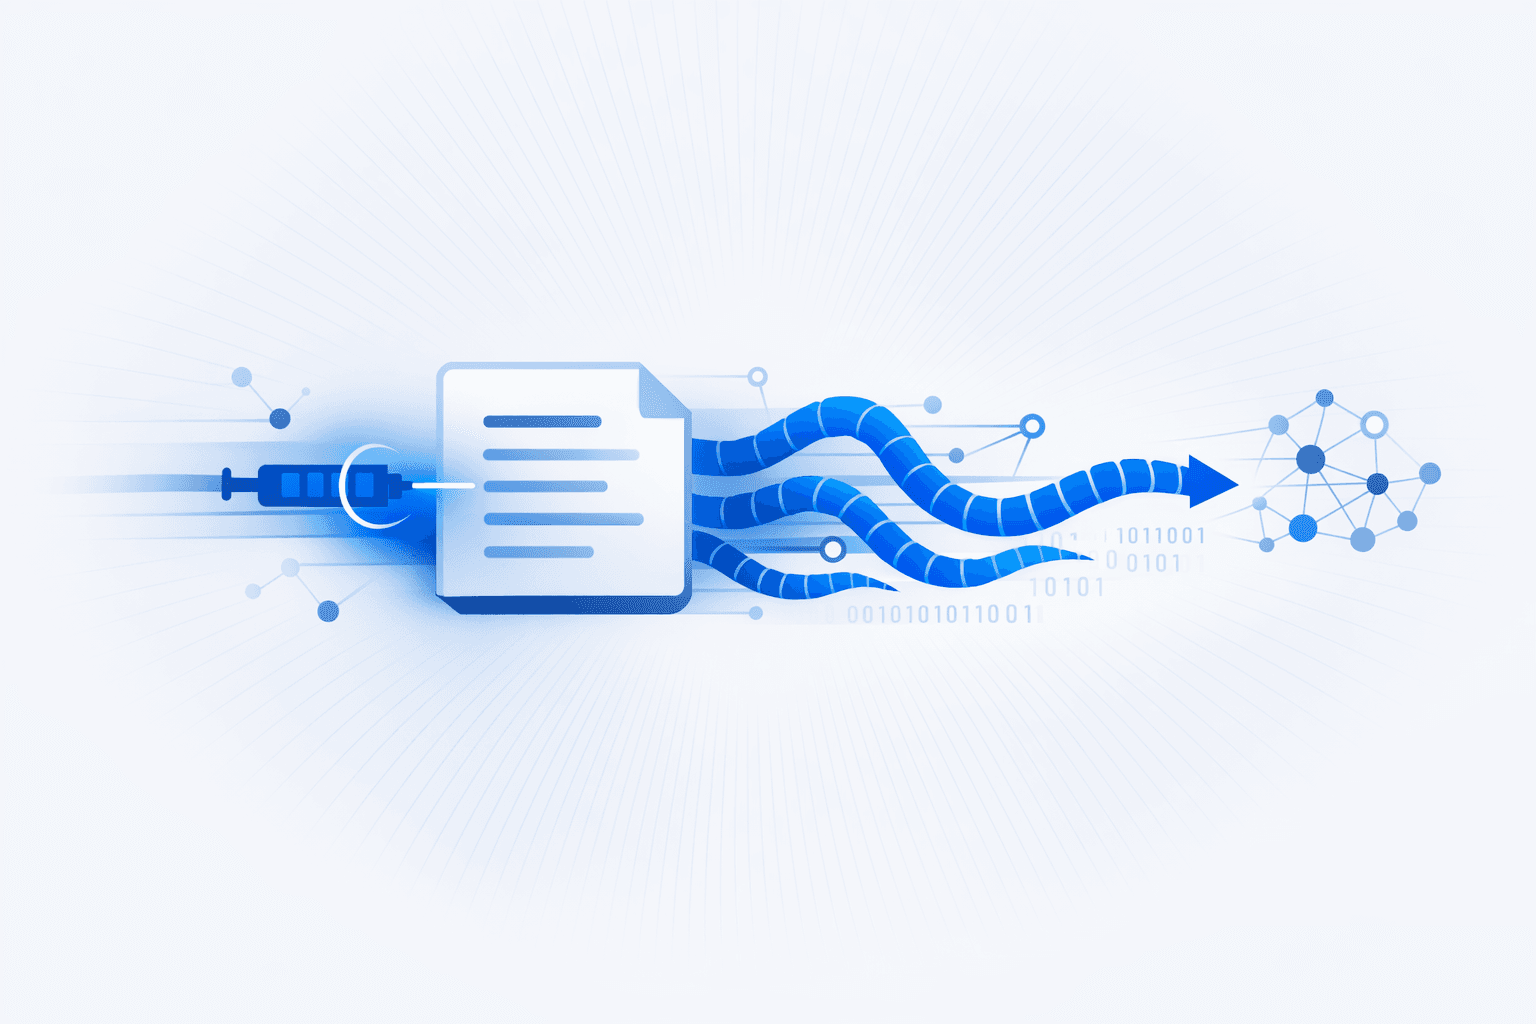
A researcher disclosed a self-propagating prompt-injection flaw in Microsoft Copilot for Word that allows hidden instructions embedded in a Word document to be interpreted by the underlying LLM and carried into Copilot-generated content. The attack requires only that a victim include an attacker-controlled document in Copilot’s context; the attacker does not need access to the victim’s Microsoft 365 tenant. Researchers said the malicious text can alter active business content and silently copy itself into newly edited or generated documents, creating a document-borne AI worm that crosses document trust boundaries.
The issue was reportedly reproduced across multiple Copilot configurations, including deployments upgraded to GPT-5.5 and GPT-5.6, despite Microsoft shipping mitigations and fixes for some proof-of-concept vectors during a roughly 144-day coordinated disclosure with MSRC. Researchers said the broader vulnerability class remained exploitable at publication, raising enterprise concerns over data integrity and traceability as poisoned documents spread through SharePoint, Teams, email, and other Microsoft 365 workflows. Microsoft’s partial fixes did not fully eliminate the risk, and customers were advised to treat external documents as untrusted and manually review both source files and Copilot output.