
Loading story…
Sage Water Resources said a cyber intrusion at its oilfield wastewater disposal site near Duchesne, Utah, altered an automated controller and bypassed pump shutdown safeguards, creating conditions that could have caused equipment failure or environmental damage. The company said the attack occurred on March 15 and targeted a programmable logic controller, with the manipulated safety logic allowing pumps to continue running dry while the control system falsely indicated normal operation.
According to Sage Energy Partners CFO Steve Crower, workers detected and stopped the malicious changes before the intrusion caused physical consequences. Sage had previously disclosed the incident in June and later provided additional details in an Aug. 3 email cited by DysruptionHub, framing the event as a serious attempted manipulation of industrial control systems at a critical wastewater disposal operation.
See the actors and campaigns active against you right now.
4 events from the most recent confirmed update back to the earliest known activity.
In an Aug. 3 email cited by later reporting, Sage Energy Partners CFO Steve Crower provided additional details about the incident and said he led the company's cybersecurity response. He stated that the attacker altered PLC safety logic and bypassed shutdown protections during the attack.
Sage Water Resources disclosed in June that a cyberattack had targeted its oilfield wastewater disposal site near Duchesne, Utah. Later reporting identified the incident as involving an automated controller at the saltwater disposal facility.
During the March 15 intrusion, workers intervened and stopped the malicious controller changes before they caused equipment failure or environmental damage. Sage said the attack had bypassed pump safeguards, making the incident a potentially serious critical infrastructure event.
On March 15, an attacker made malicious changes to an automated controller at Sage Water Resources' oilfield wastewater disposal site near Duchesne, Utah. According to the company, the intrusion altered programmable logic controller safety logic, bypassed shutdown protections, and caused pumps to continue running dry while the control system falsely showed normal operation.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
3 references tracked. Mallory keeps watching after this page renders.
malware.news
Open sourcedatabreaches.net
Open sourcedysruptionhub.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
More than 30 Minnesota community water systems reportedly suffered a coordinated intrusion into their operational-technology environments, disrupting remote monitoring and forcing some utilities to operate manually. Attackers reportedly reached internet-exposed programmable logic controllers (PLCs) through cellular gateways, changed controller IP addresses and passwords, and deprived operators of visibility into affected equipment. Authorities have not confirmed the vulnerability or equipment involved at most affected utilities. The incident nonetheless highlights the risk from publicly reachable OT assets, including exposed Rockwell Logix controllers affected by the actively exploited, unpatched authentication-bypass vulnerability `CVE-2021-22681`; utilities should remove public OT exposure, segment networks, harden remote access, monitor configuration changes, and maintain tested manual fallback procedures.
Aug 27, 2026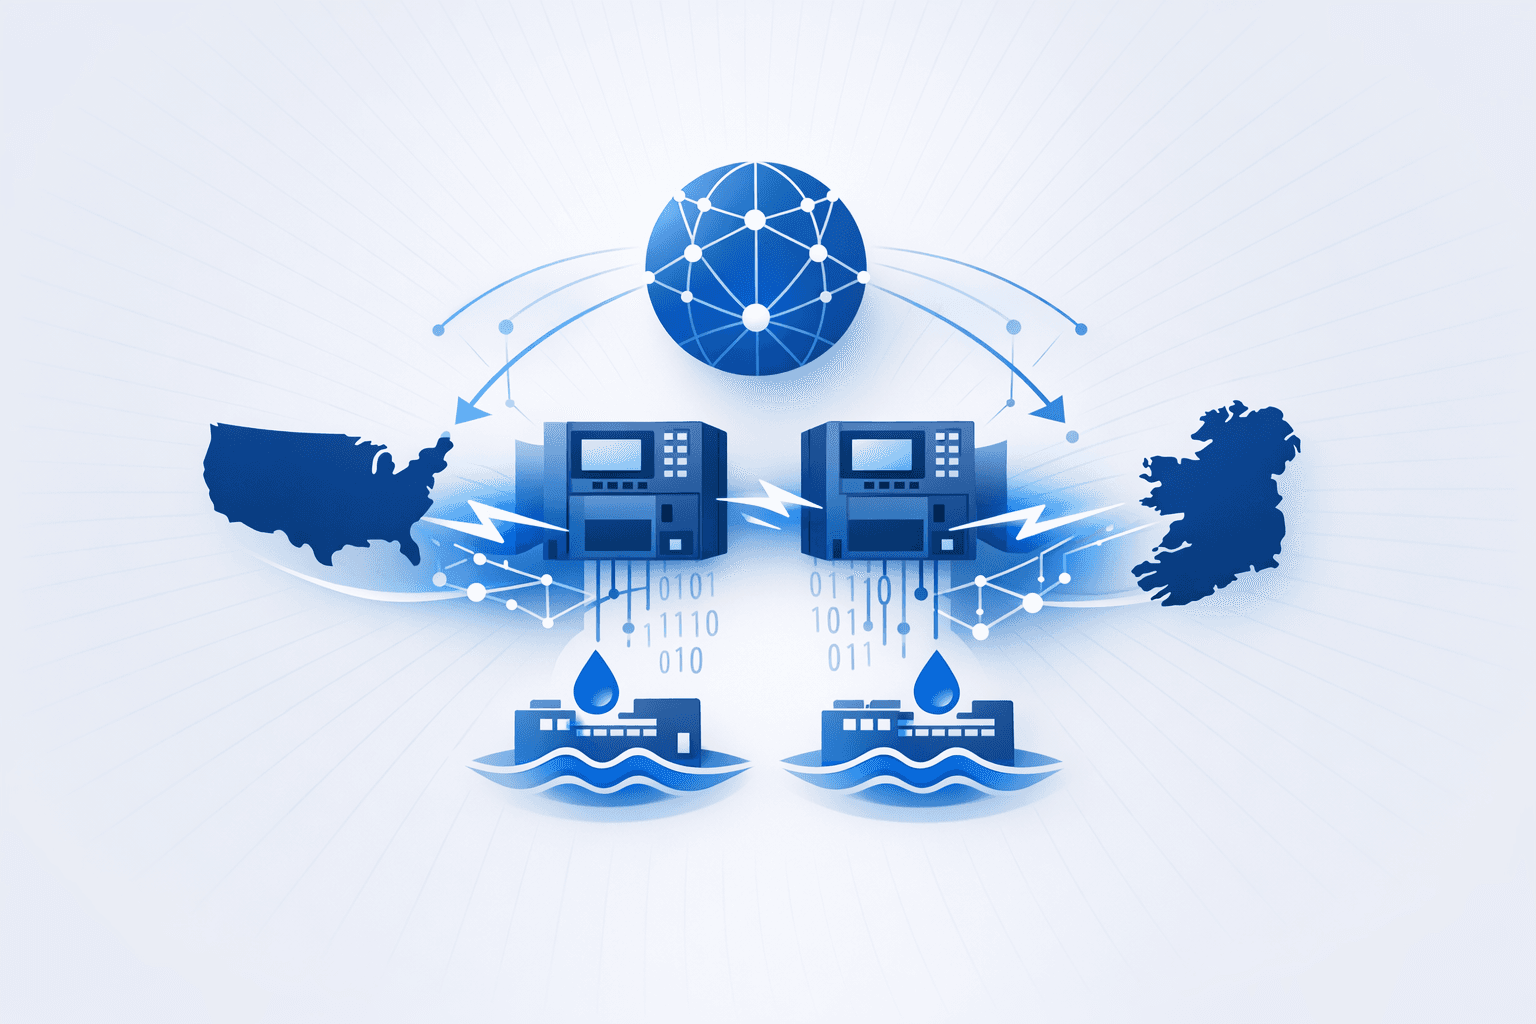
A cyberattack on the Municipal Water Authority of Aliquippa in Pennsylvania exposed a broader campaign targeting **Unitronics Vision Series PLCs** used in water and wastewater operations. Attackers linked to the pro-Iran **Cyber Av3ngers** group reportedly defaced facility screens and disrupted a remote water pressure station, prompting operators to take affected equipment offline and switch to manual or backup processes; officials said drinking water quality and core service were not affected because the compromised system was isolated from the main treatment plant. Reporting also cited a separate incident at a North Texas utility, underscoring concern that internet-exposed industrial control systems are being actively targeted across the sector. U.S. and Irish authorities later tied similar activity to exploitation of weakly secured or internet-accessible Unitronics controllers, including default or poor password practices and the vulnerability tracked as `CVE-2023-6448`, which was added to CISA's Known Exploited Vulnerabilities catalog. In Ireland, attackers disrupted water service to about 160 households in County Mayo after compromising a PLC at a private group water scheme. CISA warned water operators to remove PLCs from direct internet exposure, change default credentials, enforce multifactor authentication where possible, and back up device configurations as officials and experts warned that undersecured operational technology poses an ongoing risk to critical infrastructure.
Jun 29, 2026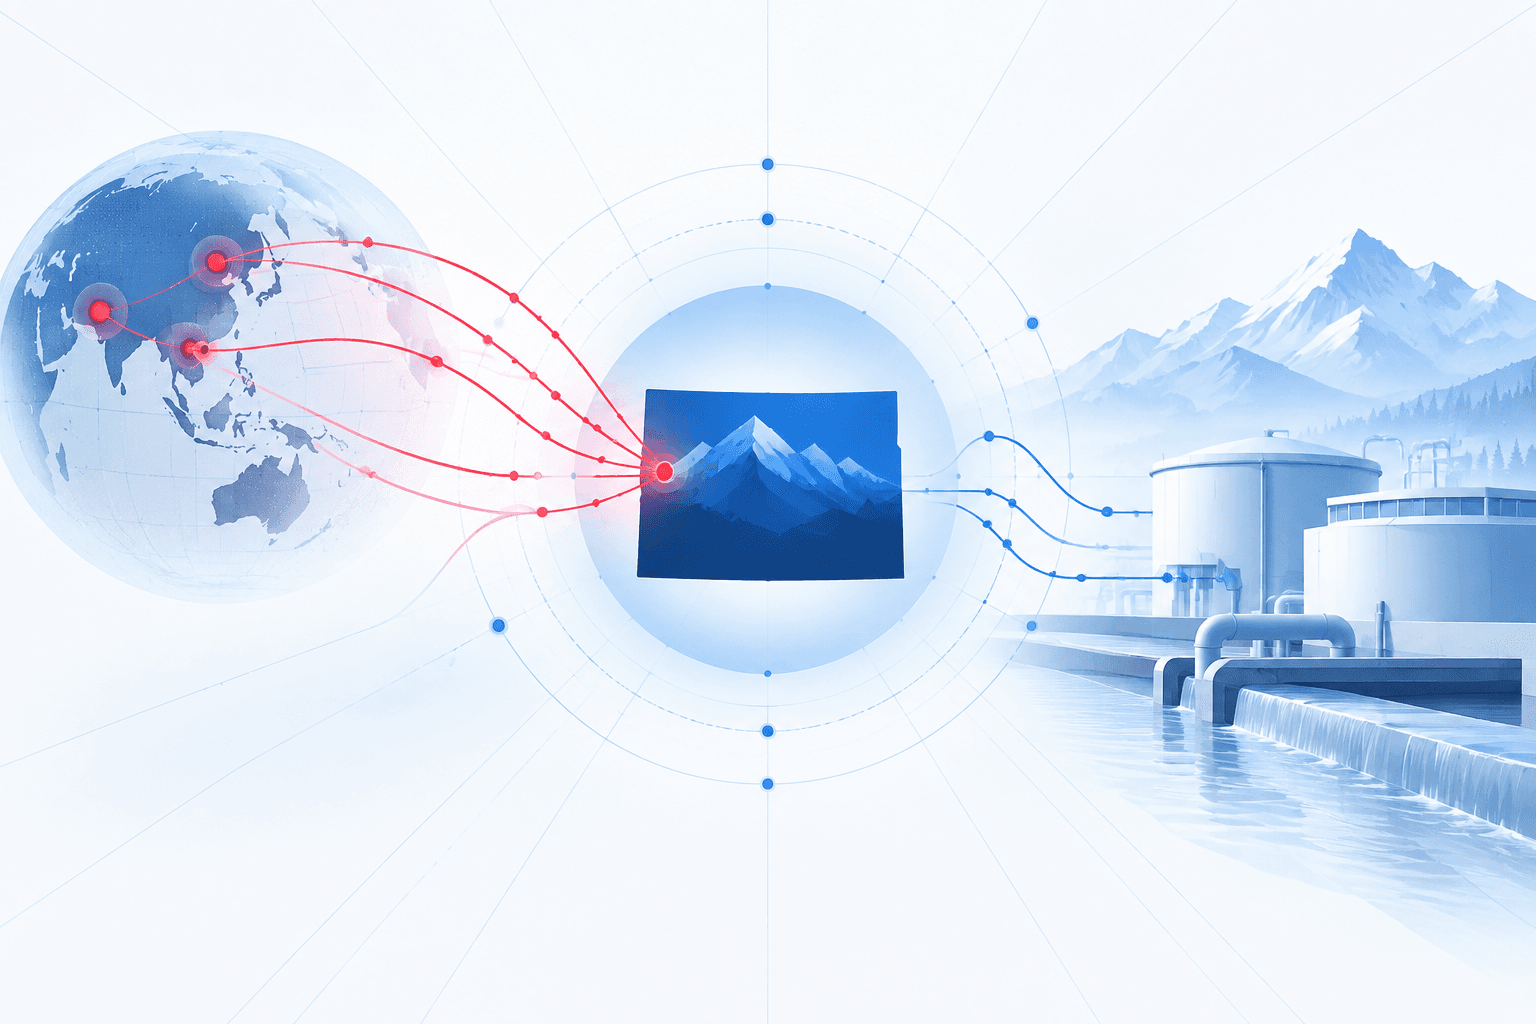
Foreign actors breached the operational technology and industrial control systems of two unnamed, privately owned Colorado water utilities in late August. Each utility serves fewer than 200 people. The intruders changed equipment settings, disabled remote access and alarms, and altered pumping cycles; disruption was brief, with no reported interruption to water service or impact on public safety. Colorado officials did not identify the perpetrators, the affected utilities, or the initial access method. They said they were aware of a broader Iranian-backed campaign targeting U.S. drinking-water and wastewater systems but did not attribute the Colorado intrusions to it. The incidents follow July attacks against roughly 100 internet-exposed water systems across at least seven states, underscoring the exposure of small utilities' internet-accessible OT environments.
Sep 24, 2026