Apache ActiveMQ RCE Exploited to Deploy Kinsing Cryptominer and Rootkits
Active Exploitation · 5 sources · Updated 2mo ago · First seen Aug 14, 2026
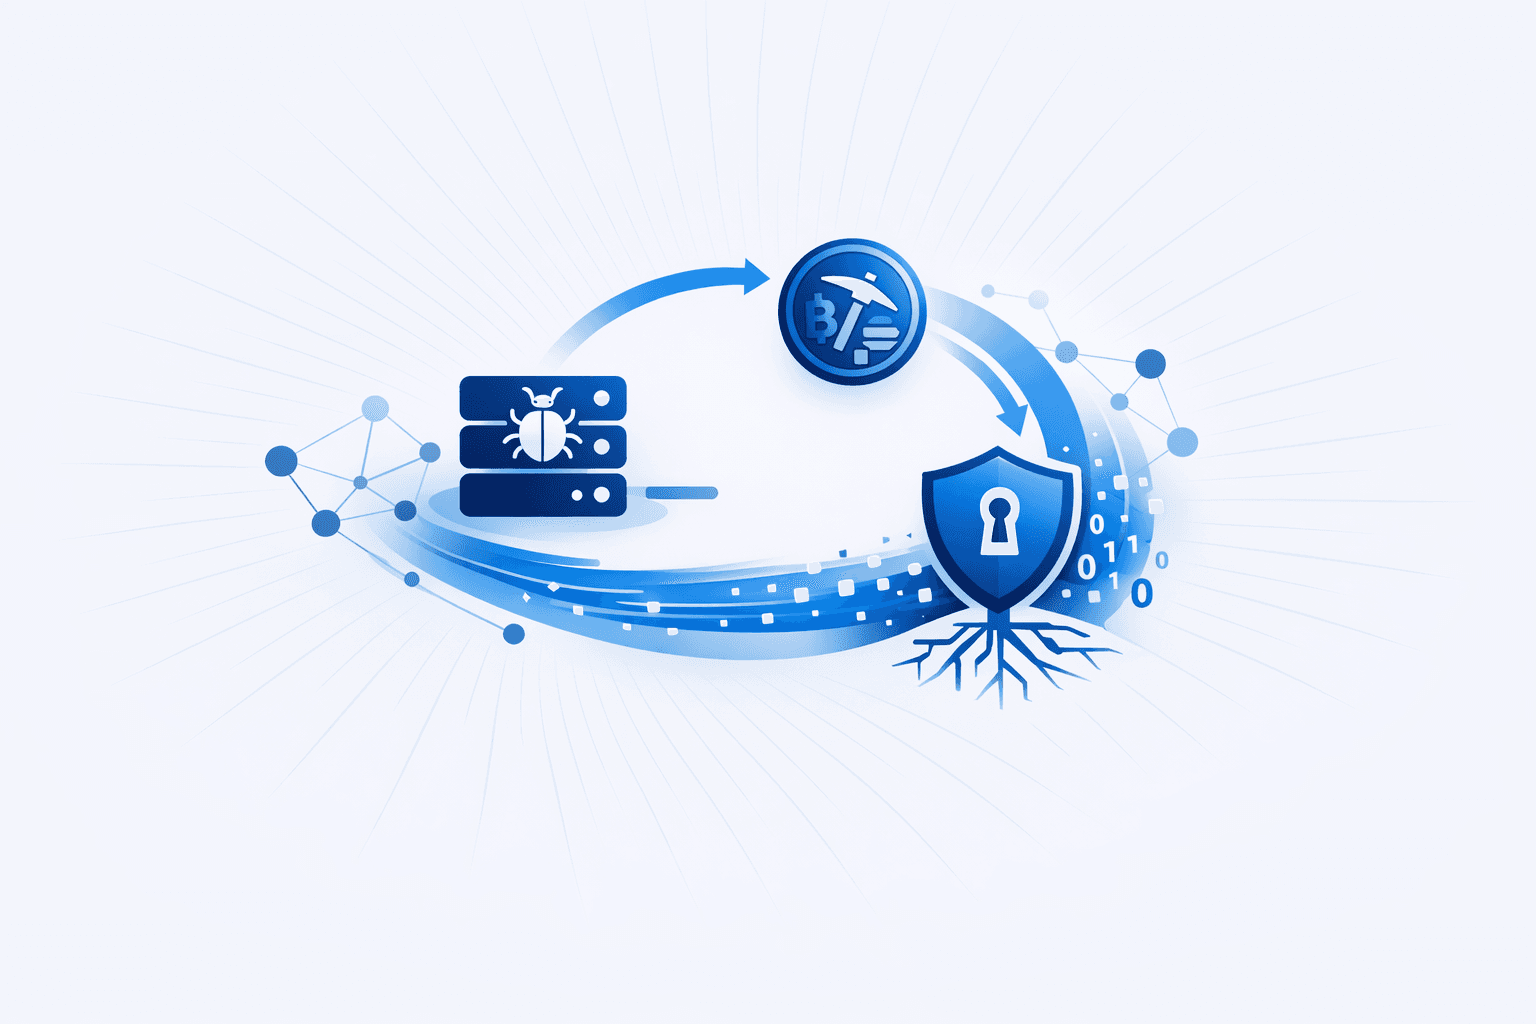
Attackers have actively exploited CVE-2023-46604, a remote code execution flaw in Apache ActiveMQ, to compromise Linux systems and install Kinsing (also known as h2miner). The vulnerability stems from improper validation of throwable class types in OpenWire commands during unmarshalling, allowing malicious code execution on exposed brokers. Trend Micro reported that intrusions led to the delivery of cryptocurrency-mining payloads and rootkit components, causing performance degradation and broader infrastructure impact.
Affected software includes multiple Apache ActiveMQ and Legacy OpenWire Module versions prior to the vendor’s patched releases. Apache addressed the issue by adding a validateIsThrowable check in the BaseDataStreamMarshall class, and organizations were urged to upgrade to 5.15.16, 5.16.7, 5.17.6, or 5.18.3 to block further exploitation and malware deployment.