Qakbot Resurfaces in Phishing Campaign Using PDF-to-MSI Infection Chain
Social Engineering & Fraud · 3 sources · Updated 3mo ago · First seen Dec 11, 2023
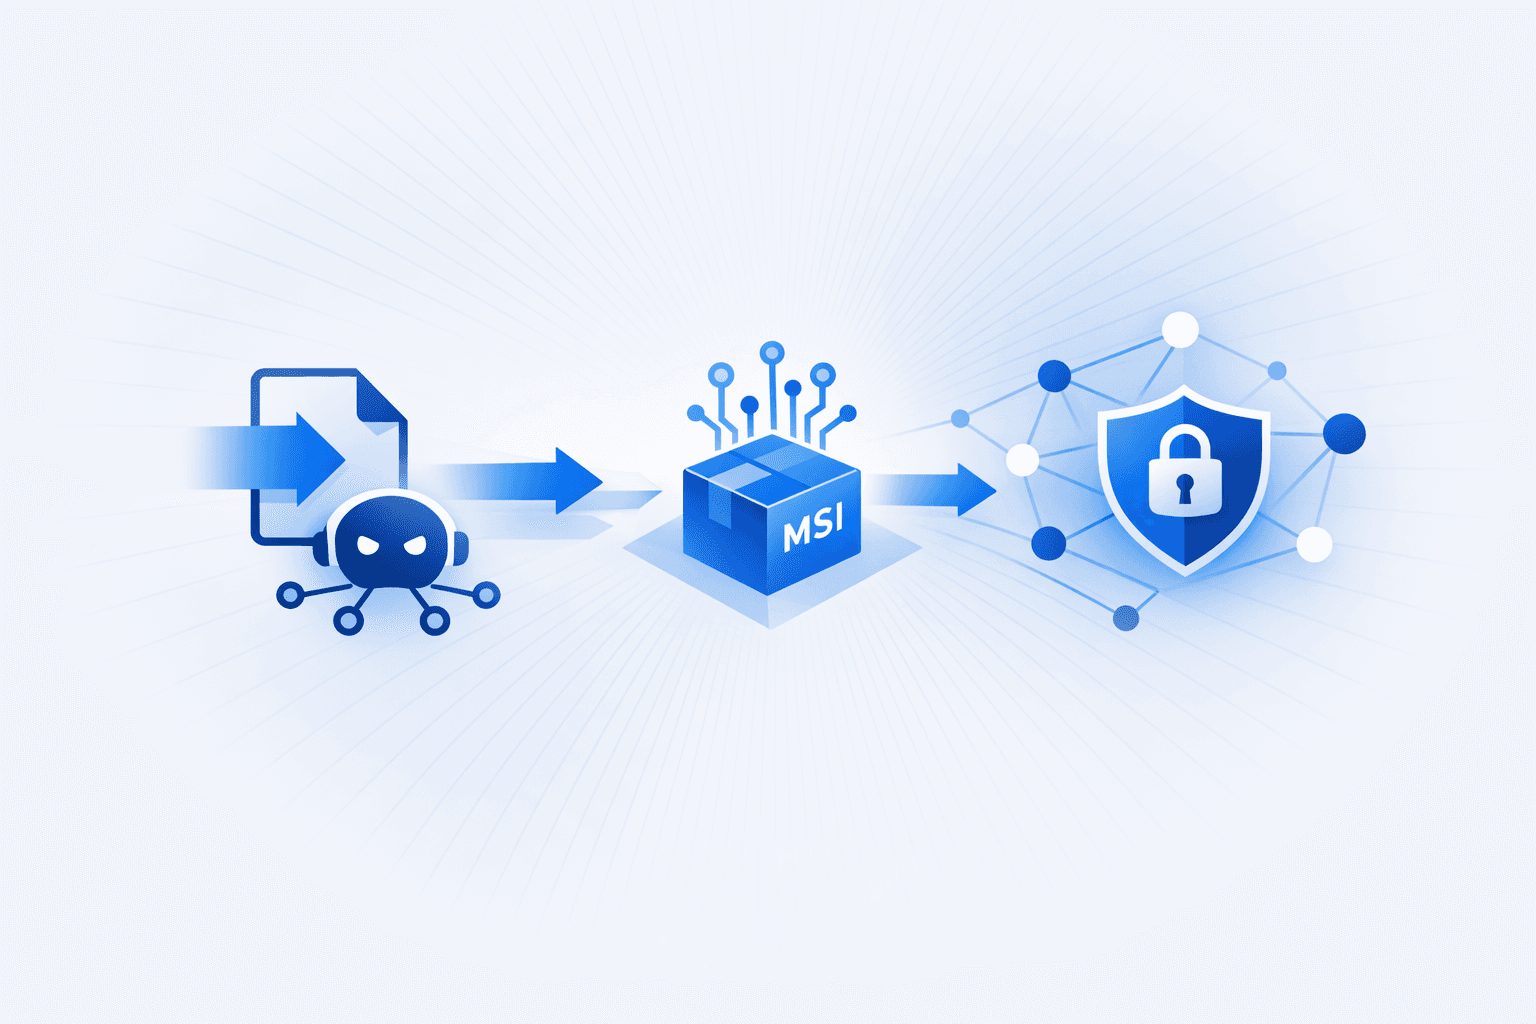
Qakbot has reappeared months after the law-enforcement-led Duck Hunt disruption, with researchers observing a new phishing campaign that targeted organizations in the hospitality sector. The activity used malicious PDF lures to deliver MSI installers containing a patched Internet Download Manager DLL and embedded Qakbot components, reviving a malware family long associated with credential theft, lateral movement, and follow-on ransomware operations.
Analysis of the new samples showed Qakbot relying on rundll32.exe, Acrobat-themed decoy behavior, and process hollowing into wermgr.exe to run its final payload from memory while attempting to evade detection. Researchers also highlighted Qakbot's continued use of RC4-encrypted Windows Registry entries to store victim identifiers and command-and-control data, a technique documented in separate analysis focused on decrypting the malware's encrypted registry keys and tracking its persistent tradecraft.