DarkWatchman RAT Delivered Through Russian-Themed Phishing Lures
Malware Intelligence · 3 sources · Updated 3mo ago · First seen Aug 14, 2026
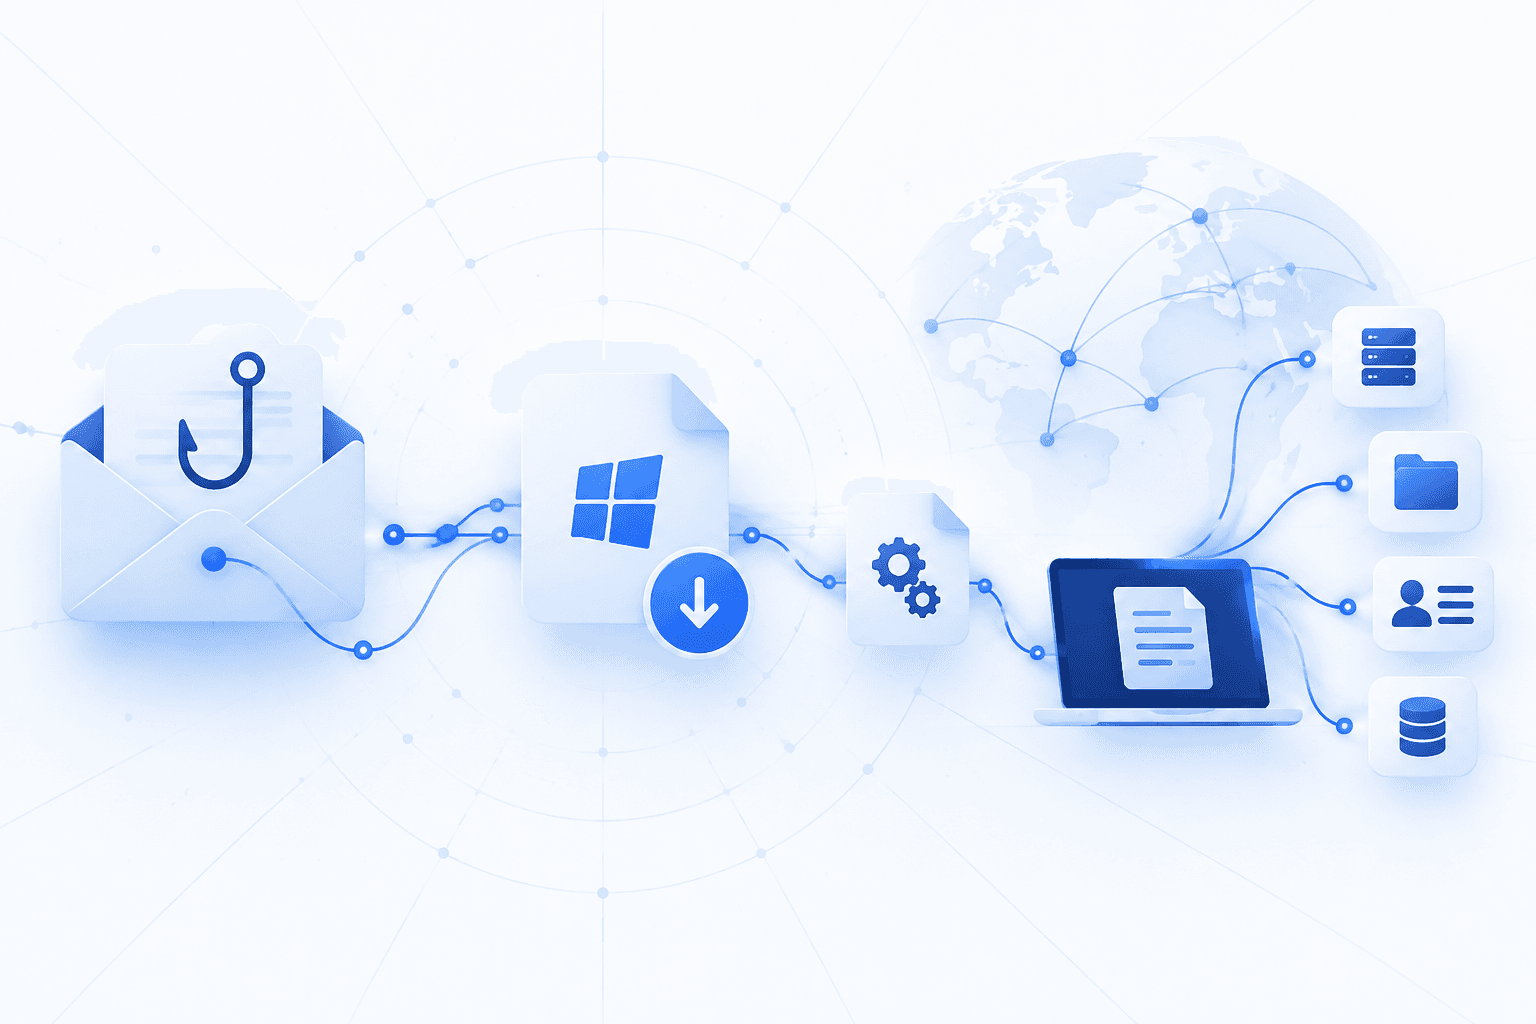
Researchers reported multiple phishing campaigns delivering the DarkWatchman remote access trojan through Russian-themed lures, including a fake CryptoPro CSP site and messages imitating military conscription summons. Victims were directed to download password-protected or self-extracting archives that launched a downloader, dropped an obfuscated JavaScript backdoor, and decrypted a PowerShell-based keylogger. The malware collected keystrokes, clipboard contents, smart card data, and host information, then exfiltrated the data to command-and-control infrastructure.
DarkWatchman stood out for storing configuration data, payload components, and stolen information in the Windows Registry rather than on disk, complicating detection and forensic recovery. The malware executed via wscript.exe, added Windows Defender exclusions, established persistence with Task Scheduler using generated task names, deleted installation artifacts, and in some cases removed volume shadow copies when running with elevated privileges. Reporting also linked the malware’s delivery and operation to heavy use of obfuscation and decryption techniques, including encrypted blobs and Base64-encoded PowerShell, consistent with MITRE ATT&CK T1140 behavior.