Hive Ransomware Used 'IPfuscation' to Hide Cobalt Strike Payloads
Threat Actor Intelligence · 3 sources · Updated 3mo ago · First seen Mar 31, 2022
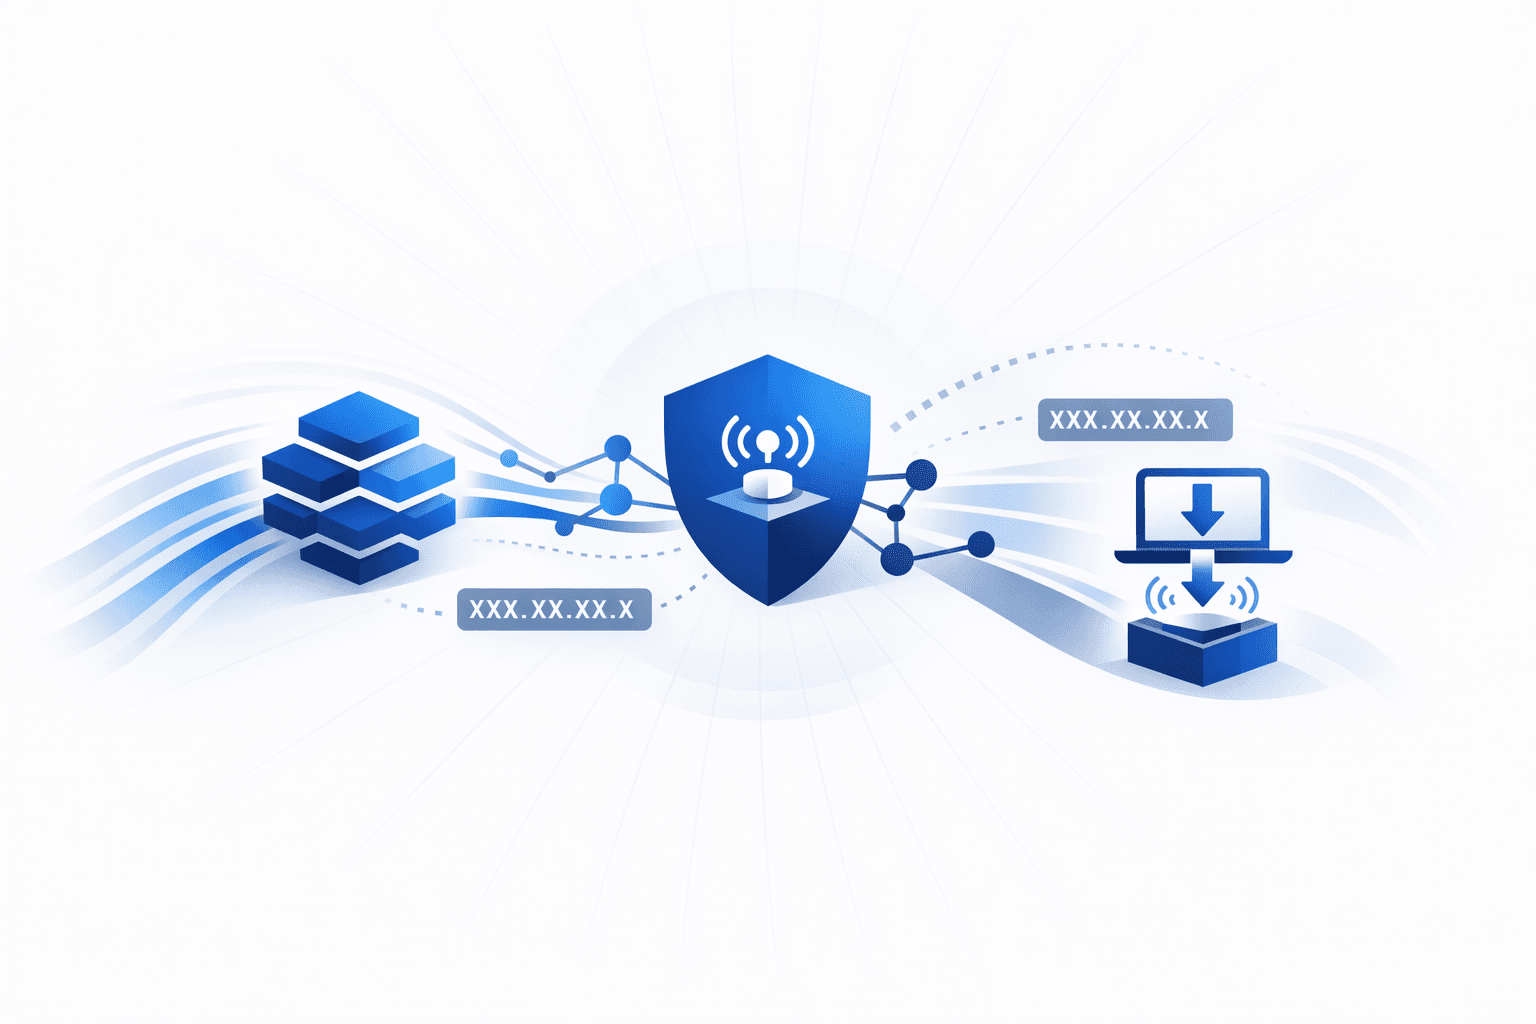
Researchers reported that Hive ransomware affiliates used a new obfuscation method dubbed "IPfuscation" to conceal malware payloads inside 64-bit Windows loaders. The technique stores shellcode as arrays of ASCII-formatted network identifiers—primarily IPv4 addresses—which are converted at runtime through Windows string-to-address APIs and then executed to launch a Cobalt Strike Beacon stager. Analysts observed execution methods including direct system calls and callback abuse through EnumUILanguagesA, making the loaders harder to detect with traditional static signatures.
Sentinel Labs also identified related variants that encoded payloads as IPv6 addresses, UUIDs, base64-encoded UUIDs, and MAC addresses, along with a Golang loader that shared development artifacts suggesting a common author. The activity aligned with known Hive intrusion tradecraft, including use of PowerShell, BAT scripts, ADFind, SharpView, BloodHound, SharpHashSpray, SharpDomainSpray, Rubeus, Group Policy Objects, and scheduled tasks. Researchers said defenders should prioritize behavioral detection, endpoint telemetry correlation, and broader security analytics over signature-only approaches, and they published malware hashes, C2 indicators, and YARA rules tied to the IPfuscation family.