
Loading story…
Proofpoint reported that the WhiteShadow downloader was being distributed through malicious Microsoft Word and Excel attachments in email campaigns, using Visual Basic macros to contact attacker-controlled Microsoft SQL Server instances over SQLOLEDB. The macros retrieved ASCII-encoded payload data from the databases, decoded it into a ZIP archive, extracted a Windows executable, and launched the next-stage malware, showing a staged delivery chain that relied on MSSQL rather than more typical web-based retrieval methods.
The campaigns were described as low- to medium-volume and were used to deliver multiple commodity malware families, including Crimson, NanoCore, njRAT, Agent Tesla, AZORult, Formbook, Orion Logger, Remcos, and Netwire. Proofpoint assessed that WhiteShadow appeared to operate as a malware delivery service built around related MSSQL infrastructure, with only basic but evolving macro obfuscation, and said defenders could use outbound TCP port 1433 traffic as a key detection and control point.

Pull IOCs and campaign context straight into your stack.
11 events from the most recent confirmed update back to the earliest known activity.
On September 26, 2019, Proofpoint published research describing WhiteShadow's use of Microsoft SQL Server databases to retrieve ASCII-encoded payloads, decode them into ZIP archives, and execute next-stage malware. The report also highlighted outbound TCP 1433 MSSQL traffic as a detection opportunity for defenders.
Proofpoint observed a further WhiteShadow campaign delivering Crimson RAT on September 24, 2019. This was the latest specifically dated Crimson delivery listed in the report.
On September 20, 2019, Proofpoint observed WhiteShadow delivering Crimson RAT and also observed NanoCore delivery that day. The activity showed concurrent use of the same delivery mechanism for different malware families.
Proofpoint observed another WhiteShadow campaign delivering Crimson RAT on September 12, 2019. The report notes no evidence linking these Crimson deliveries to prior Crimson campaigns.
Proofpoint observed a WhiteShadow campaign delivering Crimson RAT on September 9, 2019. The delivery was one of several Crimson-related events tracked across August and September 2019.
Proofpoint observed WhiteShadow campaigns delivering NanoCore between September 17 and September 18, 2019. This continued the downloader's use for multiple commodity malware payloads.
Between September 16 and September 18, 2019, Proofpoint observed WhiteShadow delivering AZORult, and between September 16 and September 17 it also delivered Formbook. These campaigns expanded the set of malware families distributed through the downloader.
Between September 2 and September 4, 2019, Proofpoint observed WhiteShadow campaigns delivering NanoCore, njRAT, Agent Tesla, and Crimson. This showed the downloader being used as a multi-malware delivery mechanism rather than for a single payload family.
Proofpoint observed another WhiteShadow campaign delivering Crimson RAT on August 29, 2019. This was part of the early run of WhiteShadow activity documented in the report.
Proofpoint observed a WhiteShadow campaign delivering Crimson RAT on August 26, 2019. The report identifies Crimson as the earliest malware family seen in the WhiteShadow campaigns.
Proofpoint researchers first observed WhiteShadow in malicious Microsoft Word and Excel attachments distributed through email campaigns beginning in August 2019. The staged downloader used Office macros to retrieve next-stage malware from attacker-controlled Microsoft SQL Server infrastructure.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 79 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
1 reference tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Multiple research reports detailed **Windows-focused malware delivery chains** that rely on social engineering and abuse of legitimate services to blend into normal enterprise traffic. FortiGuard Labs described a **multi-stage campaign targeting users in Russia** that starts with business-themed decoy documents and scripts, then escalates to security-control bypass and surveillance before deploying **Amnesia RAT** and ultimately **ransomware** with widespread file encryption. A notable technique in that intrusion is the abuse of **Defendnot** (a Windows Security Center trust-model research tool) to **disable Microsoft Defender**, while payloads are hosted modularly across public cloud services (e.g., **GitHub** for scripts and **Dropbox** for binaries) to improve resilience and complicate takedowns. Separately, ReliaQuest reported attackers using **LinkedIn private messages** to build trust with targets and deliver a **WinRAR SFX** that triggers **DLL sideloading** via a legitimate PDF reader, then establishes persistence (Registry `Run` key) and executes **Base64-encoded shellcode in-memory** to load a RAT-like payload. Trend Micro and Koi Security documented **Evelyn Stealer**, which weaponizes **malicious VS Code extensions** to drop a downloader DLL (e.g., `Lightshot.dll`), run hidden PowerShell to fetch `runtime.exe`, and inject the stealer into `grpconv.exe`, exfiltrating data (credentials, cookies, wallets, screenshots, Wi‑Fi credentials) to `server09.mentality[.]cloud` over FTP. AhnLab ASEC also reported **proxyjacking** activity in South Korea attributed to **Larva‑25012**, distributing **proxyware disguised as a Notepad++ installer** and evolving evasion (e.g., injecting into Windows Explorer and using Python-based loaders) to monetize victims’ bandwidth via unauthorized proxyware installation.
Jun 29, 2026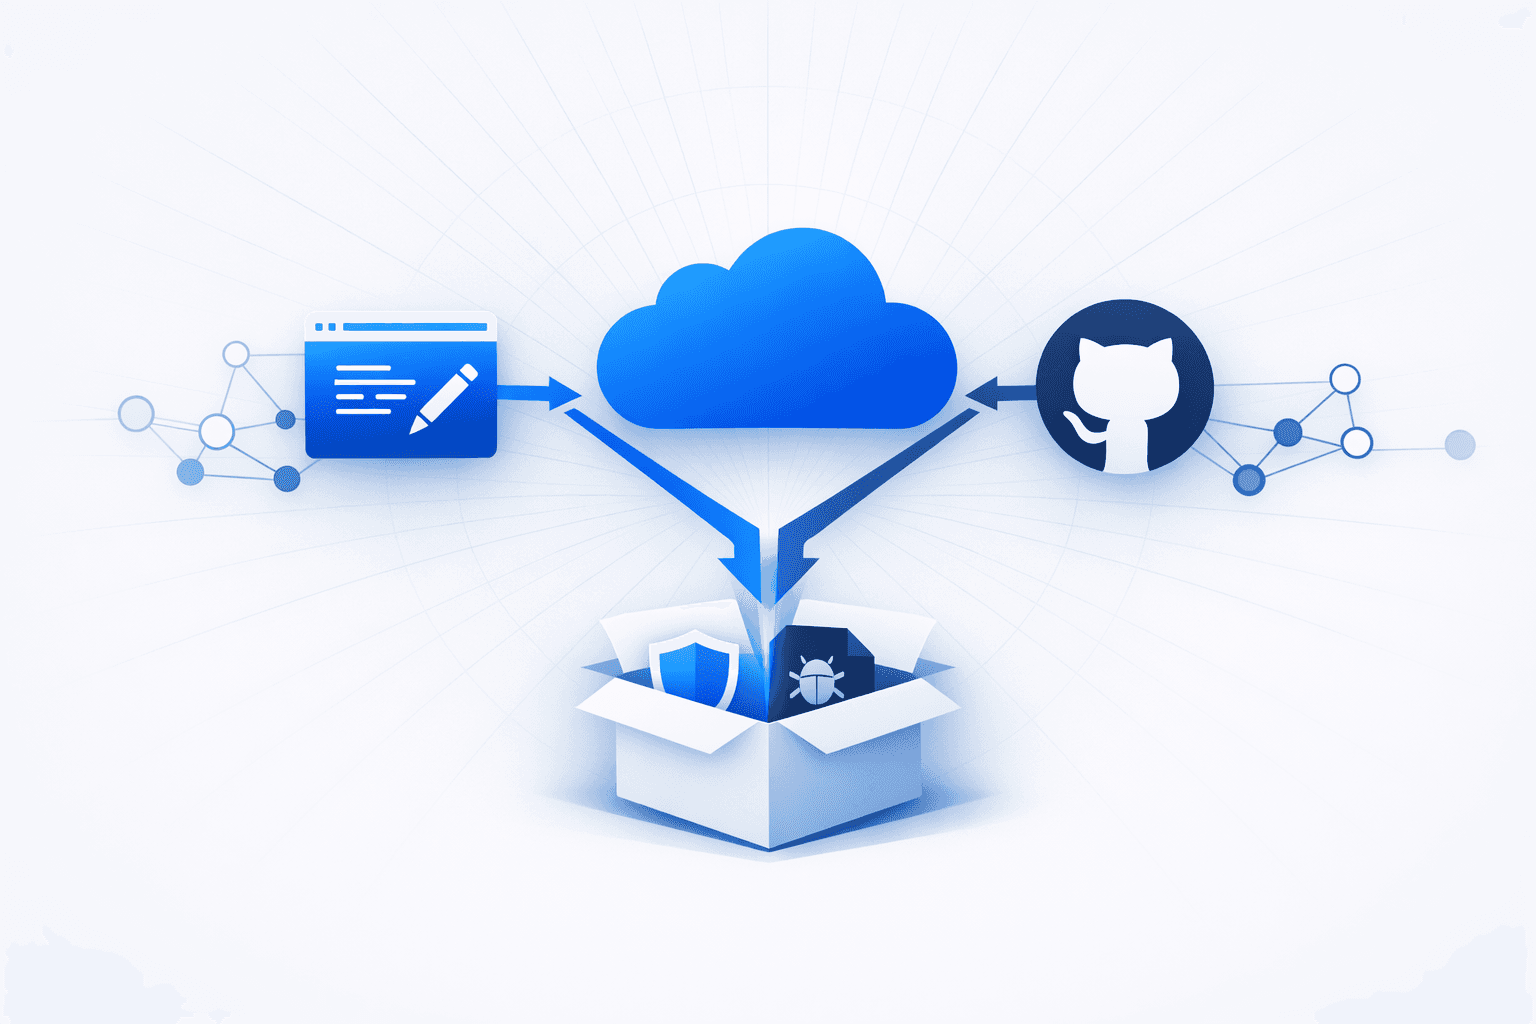
Multiple Windows-focused malware campaigns were reported leveraging *trusted distribution and execution paths* rather than exploiting software vulnerabilities. One campaign attributed to **Larva-25012** disguised proxyware as legitimate *Notepad++* installers distributed via fake cracked-software portals and deceptive ads, primarily impacting South Korea. The payloads were hosted on GitHub and delivered as MSI/ZIP packages containing legitimate components plus malicious DLLs, using **DLL side-loading** and process injection into **Windows Explorer** to deploy proxyware (e.g., **Infatica** and **DigitalPulse**) for **proxyjacking**—monetizing victims’ internet bandwidth by reselling access through their networks. A separate multi-stage Windows malware operation used business-themed lures and weaponized archives containing **LNK** shortcuts to run hidden **PowerShell** with execution-policy bypass, pulling an obfuscated loader from GitHub and using legitimate services (e.g., **Dropbox**) to blend into normal traffic. Fortinet-reported tradecraft included persistence, decoy document generation, and beaconing via the **Telegram Bot API**, followed by defense evasion through abuse of **Defendnot** to disable Microsoft Defender before dropping follow-on payloads such as ransomware, banking trojans, and surveillance tooling. Additional reporting highlighted a broader trend of attackers abusing legitimate infrastructure and admin tooling (including **RMM** software after credential theft) to establish persistent access, while generic “common threats” content provided no incident-specific intelligence.
Jun 29, 2026
A malspam campaign delivered a file named **`MT-209111.DOC`** that posed as a Word document but was actually an RTF containing four embedded Excel OLE objects. Opening the lure triggered repeated Excel macro prompts, and the embedded spreadsheet used layered obfuscation to decrypt and launch a PowerShell stage, which then decrypted and compiled obfuscated C# code in memory. The chain also attempted an **AMSI bypass** by patching memory before retrieving the next payload. The final stage downloaded an executable from **`104.244.79.123/As/MT-209111.jpg`** into the victim's **AppData** directory as **`c2ef3.exe`** and executed it. Although the payload was unavailable during analysis, corroborating data from **URLhaus** and **Any.Run** linked the downloaded file to the **AZORult** infostealer. The infection flow combined Word, Excel, OLE object auto-update behavior, PowerShell, and custom multi-layer encryption to improve the chances of successful macro execution and payload delivery.
Aug 15, 2026