Vidar Infostealer Delivered Through ISO-Packaged Microsoft CHM Help Files
Malware Intelligence · 3 sources · Updated 2mo ago · First seen Aug 14, 2026
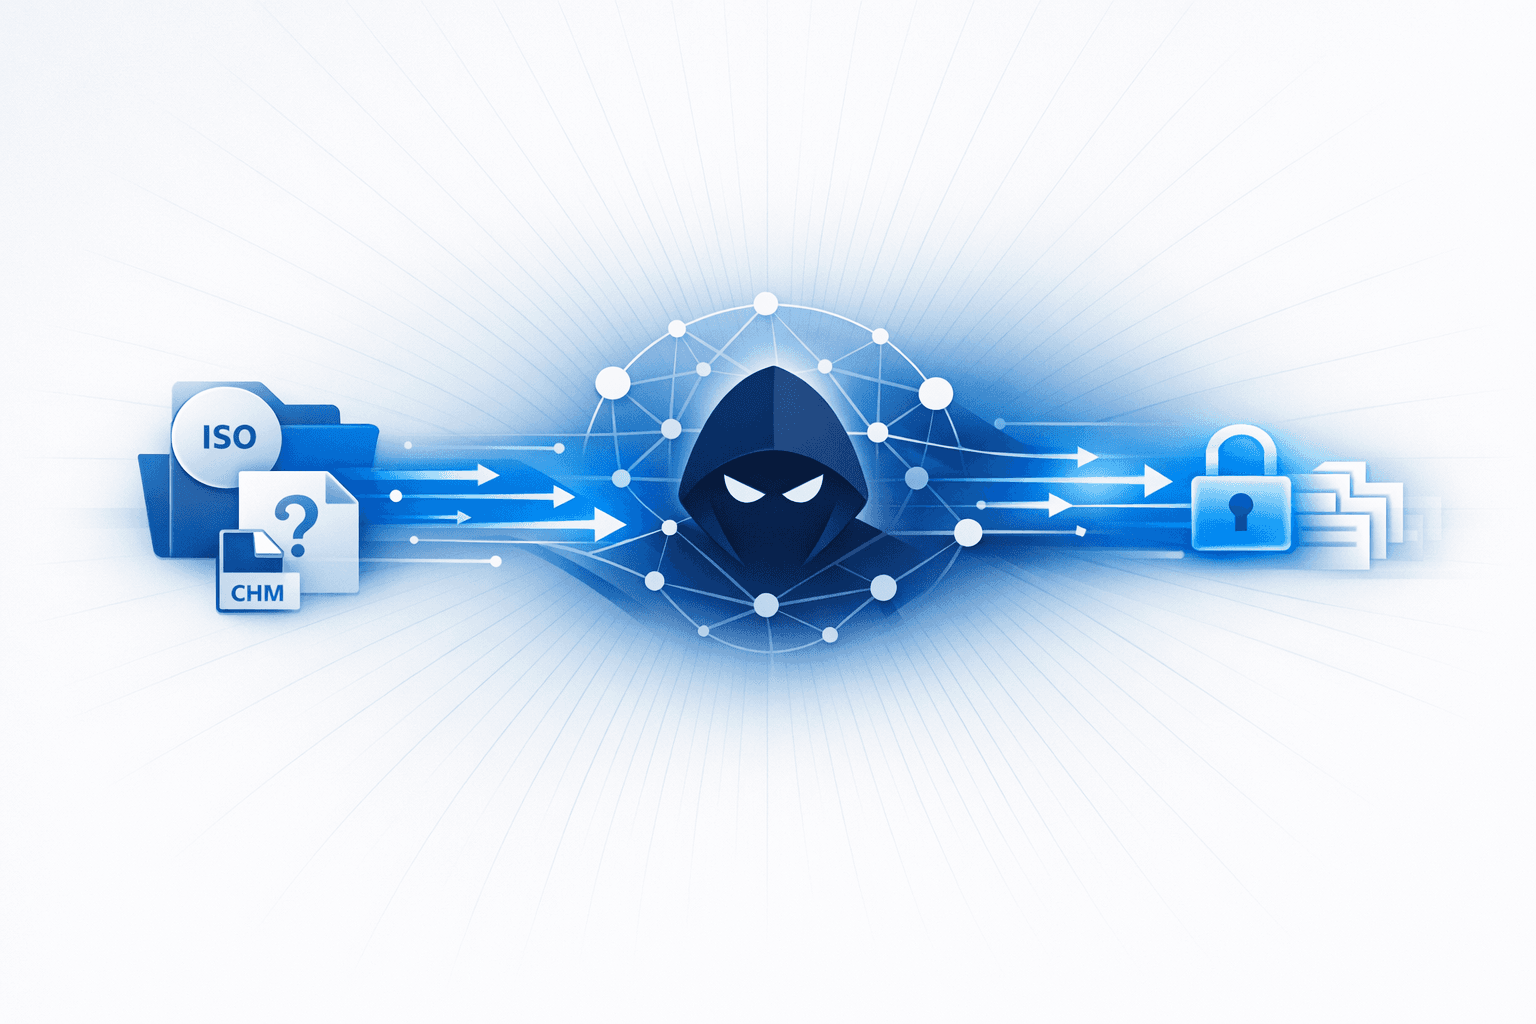
A phishing campaign distributed the Vidar infostealer through .ISO attachments containing malicious Microsoft Compiled HTML Help (.CHM) files and a payload disguised as a Word document. Researchers said the infection chain used several nested stages to obscure execution—moving from ISO to CHM to HTA/JavaScript and finally to an executable—while making the lure appear benign to users. In observed samples, a file such as pss10r.chm silently relaunched through mshta and executed app.exe, which was identified as Vidar.
The malware used Vidar version 50.3 and retrieved command-and-control directions from Mastodon profile bios before downloading configuration data from C2 servers. Once active, it collected system information, browser and application passwords, and other sensitive data including payment details and cryptocurrency wallets, then exfiltrated the information in a ZIP archive. Researchers also reported that Vidar could download additional malware and remove created files afterward to reduce forensic evidence, underscoring the campaign's focus on stealth and credential theft.