
Loading story…
Researchers detailed how the Seamless drive-by download campaign delivered the Ramnit banking trojan after filtering victims by time zone and geolocation, then redirecting selected targets to a RIG Exploit Kit landing page. The malware used a custom command-and-control protocol over TCP port 443 that mimicked secure traffic but was not HTTPS, with RC4-encrypted data chunks reportedly decodable using a stable key observed in the analyzed environment.
The analysis found that Ramnit registered infected hosts by sending two MD5 values to its command server before retrieving region-specific modules and web-inject configurations. Japan-focused infections received localized credit-card-themed web injects, while downloaded components supported antivirus interference, cookie theft, browser injection, and browser communication hooks; U.S.-targeted infections used a similar module set but could also fetch tools such as an FTP grabber and AZORult.
Pull IOCs and campaign context straight into your stack.
1 event from the most recent confirmed update back to the earliest known activity.
A published analysis documented how the Seamless campaign filtered victims by time zone and geolocation, redirected them to RIG Exploit Kit landing pages, and delivered the Ramnit banking trojan. The write-up also described Ramnit's custom TCP/443 C2 protocol, bot registration behavior, downloaded modules, and region-specific web injects.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Researchers documented **Ramnit** as a Zeus-like banking trojan, worm, and file infector that was distributed through the **Blackhole exploit kit** and equipped with rootkit capabilities, spam-sending functions, and aggressive persistence. Analysis of multiple samples showed the malware dropping several components, installing a fake **"Mi cor soft Windows Service"**, injecting into `svchost.exe`, and in some cases infecting executable and HTML files by appending malicious code. One sample was tied more closely to botnet and spam activity, while another emphasized file infection, a combination that made reliable cleanup difficult and led researchers to recommend full system rebuilds rather than partial remediation. The reporting also showed that Ramnit used resilient command-and-control methods, including communications over port `443` with a custom encoded protocol rather than SSL and large fallback domain lists to find active servers. Separate reverse engineering of the malware's **domain generation algorithm (DGA)** found that Ramnit generated variable-length `.com` domains using a simple linear congruential generator and multiple observed 32-bit seeds, including `0xEF214BBF`, `0x28488EEA`, `0x4BFCBC6A`, and `0x79159C10`. Investigators linked parts of the infrastructure to pharma spam operations, noted overlap with previously documented Ramnit C2 servers, and reported that while one command server had been sinkholed, other infrastructure remained active.
Aug 15, 2026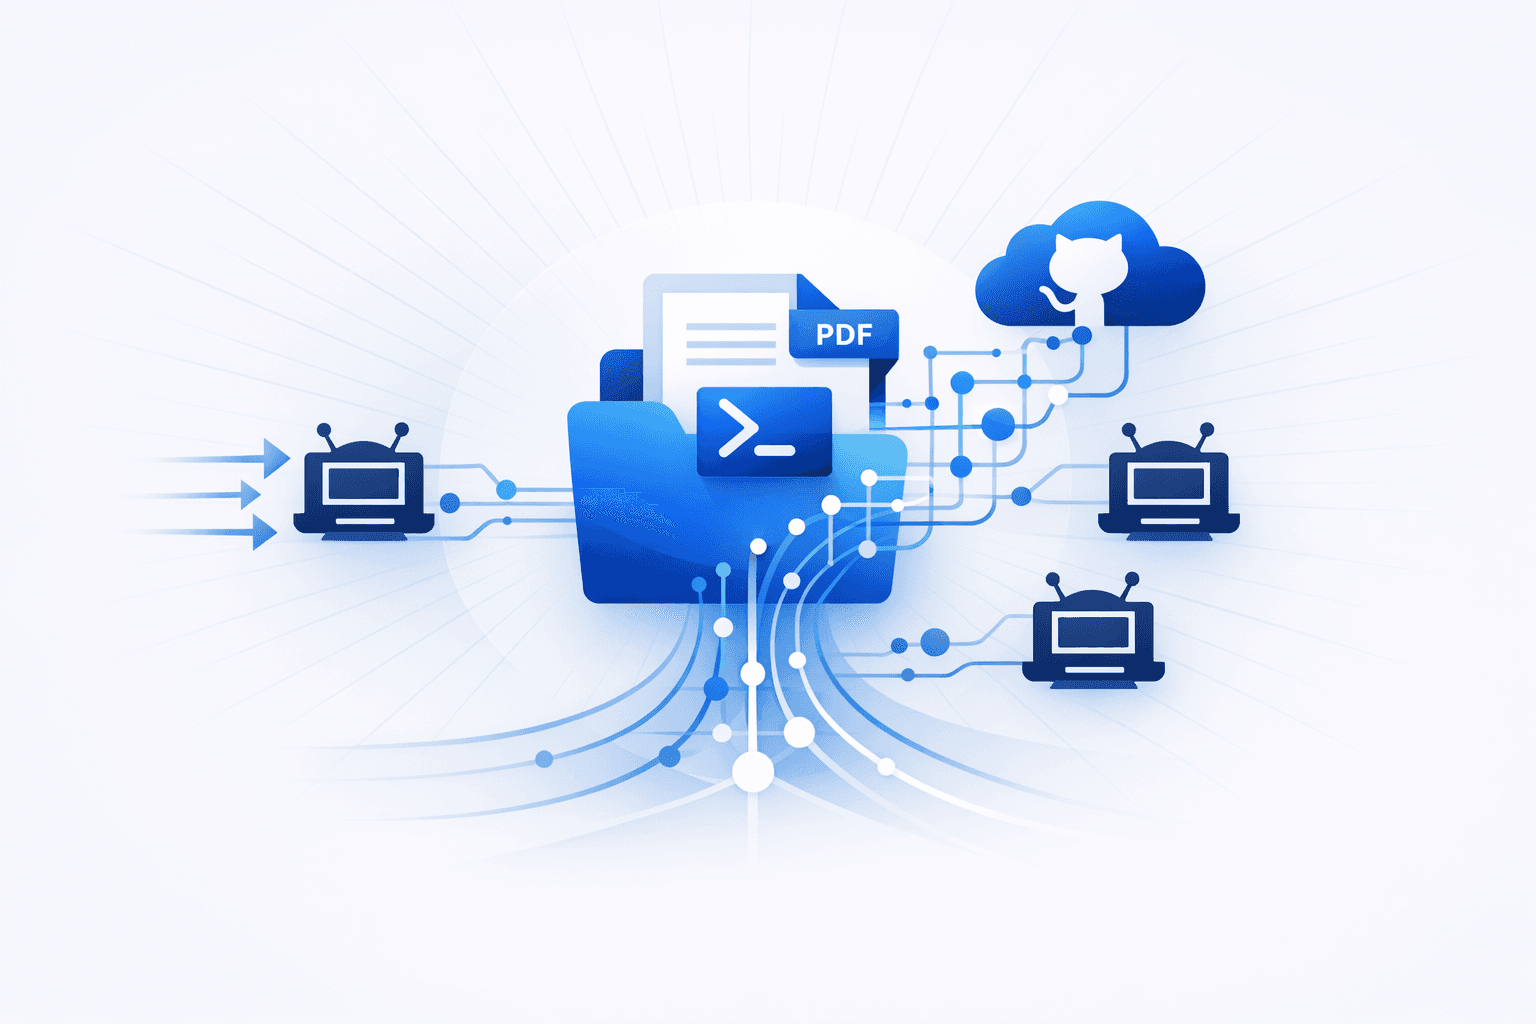
Security researchers reported several unrelated **remote access trojan (RAT)** delivery campaigns using different initial access vectors and lures. Seqrite Labs described “**Operation Covert Access**,” a spear‑phishing operation targeting Argentina’s judiciary with a ZIP attachment containing a convincing court-resolution decoy; execution is triggered by a malicious `LNK` masquerading as a PDF, which launches hidden PowerShell to fetch additional stages from a GitHub repository, culminating in a custom **Rust-based RAT** that attempts to blend in by renaming itself (e.g., `msedge_proxy.exe`). Separately, AhnLab Security Intelligence Center reported South Korea-focused activity distributing **RemcosRAT** through illegal online gambling-related tools and trojanized *VeraCrypt* installers, using embedded malicious VBS scripts and a multi-stage chain that ultimately deploys a RAT capable of surveillance and data theft (e.g., keylogging, screenshot/webcam/mic capture, credential/data harvesting). Another campaign documented by ReliaQuest abused **LinkedIn private messages** to deliver a bundled legitimate application alongside a malicious DLL for **DLL sideloading**, enabling RAT deployment under the guise of a trusted process; the reporting emphasized that social platforms can serve as effective phishing channels beyond email and that the technique is portable to other commonly used business messaging platforms.
Jun 29, 2026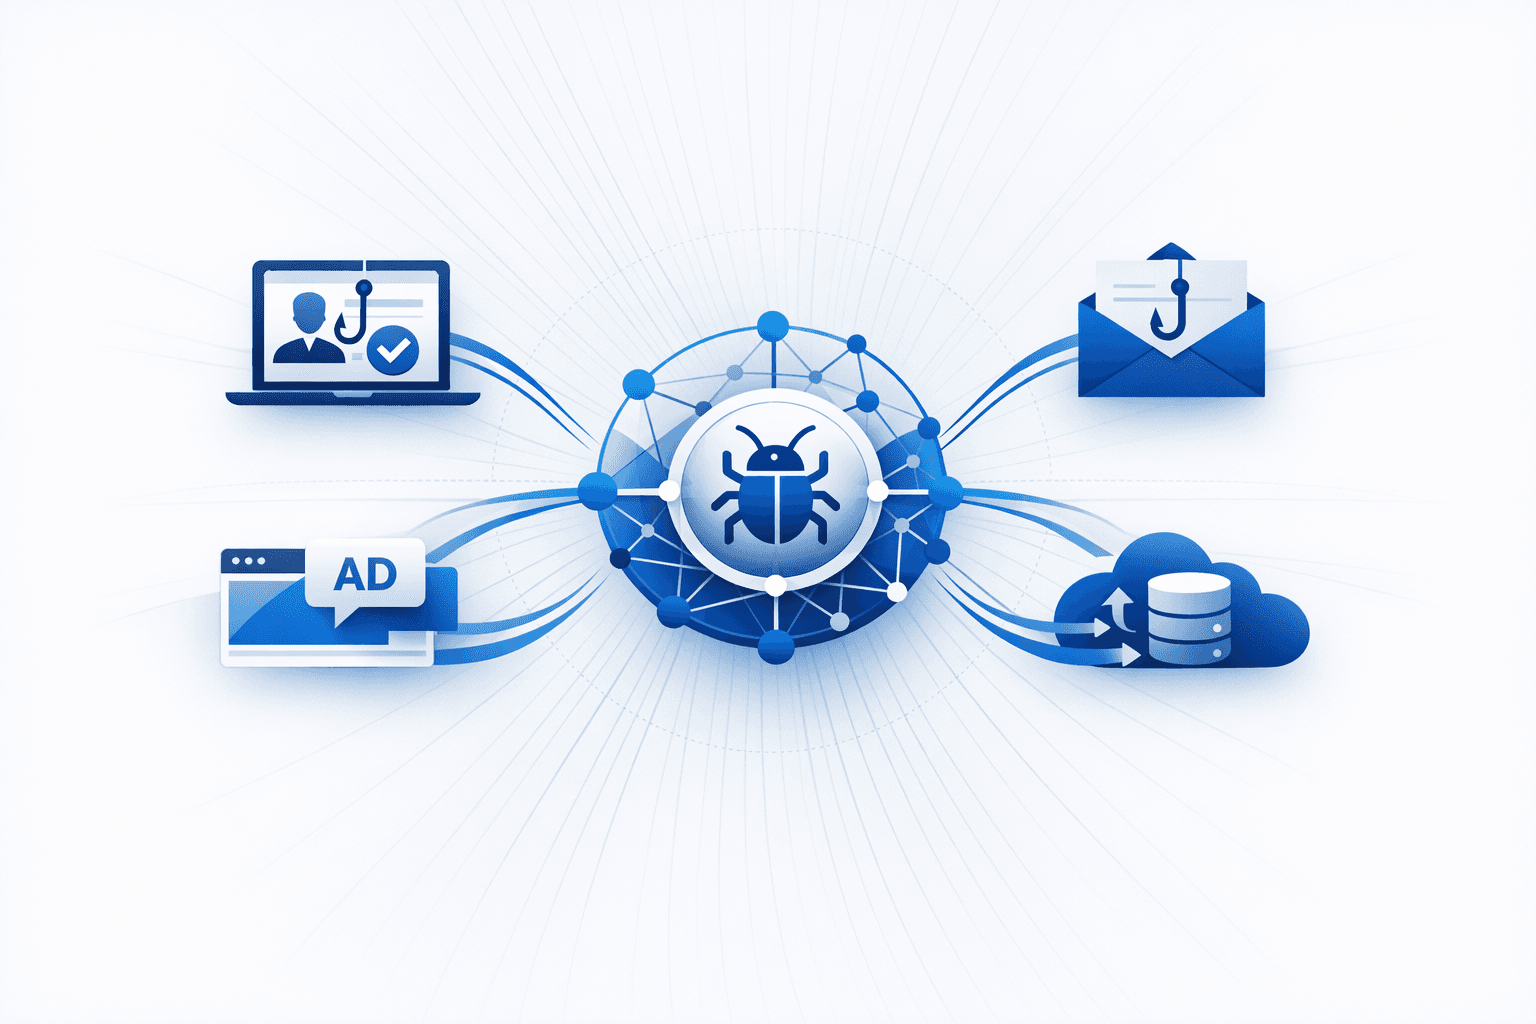
Multiple reports detail **social-engineering-driven malware delivery** that results in **remote access trojans (RATs)** and credential theft. Infoblox described observing an affiliate push-notification ad network after exploiting misconfigured DNS delegations (“**Sitting Ducks**”/lame name server delegation) to take over abandoned threat-actor domains, allowing collection of **~57M logs** over two weeks and visibility into widespread **scams and brand impersonation** delivered via push ads. Nextron Systems separately reported recurring **malvertising** chains where “free converter” tools (e.g., document/image converters) downloaded from ads on legitimate sites function as advertised while covertly installing **persistent RATs**, with common artifacts such as Windows **Mark-of-the-Web** (`ZoneId=3`) indicating internet origin. Other activity in the set reflects different initial-access lures but the same general outcome—RAT-style access and data theft. Fortinet analyzed a **phishing** campaign using a fake Vietnam shipping document: a Word attachment leads to an RTF stage that exploits an RTF-related vulnerability, then uses **VBScript/PowerShell** to load a **fileless .NET module**, ultimately downloading and injecting a **Remcos** variant (including process hollowing) to provide full remote control. Separately, reporting on North Korea’s **“Contagious Interview”** campaign described fake recruiter outreach (e.g., via LinkedIn) that tricks developers into opening malicious code repositories; execution can be triggered via a hidden **VS Code `tasks` configuration**, server-side logic hooks, or a malicious npm dependency to steal credentials/crypto wallets and establish persistence—this is thematically similar (social engineering leading to remote access) but is a distinct operation from the malvertising/push-ad and Remcos phishing activity.
Jun 29, 2026