Mallory
← Back to News
credential-stealer-activityphishing-campaign-intelligenceloader-delivery-mechanismdefense-evasion-method

XLoader Campaigns Use SharePoint Lures and CVE-2017-11882 to Deliver Formbook

Malware Intelligence · 3 sources · Updated 3mo ago · First seen Jan 1, 2026
XLoader Campaigns Use SharePoint Lures and CVE-2017-11882 to Deliver Formbook

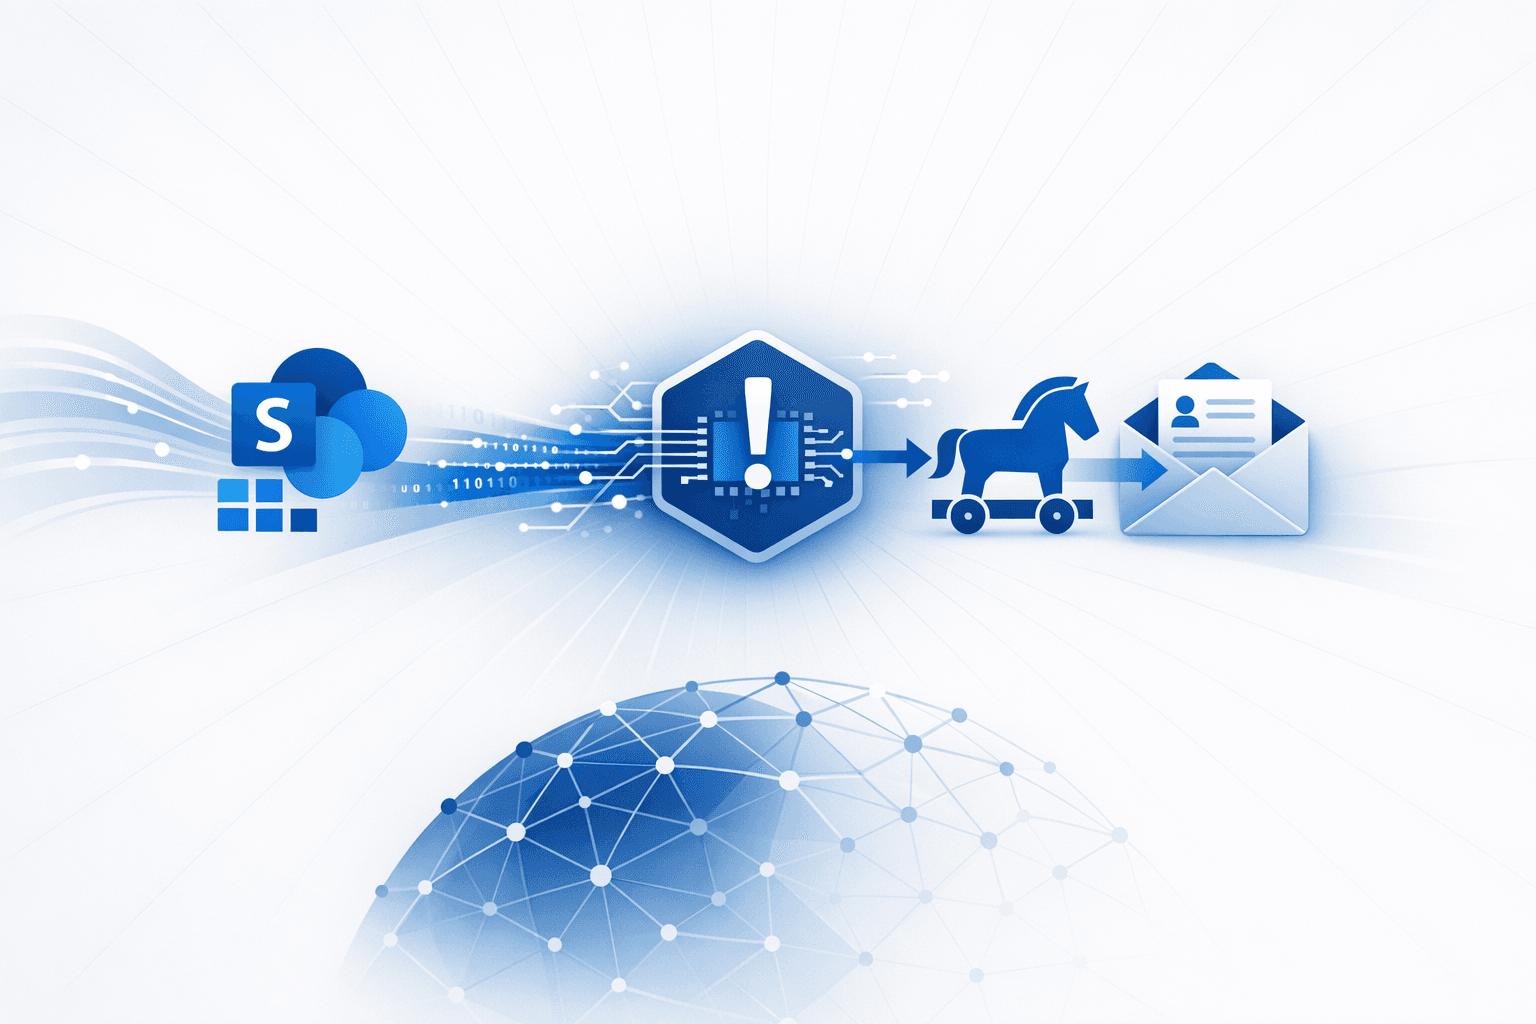
Researchers documented multiple XLoader/Formbook delivery chains that used different initial access methods but converged on the same information-stealing malware. One campaign used spam emails with PDF attachments that led victims through embedded XLSX and downloaded RTF files, while another impersonated SharePoint to push users to a malicious ZIP archive. A separate Excel-based campaign exploited CVE-2017-11882 in Microsoft Equation Editor (EQNEDT32.exe) through a malicious OLE object, triggering shellcode that downloaded and launched additional malware from attacker-controlled infrastructure.

Across the campaigns, the loaders relied on layered obfuscation, in-memory execution, and repeated process injection before deploying the final XLoader payload. Analysts observed AutoIT-based loaders, anti-analysis delays, CRC32 API hashing, shellcode injection into processes including svchost.exe, netsh.exe, and explorer.exe, and payload components hidden in bitmap resources and unpacked with steganography or decompression routines. The final malware established persistence through HKCU Run keys and shortcut artifacts, used process hollowing, and stole credentials, cookies, keystrokes, clipboard contents, and screenshots while maintaining command-and-control channels that could fetch additional payloads or remove the malware.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

3 events · Jul 1, 2022 – Jan 1, 2026
  1. Jan 1, 202611mo ago

    Sublime blocks SharePoint-themed phishing delivering Xloader

    Sublime analyzed and blocked a phishing email impersonating SharePoint that linked to a ZIP archive containing an AutoIT executable. The researchers assessed with high confidence that the final payload was XLoader/Formbook and with moderate confidence that the initial loader components were related to TrickGate, based on shellcode behavior, API hashing, staged injection, and PKT2-related C2 strings.

    Xloader deep dive: Link-based malware delivery via SharePoint impersonation · Blog · Sublime Security
  2. Sep 19, 20224y ago

    Fortinet analyzes Excel exploit chain tied to Formbook delivery

    FortiGuard Labs reported a malicious Excel file, "GAT412-IFF22.xlsx," that auto-loaded an embedded OLE object and exploited CVE-2017-11882 in EQNEDT32.EXE to download and run a payload from lutanedukasi[.]co[.]id. The report also described a related Delphi-based Formbook loader that used a bitmap resource, Discord CDN payload retrieval, process hollowing, and Run-key persistence.

    Excel Document Delivers Multiple Malware By Exploiting CVE-2017-11882 - Part I | Fortinet Blog
  3. Jul 1, 20224y ago

    Cyble documents multistage Xloader phishing campaign

    Cyble Research Labs analyzed a spam-driven infection chain in which a malicious PDF dropped an XLSX file that fetched an RTF exploiting CVE-2017-11882 to deliver Xloader. The report detailed the .NET loader stages, steganography in a bitmap resource, process hollowing, persistence, and Xloader's credential theft and C2 capabilities.

    Cyble - Xloader Returns With New Infection Technique
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Observables

117 linked

Indicator values are masked on this page. View all 117 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.