Tor-Based Linux Botnet Spreads via Ansible, Chef, and SaltStack to Deploy XMRig
Malware Intelligence · 1 source · Updated 3mo ago · First seen Apr 22, 2021
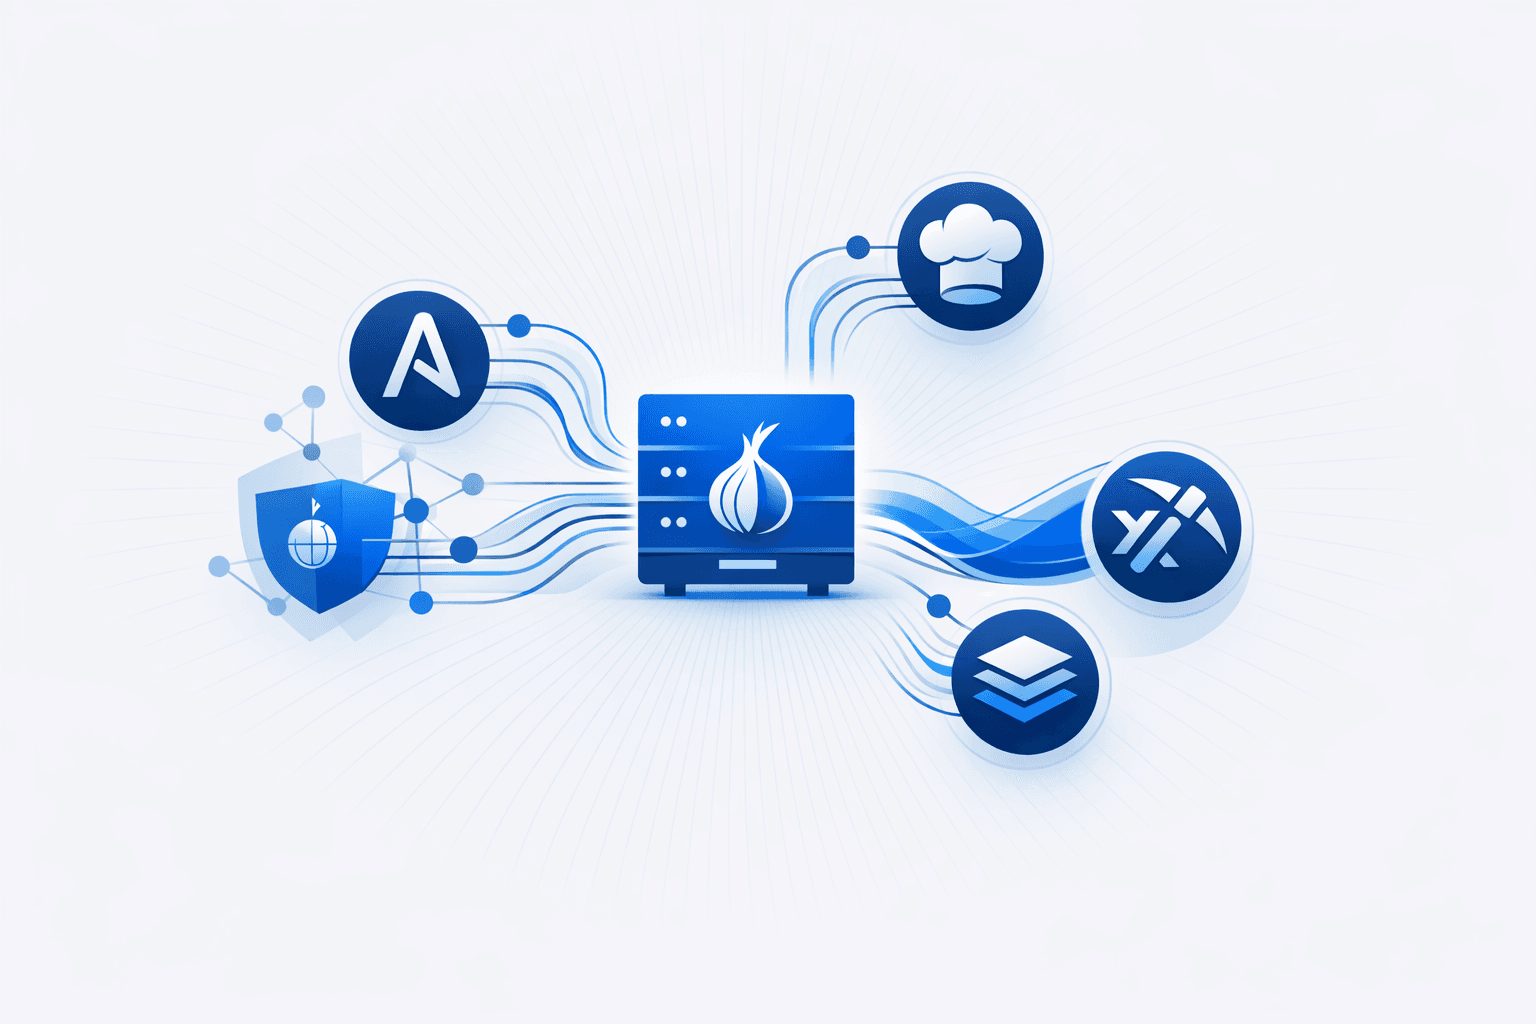
A Linux-focused botnet used the Tor network and a large proxy infrastructure to conceal command-and-control traffic, deliver payloads, and exfiltrate victim data while deploying the XMRig Monero miner on compromised systems. The malware arrived as a multilayer-encoded shell script, supported multiple Linux architectures, and fetched legitimate utilities such as ss, ps, and curl when they were not already present, indicating an effort to operate flexibly across diverse server environments.
The campaign also abused infrastructure-as-code and cloud management tools including Ansible, Chef, and SaltStack to expand laterally and scale infections. Once active, the malware removed rival cryptominers and disabled or uninstalled cloud monitoring and security agents tied to Tencent Cloud, Alibaba Cloud, and Aegis/YunJing, while researchers found evidence suggesting some Tor proxy and mining-pool servers used in the operation may themselves have been compromised hosts with exposed and vulnerable services.