Mallory
← Back to News
actively-exploited-vulnerabilityinternet-facing-service-vulnerabilitywidely-deployed-product-advisoryproof-of-concept-release

ProxyNotShell Exploitation Hit Microsoft Exchange Servers

Active Exploitation · 4 sources · Updated 3mo ago · First seen Oct 3, 2022
ProxyNotShell Exploitation Hit Microsoft Exchange Servers

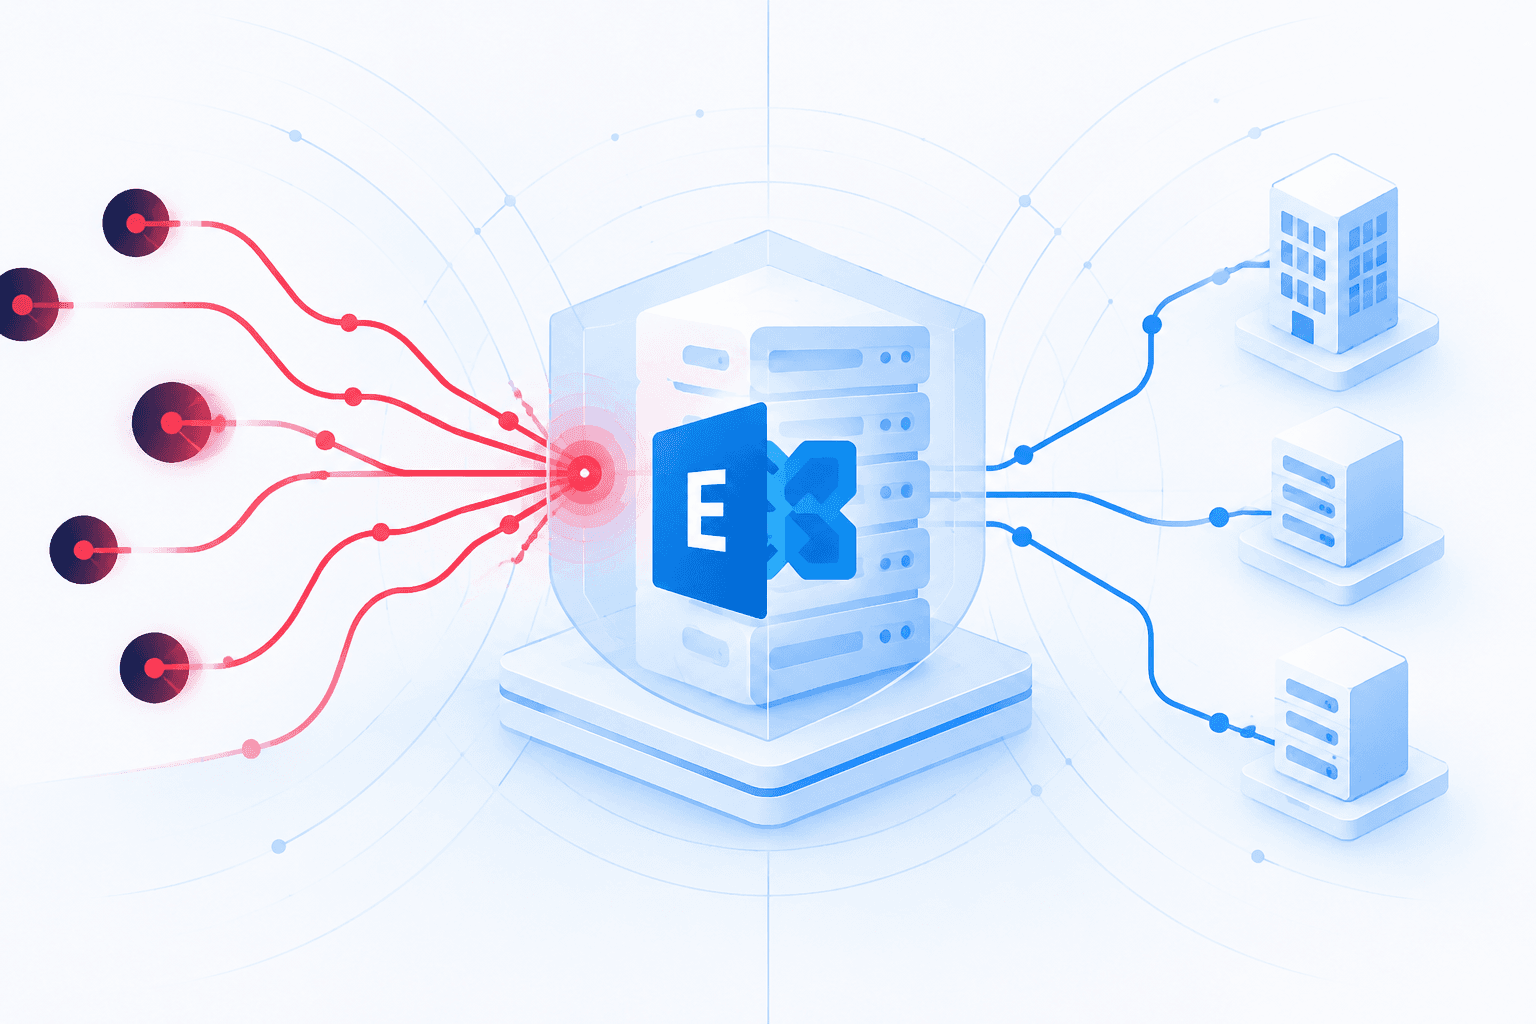
Attackers actively exploited the Microsoft Exchange Server vulnerabilities CVE-2022-41040 and CVE-2022-41082, widely known as ProxyNotShell, to gain remote code execution on vulnerable on-premises deployments. Microsoft disclosed the attacks and analyzed the exploit chain, which abuses the two flaws together, while affected products included supported Exchange Server 2013, 2016, and 2019 cumulative update versions; Exchange Online was not affected.

Security monitoring in the weeks after disclosure showed sustained scanning and exploitation attempts, with one SOC reporting activity beginning on October 3 and continuing intermittently through November, and more than 90% of observed source countries tied to the United States. Many requests appeared to use the ZGrab scanning tool based on User-Agent headers, and public proof-of-concept code increased the likelihood of continued abuse. Microsoft released patches for affected Exchange versions, and organizations running on-premises Exchange were urged to apply the vendor fixes without delay.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events · Sep 30, 2022 – Nov 2022
  1. Reported Dec 15, 20224y ago

    Microsoft releases remediated Exchange versions

    Microsoft released remediated versions for affected Exchange Server 2013, 2016, and 2019 cumulative update branches. The fixes addressed the on-premises products listed as affected, while Exchange Online was noted as unaffected.

    2022年11月度 MBSD-SOCの検知傾向トピックス | 技術者ブログ | 三井物産セキュアディレクション株式会社
  2. Nov 2022

    MBSD-SOC reports increased ProxyNotShell attacks in November

    MBSD-SOC reported increased attack activity during November 2022 targeting the Exchange vulnerabilities CVE-2022-41040 and CVE-2022-41082. It said detections continued intermittently after the initial October observations, with more than 90% of observed source countries identified as the United States.

    2022年11月度 MBSD-SOCの検知傾向トピックス | 技術者ブログ | 三井物産セキュアディレクション株式会社
  3. Oct 3, 20224y ago

    MBSD-SOC begins observing ProxyNotShell attack activity

    MBSD-SOC reported first observing attacks targeting CVE-2022-41040 and CVE-2022-41082 on October 3, 2022. The observed requests targeted Exchange autodiscover paths and many appeared to use the ZGrab scanning tool.

    2022年11月度 MBSD-SOCの検知傾向トピックス | 技術者ブログ | 三井物産セキュアディレクション株式会社
  4. Sep 30, 20224y ago

    Microsoft discloses Exchange ProxyNotShell vulnerabilities

    Microsoft publicly disclosed CVE-2022-41040 and CVE-2022-41082 affecting on-premises Microsoft Exchange Server. The chained vulnerabilities, later widely referred to as ProxyNotShell, can enable remote code execution.

    2022年11月度 MBSD-SOCの検知傾向トピックス | 技術者ブログ | 三井物産セキュアディレクション株式会社
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →
Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.