
Loading story…
The FBI’s Internet Crime Complaint Center warned that an ongoing OAuth consent-phishing campaign has targeted prominent individuals, their relatives, and personal contacts since late 2025. Attackers impersonate government officials, journalists, public figures, event coordinators, and other trusted contacts through a commercial messaging application, directing targets to authorize malicious applications posing as file-sharing, cloud-storage, or identity-verification services.
Victims authenticate on legitimate Microsoft or Google pages, but approving the requested OAuth permissions grants attackers persistent token-based access to email, files, and other sensitive cloud data without stealing passwords. This access can bypass password-based protections and MFA and remains active after a password reset; affected users must revoke the malicious application authorization or invalidate its token in account security settings. The FBI advised independently verifying unexpected messages and authorizing only trusted applications.
Get the infrastructure and lures behind it.
3 events from the most recent confirmed update back to the earliest known activity.
Attackers began an OAuth consent-phishing campaign targeting prominent individuals, their relatives, and personal contacts. They impersonated trusted figures and used malicious OAuth applications to obtain persistent access to email, files, and other account data without stealing passwords.
The FBI warned that Kali365, a phishing-as-a-service platform, targets Microsoft 365 users by persuading them to enter attacker-supplied device codes in Microsoft's legitimate OAuth device-authentication flow. Completing the flow can authorize attacker access and enable OAuth token capture without victims submitting credentials to a fake login page.
The FBI and its Internet Crime Complaint Center issued a public warning about the ongoing campaign, advising recipients to independently verify unfamiliar contacts, authorize only trusted applications, and revoke malicious OAuth authorizations through account security settings.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
6 references tracked. Mallory keeps watching after this page renders.
infosec.pub
Open sourcewaterisac.org
Open sourcehelpnetsecurity.com
Open sourcecyberscoop.com
Open sourceic3.gov
Open sourcecloudsecurityalliance.org
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
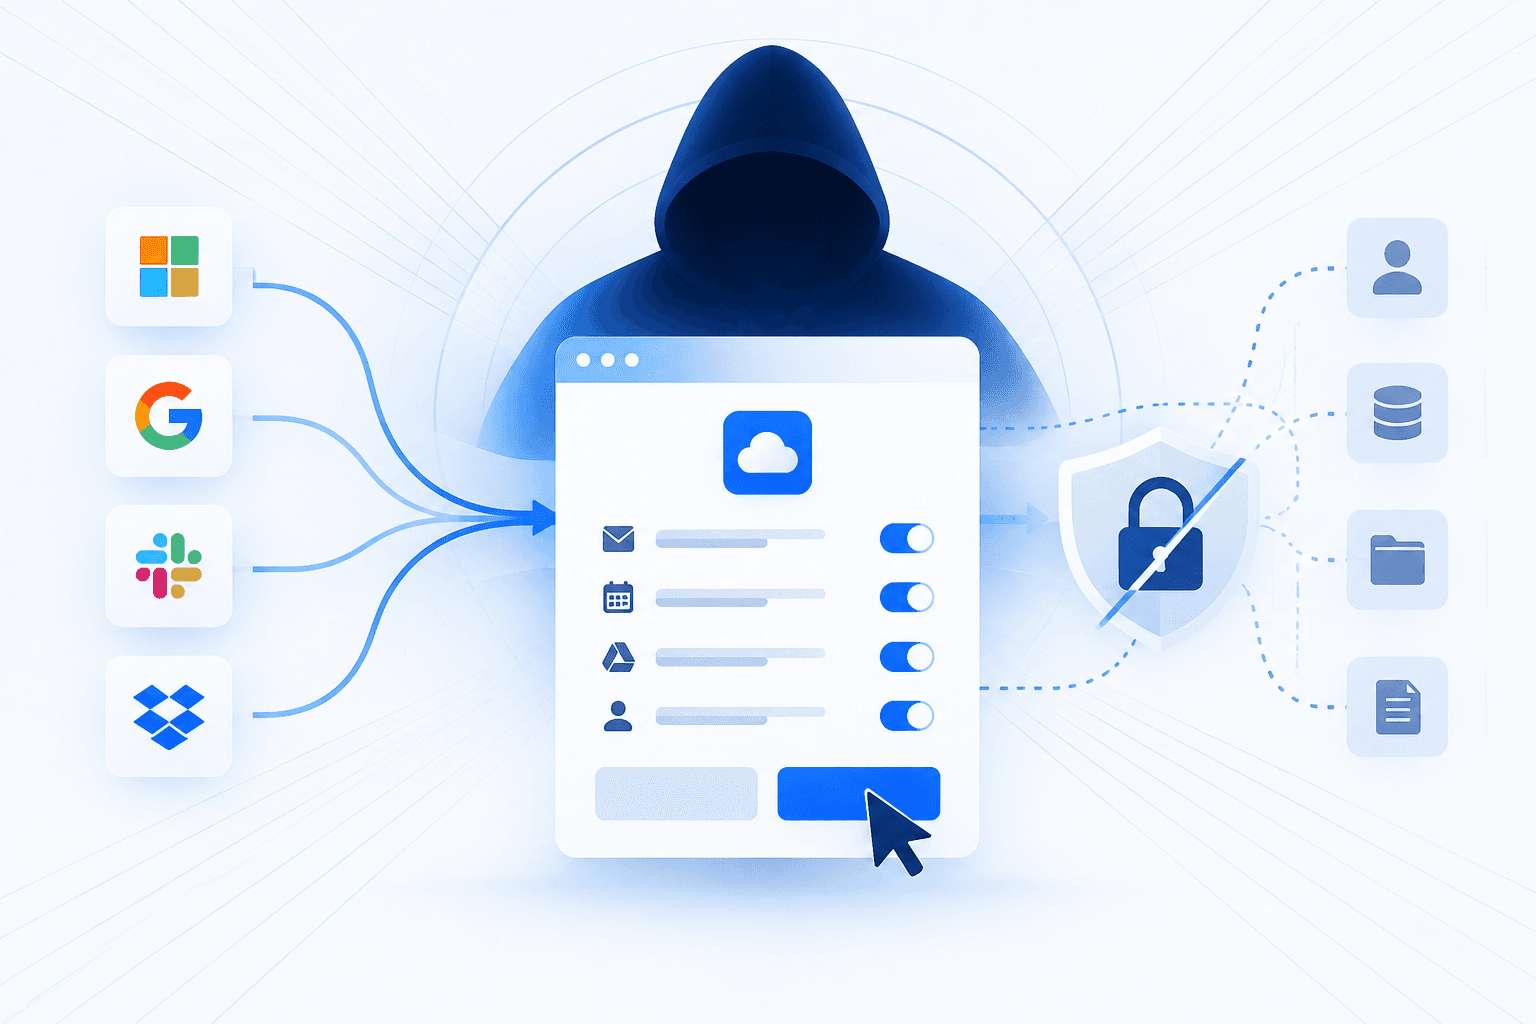
The FBI warned of an ongoing targeted OAuth consent-phishing campaign in which attackers impersonate government officials, media figures, public personalities, event organizers, and other trusted contacts through phishing emails and commercial messaging applications. The activity, observed since late 2025, targets prominent individuals as well as their relatives and acquaintances, luring them into authorizing attacker-controlled applications. Granting consent gives attackers persistent, high-level access to cloud accounts, including email and sensitive data, through legitimate OAuth authorization flows rather than stolen passwords. The access can survive password changes and bypass conventional password and multifactor authentication protections until the victim explicitly revokes the malicious application's permissions in account security settings. The FBI advised users to verify unsolicited contacts, authorize only trusted applications, and closely review requested OAuth permissions.
Sep 11, 2026
Microsoft warned that **consent phishing** campaigns are increasingly abusing the OAuth authorization flow in Microsoft 365 to trick users into granting attacker-controlled applications access to corporate cloud data. In campaigns observed against remote workers, attackers sent phishing emails through compromised domains or cloud providers, then redirected victims to malicious Office 365 OAuth apps disguised as legitimate services. One campaign impersonated Mexico’s tax administration service to target Spanish-speaking users, while another used financial-themed lures aimed at investment teams; Microsoft later described similar tactics using a **"Review Doc(s) & Sign"** lure tied to a fake business services brand. If a user approved the requested permissions, the attackers could obtain **access and refresh tokens** and use them to access email, files, contacts, SharePoint resources, OneDrive for Business data, and mailbox forwarding settings without directly stealing passwords. Microsoft said it had taken down malicious infrastructure and disabled rogue OAuth apps, while urging organizations to tighten Microsoft identity platform consent settings, limit user consent to **verified publishers** and low-risk permissions, audit application grants, and use Microsoft Defender for Office 365 and related tooling to detect and remediate **illicit consent grants**.
Aug 14, 2026
Security researchers have identified a new phishing technique called **ConsentFix** that enables attackers to compromise cloud accounts by exploiting legitimate OAuth consent flows. Instead of stealing passwords or MFA codes, the attack relies on social engineering to trick users into copying and pasting a valid Microsoft sign-in URL, which contains an OAuth authorization code, back into a phishing page. This allows threat actors to capture OAuth authorization codes and access tokens, granting them full access to the victim's cloud account without credential exposure. The attack specifically targets users by requiring a matching email address and leverages trusted authentication infrastructure, making detection more challenging for organizations relying on cloud services. The ConsentFix method is similar to the previously documented ClickFix technique, which used fake CAPTCHA pages, but it innovates by harvesting tokens directly through the OAuth process. The phishing flow involves a Cloudflare-style verification prompt, targeted email validation, and redirection to a legitimate Microsoft login page. After successful authentication, the victim is instructed to paste a localhost URL containing the authorization code into the phishing site, enabling the attacker to hijack the session. This technique poses a significant risk to organizations using cloud platforms, as it bypasses traditional credential theft defenses and exploits the inherent trust in OAuth authentication flows.
Jun 29, 2026