
Loading story…
Attackers compromised F5 BIG-IP Access Policy Manager (APM) webtop servers and deployed the Linux rootkit PoisonedRefresh, which injects a PHP web shell into Apache process memory while leaving the corresponding APM script files unchanged on disk. F5 linked the activity to exploitation of CVE-2025-53521, an unauthenticated remote-code-execution flaw previously classified as a denial-of-service issue; Sophos assessed the rootkit as a likely second-stage payload. The campaign has not been attributed to a named threat actor.
The implant hooks Linux, Apache, and PHP loading functions to run attacker commands, and provides a password-protected local Unix-socket backdoor. Related tooling can modify the HTTP server binary, SELinux configuration, and BIG-IP upgrade images for persistence. Defenders should preserve volatile evidence and investigate anomalous Apache memory mappings and child processes, local sockets, altered SELinux settings and upgrade images, and suspicious HTTP 201 responses disguised as CSS assets.

See which actors are running it and whether you're in range.
6 events from the most recent confirmed update back to the earliest known activity.
SophosLabs published technical details of PoisonedRefresh, including its memory-only injection of an encrypted PHP web shell into BIG-IP APM webtop scripts and its authenticated local UNIX-socket backdoor. The analysis also disclosed persistence and detection indicators, including the /run/bigtlog.pipe socket, modified SELinux settings, altered upgrade images, and anomalous HTTP 201 CSS-like responses.
The Shadowserver Foundation observed 795 internet-exposed F5 BIG-IP APM endpoints vulnerable to CVE-2025-53521.
CISA added CVE-2025-53521 to its Known Exploited Vulnerabilities catalog after F5 confirmed exploitation of the BIG-IP APM vulnerability.
F5 initially disclosed CVE-2025-53521 as a denial-of-service vulnerability affecting BIG-IP APM configurations with an access policy assigned to a virtual server. F5 later reclassified it as an actively exploited unauthenticated remote-code-execution vulnerability.
Sophos analysts identified a Linux rootkit, named PoisonedRefresh by ESET, targeting F5 BIG-IP APM webtop servers. Sophos assessed it as a likely second-stage payload following exploitation of CVE-2025-53521; the activity was not attributed to a named threat actor.
F5 Networks reclassified CVE-2025-53521 from a denial-of-service issue. The vulnerability was subsequently described as a critical unauthenticated remote-code-execution flaw affecting BIG-IP devices.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Correlate live exploitation activity against the software you actually run, and see where you're exposed.
9 references tracked. Mallory keeps watching after this page renders.
cysecurity.news
Open sourcecsoonline.com
Open sourcescworld.com
Open sourcehelpnetsecurity.com
Open sourcemkd-cirt.mk
Open sourcesecurityaffairs.com
Open sourcethehackernews.com
Open sourcebleepingcomputer.com
Open sourcecryptika.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
F5 BIG-IP Access Policy Manager (APM) contains an actively exploited critical buffer-overflow vulnerability, **CVE-2026-94127** (CVSS 9.8), that enables unauthenticated remote code execution. An attacker can send specially crafted traffic to a vulnerable virtual server configured with both an APM access policy and an OAuth profile; the flaw affects the data plane, including Appliance Mode deployments, but not the control plane. Affected releases include BIG-IP APM 21.1.0, 17.5.x, and 17.1.x versions lacking the applicable engineering hotfixes. F5 and national cyber agencies urge administrators to install the vendor hotfixes immediately; an F5 iRule is available as a temporary mitigation. Defenders should investigate repeated OAuth failures, suspicious commands, and TMM `SIGABRT` crashes using F5’s compromise guidance, while treating any single indicator as insufficient evidence of compromise.
Sep 26, 2026
CISA added **`CVE-2025-53521`** to its Known Exploited Vulnerabilities catalog after confirming active exploitation of a flaw in **F5 BIG-IP Access Policy Manager (APM)**. The vulnerability affects BIG-IP **17.x, 16.x, and 15.x** when an APM access policy is configured on a virtual server, and specially crafted unauthenticated traffic can crash and restart the **TMM** process, creating a path to potential **root-level remote code execution**. F5 had initially treated the issue as a denial-of-service bug, but reclassified it as **RCE** after new information emerged, sharply raising the severity of the threat. F5 said fixes were released in February 2025, with patched versions including **17.1.0.4**, **16.1.4.3**, and **15.1.10.2** or later, and warned that end-of-technical-support systems should be considered unprotected. CISA ordered Federal Civilian Executive Branch agencies covered by **BOD 22-01** to remediate by **March 30, 2026**, while urging organizations to assess internet-exposed F5 devices, review F5-published indicators of compromise and attacker tradecraft, and investigate for signs of intrusion. Reporting also noted the KEV listing comes after F5's earlier nation-state compromise, which allegedly exposed source code and undisclosed vulnerability information.
Jun 29, 2026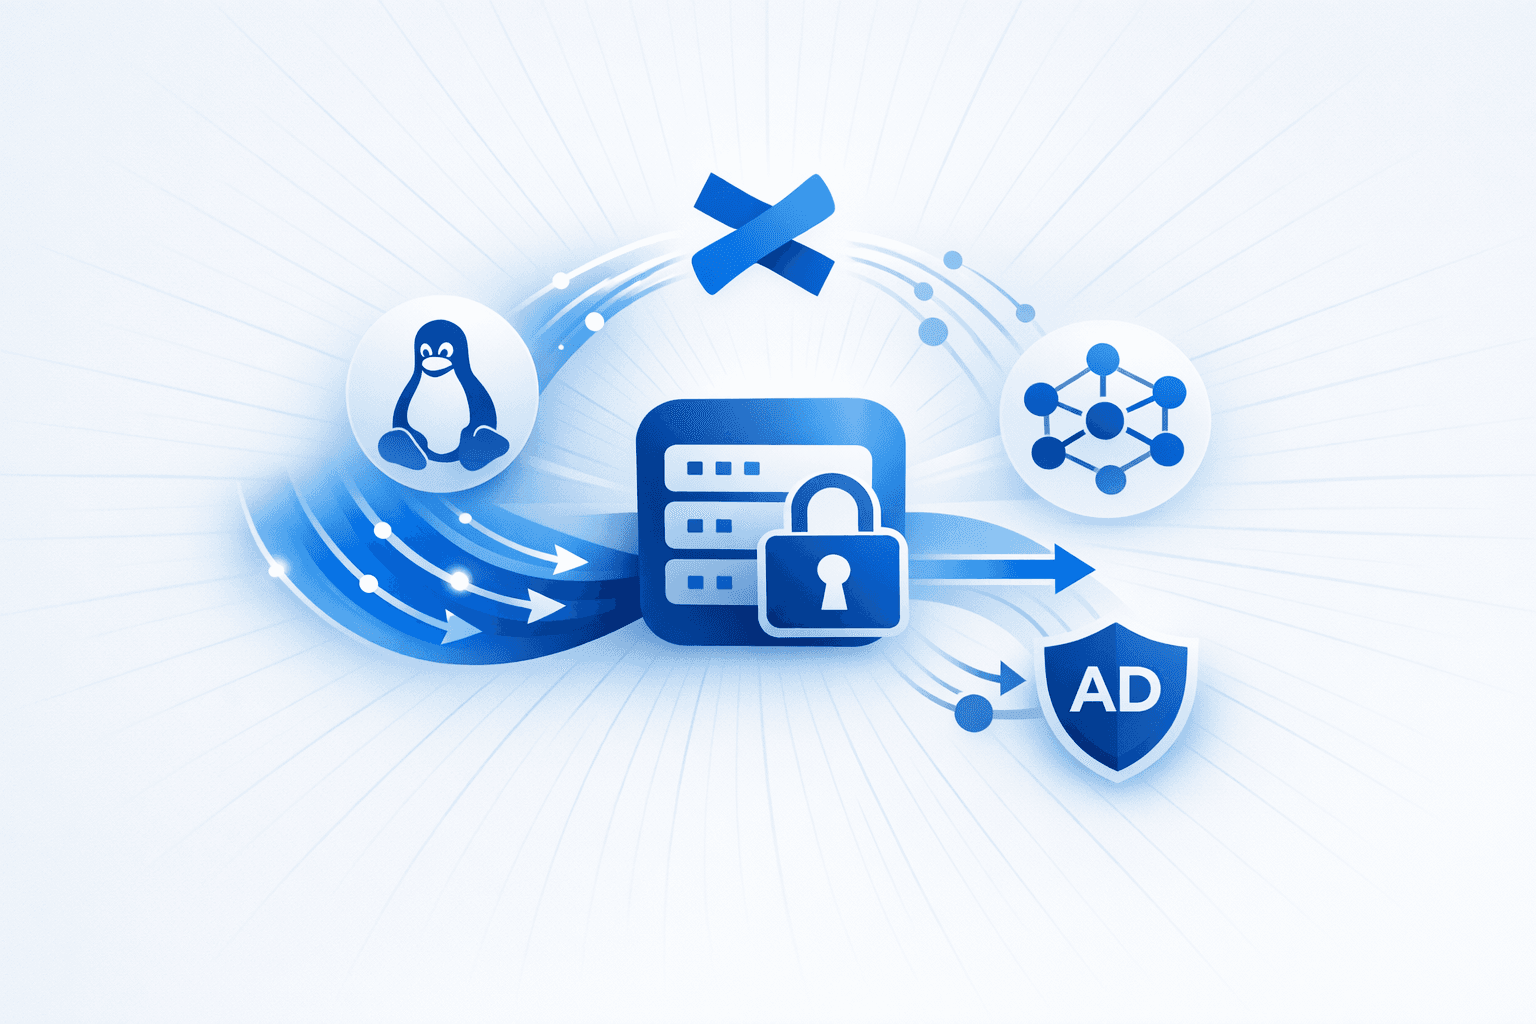
Microsoft reported a multi-stage intrusion that began with the compromise of an internet-facing **F5 BIG-IP** appliance and expanded into broader enterprise access. The attacker used the edge device to obtain SSH access to an internal Linux host, then carried out reconnaissance with tools including **Nmap**, **gowitness**, and other open-source utilities. Microsoft said the actor also downloaded a custom scanner, detected as `HackTool:Linux/MalPack.B`, from `206.189.27[.]39`, and used the Linux foothold to identify an unpatched internal **Atlassian Confluence** server. The attacker exploited Confluence for remote code execution, shifted payload staging to an FTP server on the initial Linux host after other delivery methods were blocked, and extracted credentials from Confluence configuration files. Those credentials were then used in attempts to move into Windows identity infrastructure through relay-style attacks against **Active Directory**, including Kerberos relay activity and exploitation of `CVE-2025-33073`, while the actor also tested SSL/TLS exposure with **testssl**. Microsoft said the case shows how end-of-life edge appliances, unpatched internal applications, and weak identity protections can combine into a single attack chain spanning network appliances, Linux systems, enterprise applications, and domain services.
Jun 29, 2026