
Loading story…
Microsoft detected an AI-assisted business email compromise and invoice-fraud campaign that sent more than one million emails from August 3–5, primarily targeting U.S. enterprise users. The attackers impersonated executives at victim organizations and ServiceNow, targeting accounts-payable personnel with fabricated invoices and forged email threads intended to prompt ACH transfers of nearly $50,000.
The campaign used third-party email-delivery accounts and newly registered lookalike domains to make the payment requests appear legitimate. Microsoft found no evidence that ServiceNow or any other organization impersonated in the lures had been compromised or participated in the activity. Campaign artifacts indicated AI-assisted development of phishing templates, though Microsoft could not conclusively determine the extent to which AI generated the messages; organizations should ensure anti-phishing controls and automated attack-disruption capabilities in Microsoft Defender XDR are configured to contain comparable BEC activity.
Get the infrastructure and lures behind it.
3 events from the most recent confirmed update back to the earliest known activity.
Microsoft identified service-nowinc[.]com, domainlify[.]net, and associated sender addresses as campaign indicators, and found template features consistent with AI-assisted development. Microsoft found no evidence that ServiceNow or other impersonated organizations were compromised or involved.
An invoice-fraud phishing campaign sent more than one million messages, primarily to U.S. enterprise users and accounts-payable staff. The messages impersonated executives and ServiceNow, using fabricated invoices and forged email threads to seek ACH payments of nearly $50,000.
The threat actor registered service-nowinc[.]com and domainlify[.]net, later using them in spoofed ServiceNow contact details and Reply-To addresses.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 21 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
7 references tracked. Mallory keeps watching after this page renders.
decipher.sc
Open sourcetherecord.media
Open sourcecryptika.com
Open sourcecybersecuritynews.com
Open sourcemalware.news
Open sourcemicrosoft.com
Open sourcelearn.microsoft.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Barracuda Networks researchers demonstrated a proof-of-concept attack showing how email-integrated AI assistants such as **Microsoft Copilot** could amplify business email compromise after a single mailbox is breached. In the simulated intrusion, attackers used the assistant to create stealthy inbox rules, map internal relationships, summarize sensitive threads, and mimic a user’s writing style, allowing them to conduct reconnaissance and launch convincing internal phishing from a legitimate account. The attack chain escalated from an employee mailbox to the CEO’s account by capturing the executive’s session token through an adversary-in-the-middle proxy, bypassing MFA and giving the attackers control of the real mailbox. From there, the CEO’s AI assistant was used to identify a legitimate pending wire transfer—reported in one scenario as **$247,500**—and generate fraudulent payment instructions redirecting funds to an attacker-controlled bank account, while forwarding or deleting messages to conceal the fraud; researchers warned that the risk extends beyond Copilot to any AI assistant with inbox access.
Aug 4, 2026
Attackers used an HR-themed adversary-in-the-middle (**AiTM**) phishing lure to steal an authenticated Microsoft 365 session from a finance employee and hijack a shared accounts-payable mailbox, enabling a cloud-only business email compromise without malware. Investigators found the victim’s real Microsoft 365 login and MFA approval were relayed through the phishing page, after which the attackers replayed the captured session cookie from commercial VPN infrastructure; Microsoft 365 telemetry showed MFA as previously satisfied, and Entra ID logs recorded impossible-travel activity between Amsterdam and Los Angeles within about a minute. With access to Exchange Online, SharePoint, Microsoft 365 Search, and finance mailboxes, the attackers monitored legitimate invoice workflows and carried out a roughly 30-day payment-diversion scheme using both vendor impersonation and internal look-alike-domain impersonation. They also created malicious inbox rules, deleted or hid collection notices and other messages that could reveal the fraud, while investigators correlated browser history, email headers, mailbox audit logs, and sign-in telemetry to confirm session-token replay and cloud account compromise.
Aug 21, 2026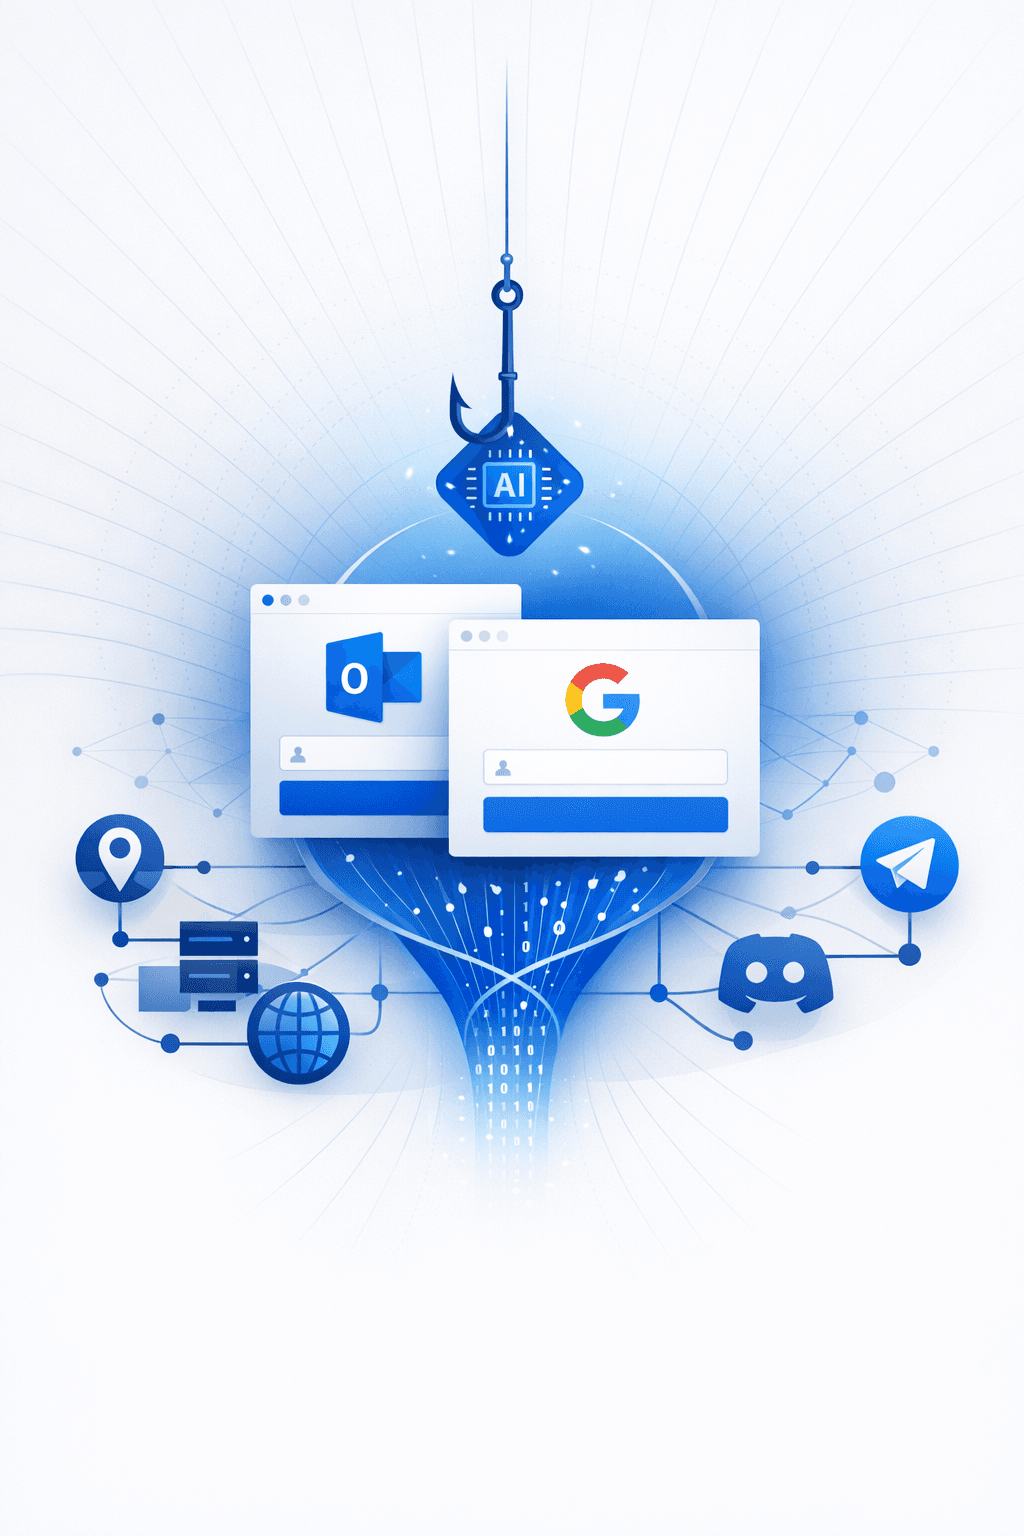
A sophisticated phishing campaign has emerged, leveraging AI-assisted development to target Microsoft Outlook users, particularly Spanish speakers. The operation, active since March 2025, employs a modular phishing kit that mimics the Outlook login interface and uses real-time reconnaissance to enrich stolen credentials with IP and geolocation data. Stolen information is exfiltrated via Telegram bots and Discord webhooks, and the kit's evolution shows clear signs of AI-generated code, including clean structure and Spanish-language comments. Researchers identified the campaign through a unique mushroom emoji signature embedded in the phishing kit, which has been observed in over 75 deployments. In a parallel development, another phishing wave has exploited Google Cloud Application Integration to send convincing emails from legitimate Google addresses, bypassing traditional security filters. This campaign, uncovered by Check Point researchers, uses a multi-stage process: victims receive official-looking emails, are redirected through Google infrastructure, and ultimately land on a fake Microsoft login page designed to harvest credentials. The attack has targeted over 3,000 organizations globally, with significant activity in the United States, Asia-Pacific, and Europe. Both campaigns demonstrate the increasing sophistication and global reach of phishing operations using advanced technical methods and trusted platforms to deceive users.
Jun 29, 2026