Mallory
← Back to News
breach-disclosure-notificationfinancial-sector-threatmass-credential-exposureidentity-impersonation-fraud

Fraudulent Government Request Triggers Revolut KYC and Transaction Data Exposure

Breach & Incident Intelligence · 33 sources · Updated 2mo ago · First seen Sep 12, 2026
Fraudulent Government Request Triggers Revolut KYC and Transaction Data Exposure

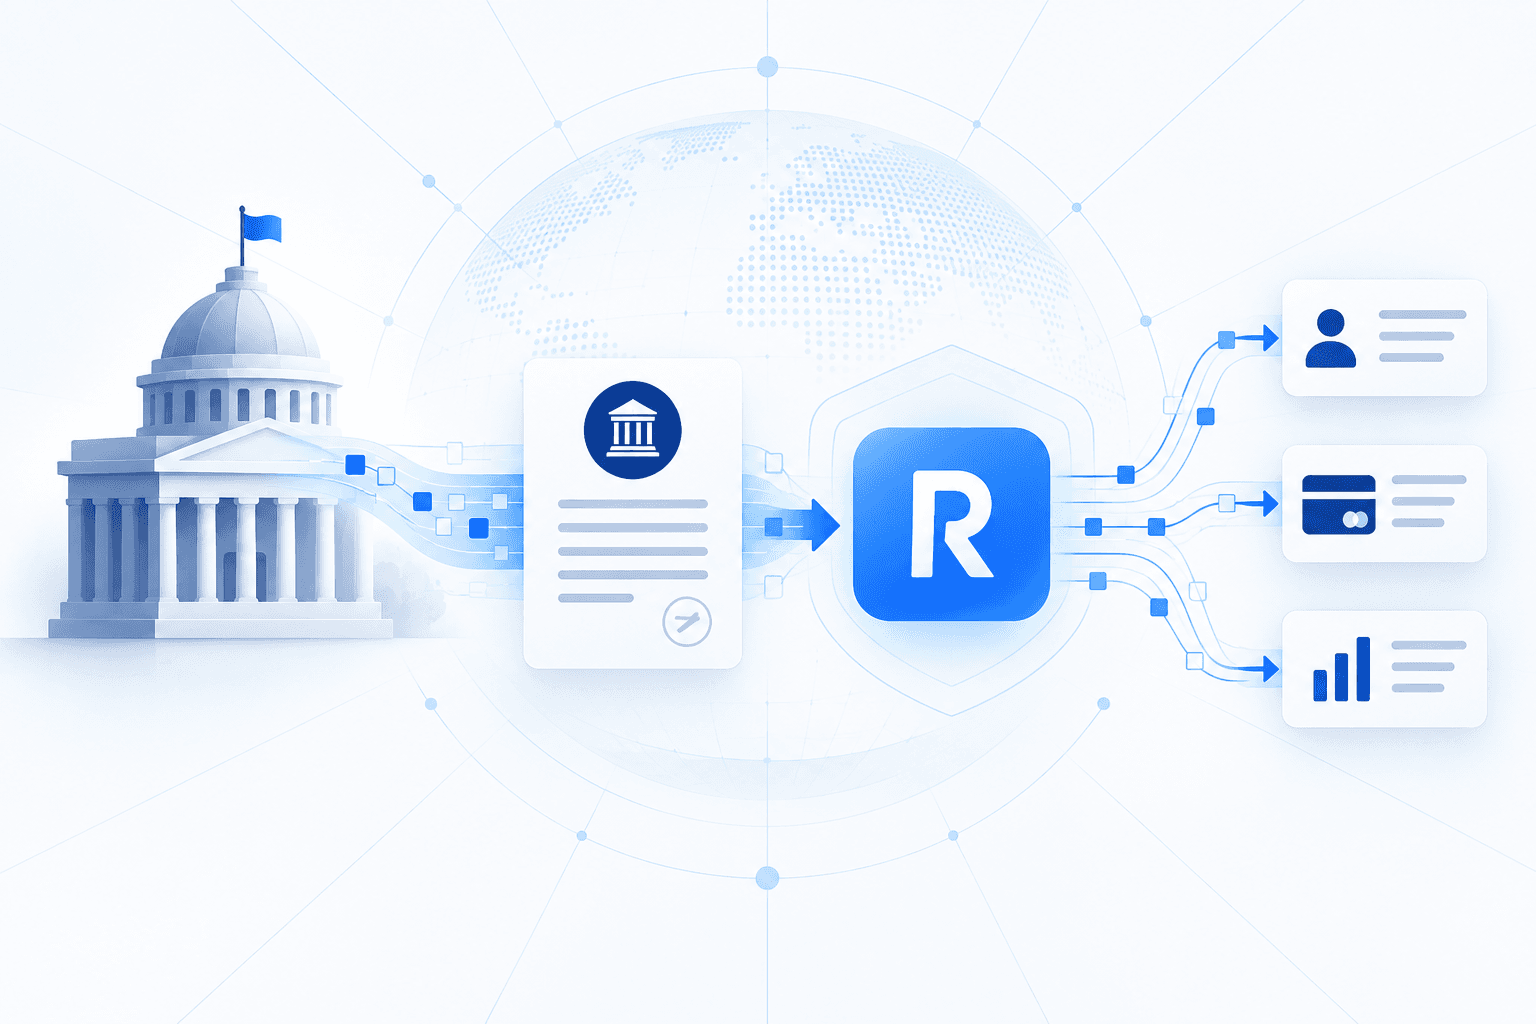
Revolut disclosed that it released sensitive customer information to an unauthorized party after receiving a fraudulent data request impersonating a legitimate government agency. The request reportedly originated from an unauthorized account using an official agency email domain with valid domain-authentication credentials, causing it to be treated as legitimate. The number of affected customers, the impersonated authority, and the precise failure path have not been publicly confirmed.

The exposed records reportedly include passport or other KYC identity documents, facial-verification selfies, contact details, account statements, IBANs, withdrawal records, and full transaction histories, including Bitcoin-related activity. Revolut said its core systems, mobile app, customer accounts, and funds were not compromised; it blocked the email source, notified authorities, and contacted affected users. The combined identity and financial data creates elevated risks of identity fraud, targeted phishing and vishing, SIM-swapping, fraudulent account opening or direct debits, extortion, and persistent linkage between customer identities and blockchain addresses.
Is this vendor in your chain?See attribution, scope, and your downstream exposure.
Check the blast radius
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

19 events · Sep 2022 – Sep 14, 2026
  1. Reported Sep 17, 20262mo ago

    Italian prosecutor and privacy regulator open Revolut disclosure investigations

    The Reggio Calabria Prosecutor's Office and Italy's data-protection regulator opened investigations into the fraudulent PEC-based requests that caused Revolut to disclose customer data. Investigators had not determined how the Prefecture of Reggio Calabria PEC mailbox was compromised.

    Мошенники получили данные клиентов Revolut через почту властей Италии и теперь требуют выкуп - Хакер
  2. Reported Sep 17, 20262mo ago

    Attackers claim theft of 147GB from Italian law-enforcement agency

    The alleged Revolut attackers also claimed to have stolen more than 147GB of data from an Italian law-enforcement agency. Italian police launched an investigation into the related claims.

    Revolut Data Breach: 5 Months, 680 High-Profile Accounts, $3M Ransom - SecurityWeek
  3. Reported Sep 17, 20262mo ago

    “iamnotavillain” demands 6,000 Monero over alleged Revolut data

    A group calling itself “iamnotavillain” claimed it had obtained Revolut customer data and demanded 6,000 Monero, reportedly worth about $3 million, threatening to sell the data to other criminals if unpaid within 24 hours. Revolut said it had received no direct ransom demand and had not negotiated with the alleged attackers.

    Hackers Demand $3M Ransom in Revolut Data Leak | OCCRP
  4. Reported Sep 15, 20262mo ago

    Italy’s Postal Police investigate compromised Prefecture PEC account

    Italy’s Interior Ministry confirmed that the Postal Police are investigating the compromise of the Prefecture of Reggio Calabria’s PEC account, which was allegedly used to send fraudulent data requests to Revolut. The method used to compromise the account remained unknown.

    Revolut piégé par de faux enquêteurs : données de 680 clients livrées via une PEC usurpée | CyberVeille
  5. Reported Sep 15, 20262mo ago

    Alleged Revolut attackers demand 10,000 Bitcoin and post data samples

    Individuals claiming responsibility for obtaining Revolut customer data allegedly posted samples of the purportedly stolen information in multiple Telegram groups and demanded 10,000 Bitcoin from Revolut.

    Hackers demand 10,000 Bitcoin from Revolut following data breach - Malware News - Malware Analysis, News and Indicators
  6. Reported Sep 15, 20262mo ago

    Alleged Revolut leak names Shevchenko and Römer as affected customers

    Social-media reports identified allegedly leaked Revolut customer records as belonging to tennis player Shevchenko and Gamdom/Skinscom CEO Römer. The reports emerged amid claims that perpetrators were leaking data obtained through the fraudulent government-agency request.

    teiss - News - Revolut falls victim to spoofed agency email, suffers data breach
  7. Reported Sep 14, 20262mo ago

    Crypto figures Zeller and Karpelès report being affected by Revolut disclosure

    Marc Zeller and Mark Karpelès stated that their customer data was exposed in Revolut’s fraudulent government-agency request incident. The suspected perpetrators appeared to have selected a limited number of high-net-worth customers, many involved in cryptocurrency businesses.

    Revolut handed customer data to fraudsters using government email account | The Record from Recorded Future News
  8. Sep 14, 20262mo ago

    Affected Revolut customer reports liveness-check phishing SMS

    An affected customer reported receiving a Revolut-impersonation phishing text message that appeared in the same SMS thread as legitimate Revolut messages. The linked site reportedly requested camera access, mimicked a liveness check, and then prompted for a password; no direct connection to the customer-data disclosure was established.

    Revolut phishing texts appear days after data breach - Malware News - Malware Analysis, News and Indicators
  9. Reported Sep 13, 20262mo ago

    Attackers allegedly extort Revolut over fraudulently obtained customer data

    Attackers were reportedly said to have demanded payment from Revolut in exchange for not releasing customer data obtained through fraudulent emergency data requests. Revolut declined to comment on whether it had received or faced the alleged extortion demand.

    Revolut divulgue des données clients à des fraudeurs via de fausses demandes gouvernementales | CyberVeille
  10. Reported Sep 12, 20262mo ago

    Lithuanian data-protection authority investigates 2022 Revolut breach

    Lithuania’s State Data Protection Inspectorate investigated Revolut’s 2022 breach as the lead data-protection supervisory authority for Revolut’s EEA entities.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  11. Sep 2026

    Fraudulent Revolut requests reportedly expose data of about 680 customers

    Approximately 680 Revolut customers were reportedly affected after fraudulent data requests were sent from a compromised PEC mailbox associated with the Prefecture of Reggio Calabria on Italy’s pec.interno.it domain. The mailbox was allegedly used to impersonate Italian Postal Police officers; Revolut said its own systems were not breached.

    Revolut Data Leak May Trace Back to Compromised Italian Government Accounts
  12. Sep 2026

    Revolut blocks fraudulent email source and alerts authorities

    Following the disclosure, Revolut said it blocked the unauthorized email source, notified relevant authorities, and contacted affected customers. Customer posts and screenshots describing the apparent fake-government-request vector circulated publicly on September 11–12.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  13. Sep 2026

    Revolut says exposed data included IDs, selfies and transaction histories

    The disclosed information reportedly included names, dates of birth, contact details, passport or driving-licence copies, identity-verification selfies, account statements, IBANs, withdrawal records, wallet references, and complete transaction histories including Bitcoin activity. Revolut stated that biometric facial telemetry was not involved or compromised.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  14. Sep 2026

    Revolut discloses customer data released to government-agency impersonator

    Revolut notified affected customers that sensitive identity, KYC, contact, and financial data had been disclosed after it received a fraudulent request impersonating a government agency. The request reportedly originated from an unauthorized account using an official agency email domain with valid domain-authentication credentials; Revolut said its systems, customer accounts, and funds were not compromised.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  15. Aug 2026

    Jersey reports scam losses involving Revolut accounts

    During a four-week period spanning August to September, approximately 75% of scam reports in Jersey involved Revolut accounts, with roughly £180,000 reportedly lost.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  16. Jul 2026

    Forum actor advertises alleged Revolut customer records

    A cybercrime-forum actor advertised 75 million alleged Revolut records for $500. Revolut reportedly found no indicators of compromise or valid identifiers in the offered samples.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  17. Apr 2026

    Attackers allegedly use compromised Italian government email for Revolut requests

    Hudson Rock reported that the alleged attackers used credentials from infostealer logs to access Italian Ministry of the Interior email accounts and send fraudulent European Investigation Order-related data requests to Revolut Bank UAB. The operation allegedly began about five months before the report and involved attacker-controlled recovery emails, inbox monitoring, and deletion of outgoing messages and replies.

    Revolut Hackers Used Infostealers for Elaborate Social Engineering | Hudson Rock
  18. Feb 2026

    Former Revolut employee allegedly attempts KYC-data extortion

    A former Revolut employee was alleged to have threatened to leak a customer’s KYC data unless paid in cryptocurrency. Revolut reportedly referred the matter to law enforcement.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
  19. Sep 2022

    Revolut suffers social-engineering data breach

    Revolut suffered a targeted social-engineering breach involving a phished employee credential. Data of 50,150 customers, including names, addresses, contact details, partial card data, and past transactions, was exposed.

    Revolut Data Breach 2026: Passports, Selfies & Bitcoin History Exposed | The CyberSec Guru
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Organizations

2 linked
RevolutRevolut Bank UAB

Breaches

1 linked
REVOLUT-2026-09

Observables

1 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See attribution, scope, and whether this vendor sits anywhere in your supply chain.
Get the Full Incident Picture
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.