LLMjacking Turns Stolen Cloud Credentials Into Resold AI Compute
Emerging Technology Risk · 4 sources · Updated 2mo ago · First seen Sep 13, 2026
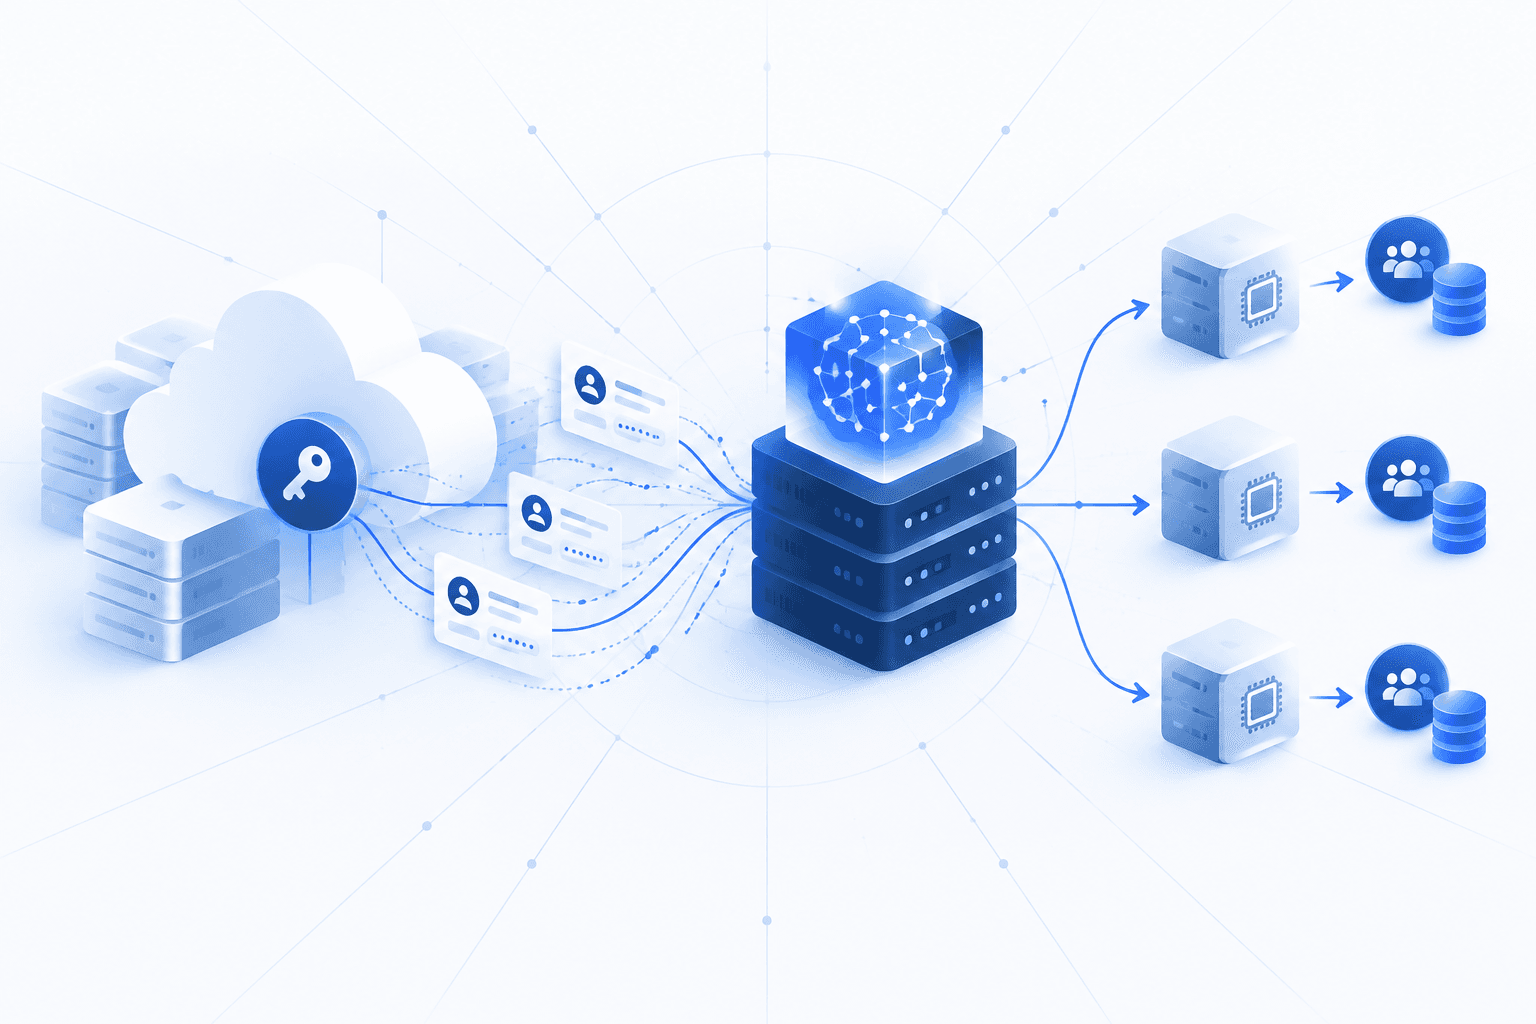
Attackers are increasingly monetizing stolen cloud credentials through LLMjacking: unauthorized use of hosted large-language-model services that charges inference costs to victims. In observed AWS incidents, attackers used long-lived IAM keys with AdministratorAccess to create IAM users, accept Amazon Bedrock Marketplace agreements, and invoke foundation models; earlier activity used credentials exposed through a vulnerable Laravel instance affected by CVE-2021-3129 to test access across multiple AI platforms and target Anthropic Claude through Bedrock. Adversaries have used malformed InvokeModel requests to validate access and checked whether invocation logging was enabled, while sustained abuse of Claude quotas across regions was estimated to cost more than $46,000 per day and exhaust legitimate customer capacity.
The activity has developed into a commercial access market. Researchers report that “Operation Bizarre Bazaar” scans for exposed, unauthenticated APIs and Model Context Protocol (MCP) servers using internet-search services, validates compromised access, and resells LLM compute or API access through Telegram and Discord marketplaces for cryptocurrency and PayPal. MCP compromise may also enable access to connected internal file systems or databases, extending the risk beyond fraudulent AI consumption. Organizations should eliminate long-lived privileged keys, use short-lived role credentials and least-privilege permissions, remediate exposed services and secret leaks, and investigate new Bedrock activity—especially identity creation, unfamiliar source IPs, service enumeration, access-denied events, and missing or disabled CloudTrail and model-invocation logs.