ShinyHunters Breached Charter Salesforce Through Employee Vishing
Social Engineering & Fraud · 3 sources · Updated 2mo ago · First seen May 28, 2025
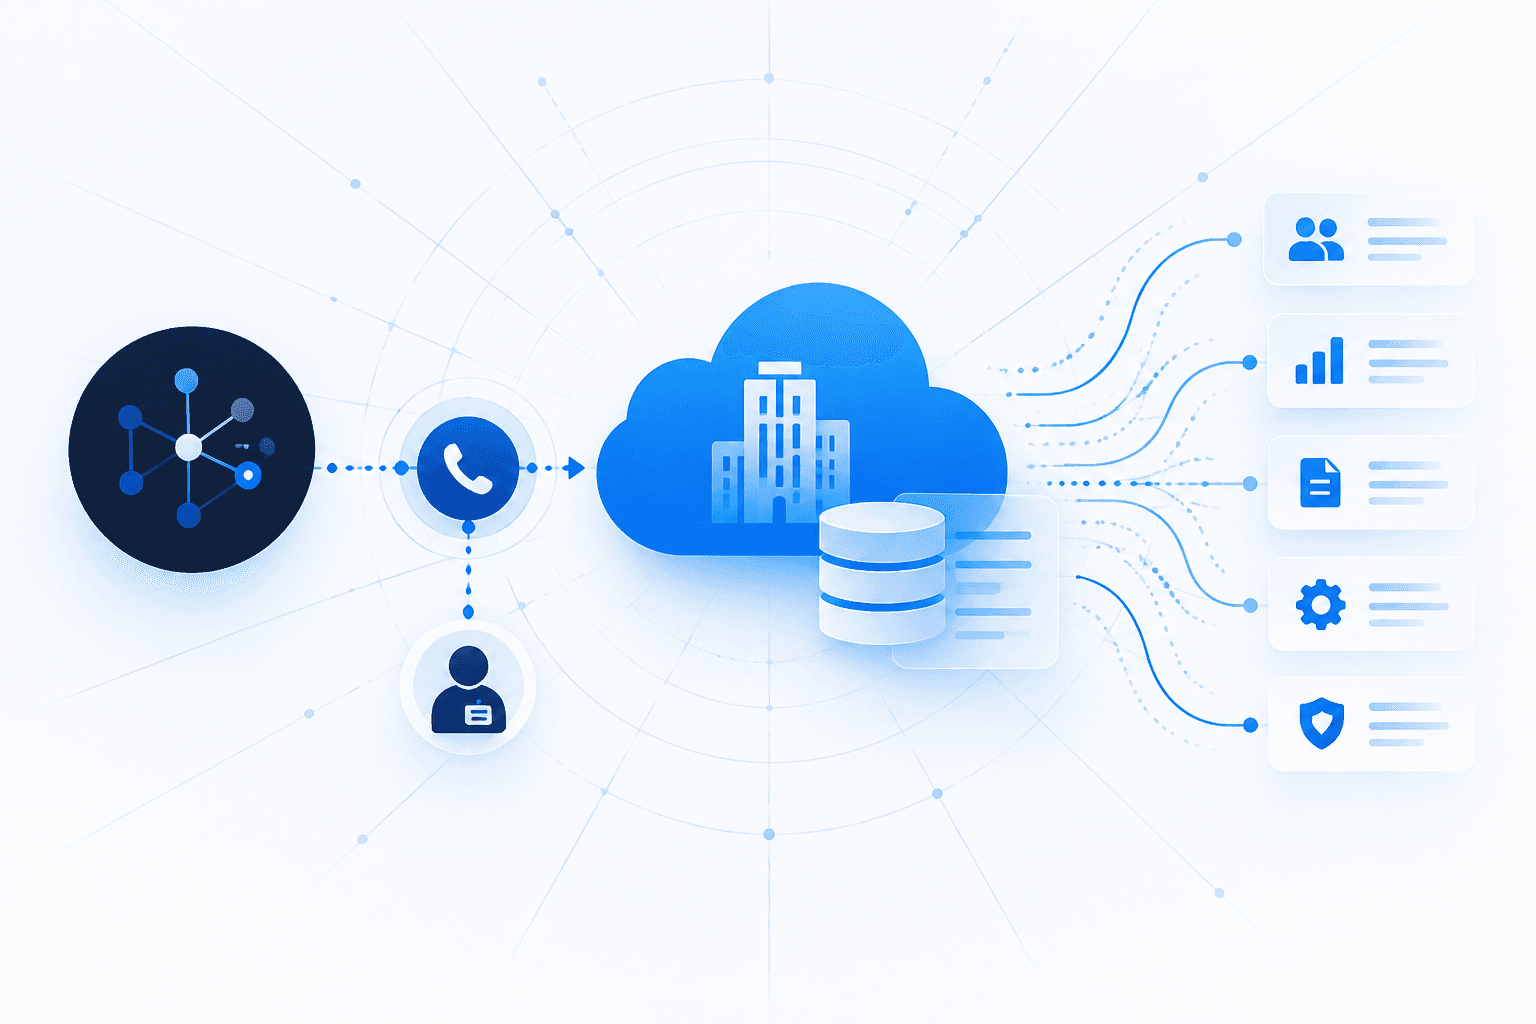
ShinyHunters allegedly gained access to Spectrum/Charter Communications' Salesforce environment by vishing an employee and compromising the employee's Microsoft Entra account. The actors reportedly used legitimate SSO access and native Salesforce capabilities to export customer data at scale, without exploiting a software vulnerability, deploying malware, or escalating privileges. Charter disclosed the incident on May 26, 2025, and said sensitive personal information and customer proprietary network information (CPNI) were not taken; ShinyHunters disputed that assertion and began releasing purported data samples the following day.
The intrusion reflects the social-engineering and identity-centric tradecraft associated with the Scattered LAPSUS$ Hunters ecosystem, an alliance linked to Scattered Spider, LAPSUS$, and ShinyHunters activity. Organizations using Entra and Salesforce should prioritize resistant help-desk identity-verification processes, Conditional Access, monitoring of Entra sign-ins and Salesforce activity, behavioral detection, and controls that restrict anomalous or bulk data exports.