Critical WooCommerce Wholesale Lead Capture Flaw Exploited to Hijack WordPress Sites
Active Exploitation · 8 sources · Updated 2mo ago · First seen Mar 29, 2026
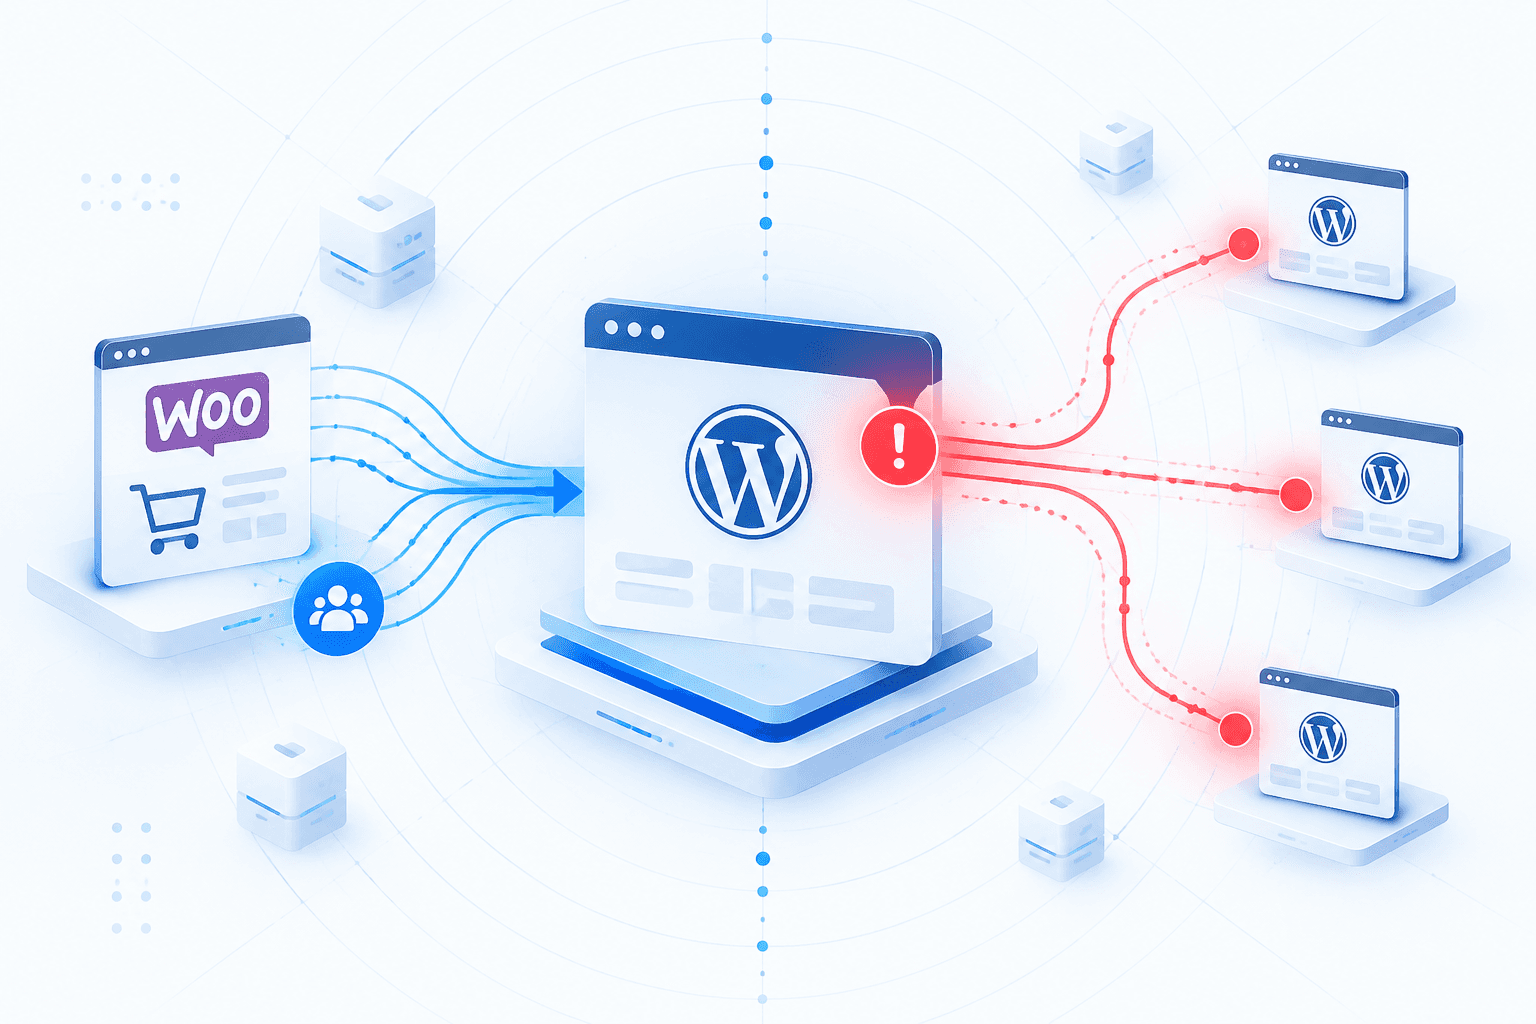
Attackers are actively exploiting CVE-2026-27540, a critical CVSS 9.8 unauthenticated arbitrary-file-upload flaw in the WordPress/WooCommerce Wholesale Lead Capture plugin. Versions through 2.0.3.1 trust attacker-controlled file-type settings in the public wholesale-registration form, allowing attackers to upload executable PHP files without logging in and gain remote code execution on the hosting server.
Exploitation has reportedly persisted for months, and Wordfence has blocked more than 100,000 attempts against roughly 6,000 active installations. Affected operators should upgrade to version 2.0.3.2 and investigate for PHP webshells, unauthorized administrator accounts, altered checkout content, persistence mechanisms, suspicious outbound connections, and related log activity.