
Loading story…
Fraudulent websites impersonating cryptocurrency gift-card provider Bitrefill are appearing in search results and directing shoppers through cloned checkout flows. The sites use typo-squatted, brand-plus-word, and internationalized/Punycode domains, closely reproduce Bitrefill branding, and offer cryptocurrency and apparent card-payment options before substituting attacker-controlled wallet addresses and QR codes for payments, reportedly as high as $1,990.
Victims receive no gift cards or other products after sending funds, and cryptocurrency transfers generally cannot be reversed or charged back. The operators also appear to use commercial analytics to measure and improve conversion; Bitrefill says it is working with takedown specialists. Organizations should warn users to navigate directly to bitrefill.com, validate the registrable domain before payment, and never approve unverified wallet transactions or token permissions.
Get the infrastructure and lures behind it.
2 events from the most recent confirmed update back to the earliest known activity.
Bitrefill publicly stated that similarly named sites copying its checkout had appeared in search results and that its security team was working with takedown specialists to remove impersonating domains.
A cluster of fraudulent websites impersonating Bitrefill was identified targeting users who search for Bitrefill or gift cards. The sites copy Bitrefill's checkout flow and direct cryptocurrency payments to attacker-controlled wallet addresses, leaving victims without purchased goods or services.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 27 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
malware.news
Open sourcemalwarebytes.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Fraudulent cryptocurrency “AML checker” websites are impersonating legitimate wallet screening services and luring users into connecting wallets, approving token access, signing transactions, or sending funds. The scam relies on professional-looking pages, fake progress indicators, fabricated errors, and reassuring results such as **“Clean, Low Risk”** to make the checks appear credible, while some sites mimic known brands including AMLBot or use generic names such as **“AML Check.”** The operation abuses a key difference between real and fake screening: a legitimate AML wallet check only needs a public wallet address and should never require a wallet connection, transaction approval, recovery phrase, or private key. Victims who interacted with these sites are being urged to disconnect the malicious dApps, revoke token approvals, move assets to a new wallet if compromise is suspected, and ignore follow-on “recovery” scams that promise to retrieve stolen funds.
Aug 19, 2026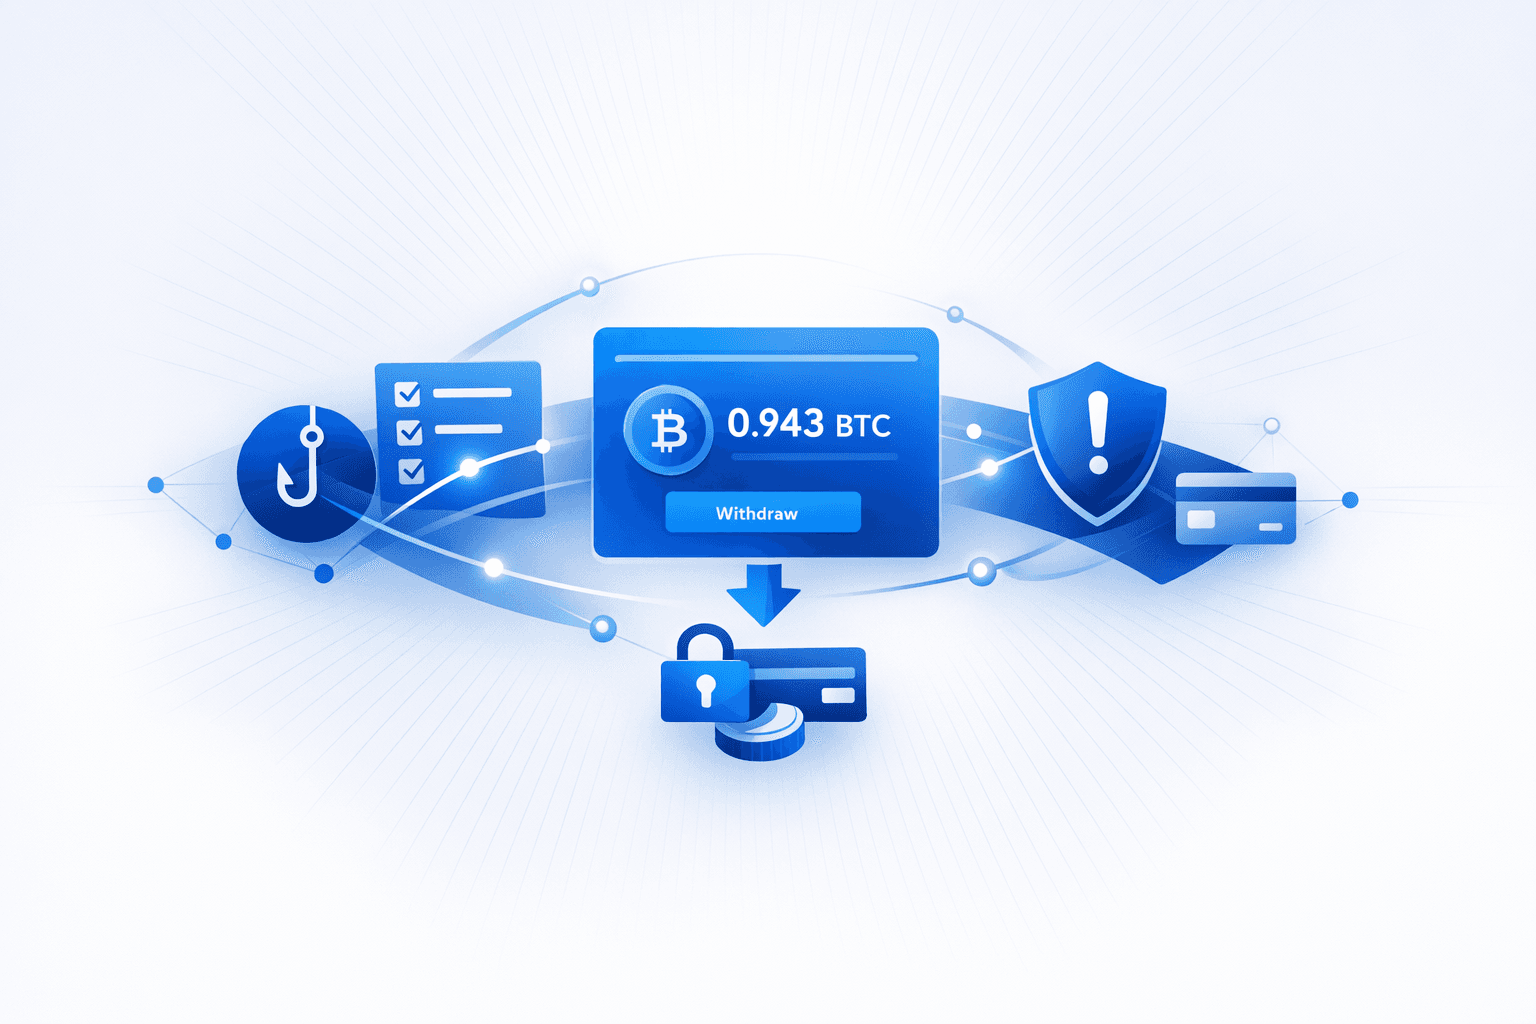
Multiple reports describe **social-engineering scams** that impersonate trusted brands and payment providers to drive victims into credential theft or direct monetary loss. A “crypto compensation” lure abuses a legitimate-looking *Yandex* poll as an entry point, then redirects victims to a fake Bitcoin payout page claiming an approved `0.943 BTC` transaction and imposes a small “commission”/fee to withdraw funds—classic advance-fee fraud wrapped in a polished, multi-step funnel (including a fake chat “support agent”). Separately, Japanese-language phishing emails impersonating **ANA**, **DHL**, and **myTOKYOGAS** show consistent infrastructure patterns (notably `.cn` domains in sender and landing-page URLs), suggesting a single operator or shared kit targeting Japanese-speaking recipients. Several consumer scam advisories highlight **SMS-based fraud alerts** that push targets to call attacker-controlled phone numbers, where scammers pose as “support” to steal **Apple ID/2FA codes** or payment details, or to coerce victims into moving money. One PayPal-themed case escalated to cash withdrawals handed to a courier after a victim called a number from an unsolicited text, illustrating how “fraud department” pretexts can transition from phishing to **cash-out theft**. Additional warnings cover lookalike payment sites (e.g., `payyourbill.aps medical.com`) and generic guidance on what to do after clicking a phishing link; these are broadly consistent with the same theme (phishing/payment fraud) but are not tied to a single, specific campaign or actor across all items.
Jul 2, 2026
Security researchers reported multiple campaigns abusing *Google* branding to drive crypto theft. Malwarebytes identified a polished fraudulent “presale” site promoting a fake token called **“Google Coin”** and embedding a chatbot that impersonates **Google Gemini**; the bot delivers a scripted investment pitch, cites specific token pricing and a “2026 roadmap,” and steers victims toward sending irreversible cryptocurrency payments while avoiding verifiable corporate, regulatory, or registration details. Separately, Kaspersky’s Securelist detailed **BeatBanker**, an Android malware campaign targeting Brazil that spreads via phishing to a website masquerading as the **Google Play Store** (e.g., `cupomgratisfood[.]shop`) and distributing trojanized APKs such as a fake “INSS Reembolso” app. The malware combines a **cryptominer** with a **banking Trojan** capable of device hijacking and screen overlays, including swapping destination addresses during **USDT** transactions in apps like *Binance* and *Trust Wallet*; newer samples reportedly replaced the banking module with **BTMOB RAT** while retaining the broader infection chain and persistence techniques (including looping near-inaudible audio to resist termination).
Jun 29, 2026