Phishing Campaigns Abuse Amazon SES and URL Cloaking to Evade Email Defenses
Social Engineering & Fraud · 2 sources · Updated 2mo ago · First seen Sep 15, 2026
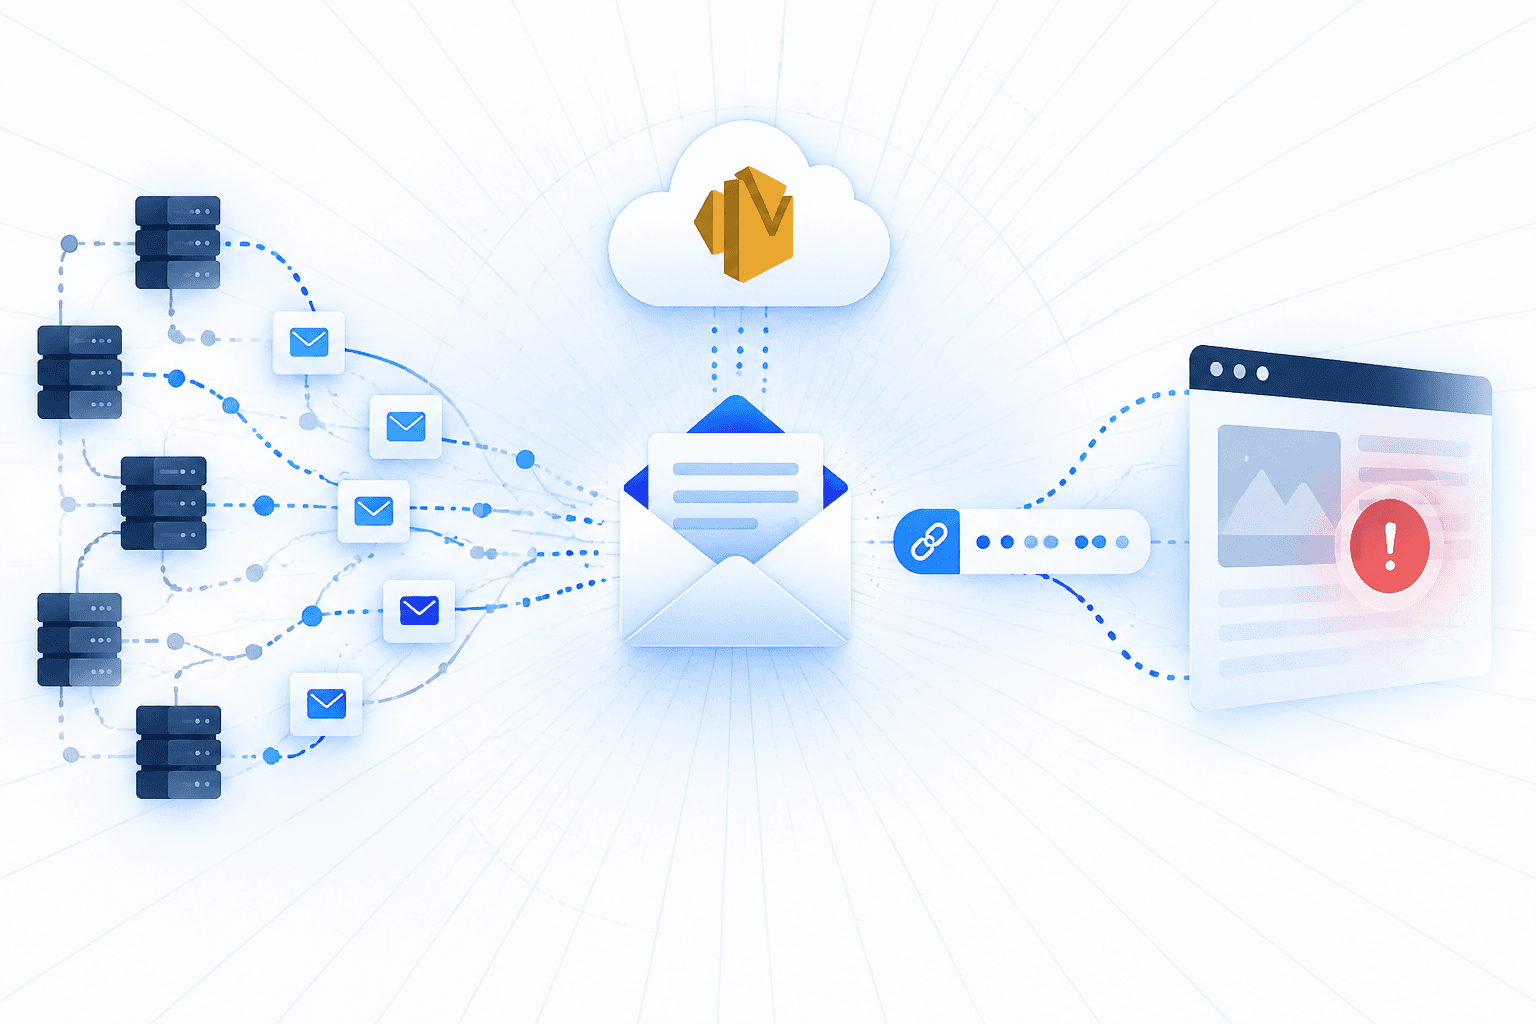
Q3 2026 phishing campaigns abused trusted email infrastructure, including Amazon Simple Email Service (SES), and DKIM-aligned sender domains to make fraudulent messages pass common authentication checks. The emails used overdue-payment, invoice, antivirus-renewal, and banking/PSD2-consent lures, while hiding malicious or fraudulent content behind multi-stage redirect chains rather than attachments or obviously suspicious initial URLs.
One German invoice-themed campaign used browser fingerprinting, hidden requests, decoy content, iframes, and obfuscated code before redirecting analysis traffic to OpenSea, indicating cloaked crypto or NFT fraud. A separate Romanian operation impersonated BCR S.A., using an IPv6-mapped IP-literal URL and redirects to target banking credentials; defenders should assess the full click path and post-load behavior because SPF, DKIM, and DMARC validate sender authorization, not the legitimacy of the request or final destination.