Actively Exploited Issabel PBX Flaw Enables Unauthenticated Command Execution
Active Exploitation · 4 sources · Updated 2mo ago · First seen Sep 16, 2026
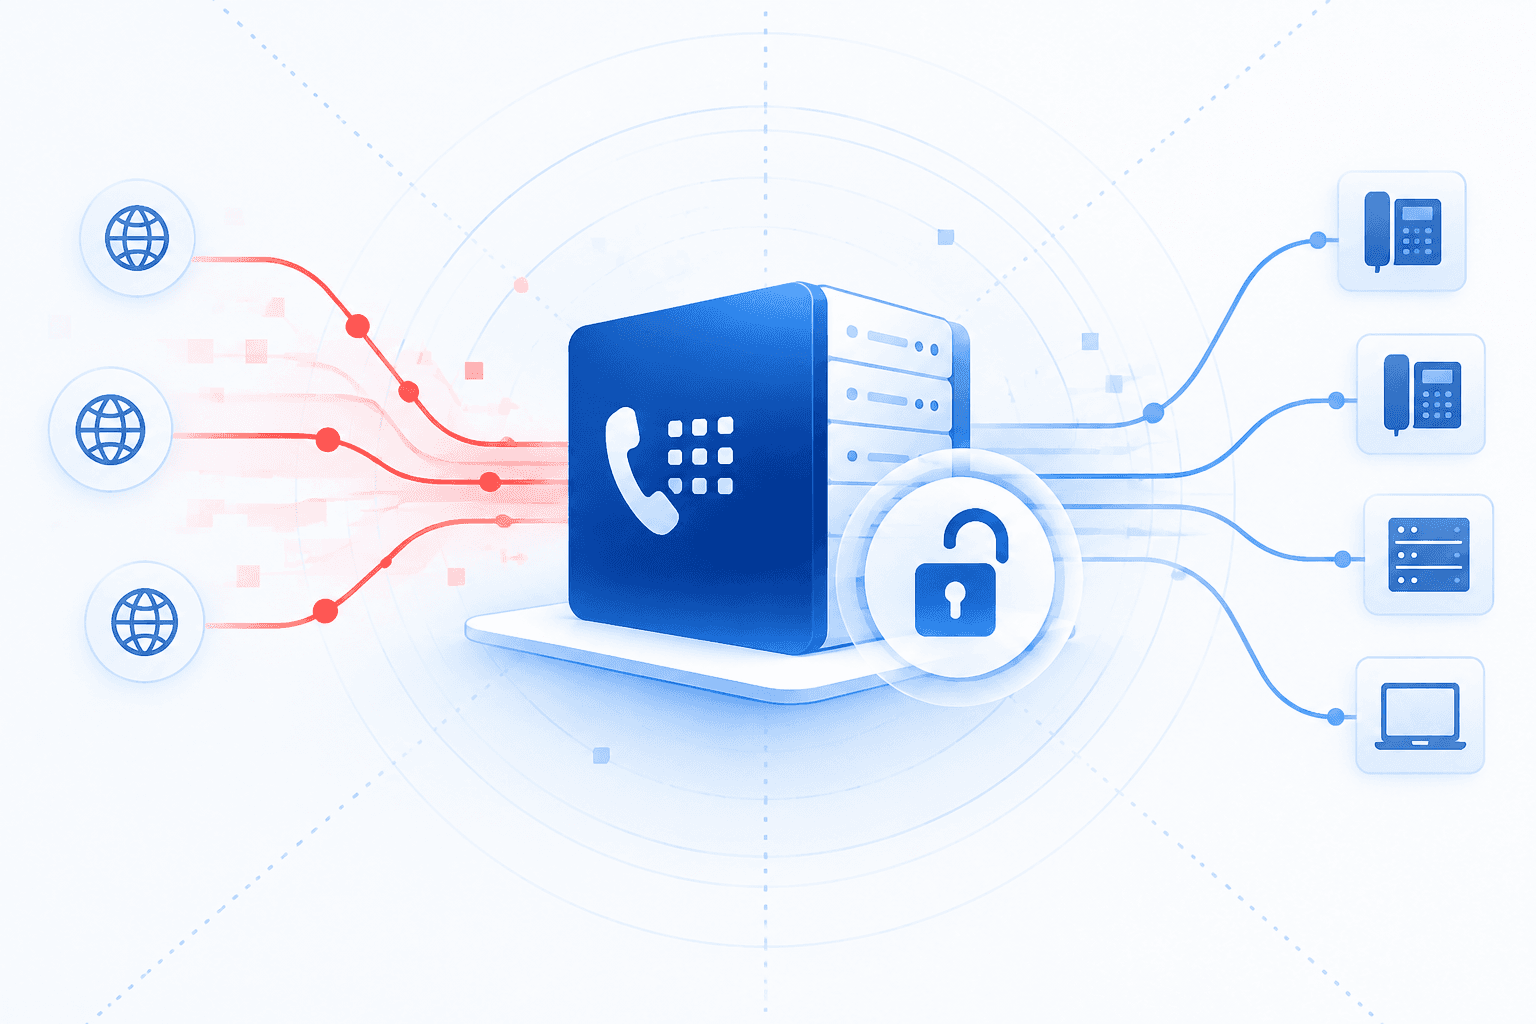
Attackers are actively exploiting CVE-2026-89026, a critical Issabel Framework vulnerability affecting Issabel PBX deployments. A universal hard-coded HS256 JWT signing key in pbxapi/index.php allows unauthenticated remote attackers to forge trusted bearer tokens, call the /pbxapi/manager/originate API endpoint, and abuse Asterisk's System application to execute arbitrary operating-system commands as the Asterisk service account. Shadowserver observed exploitation beginning September 9; VulnCheck assigned the flaw a CVSS v4 score of 9.3 and listed it as known exploited.
Issabel patched the issue by replacing the universal key with one stored in /etc/issabel.conf; organizations should urgently apply the fix associated with commit b97dbaf0b71c1c36f841e672b664afbeb02773bd. Defenders should remove public exposure of PBX APIs and Asterisk management interfaces, restrict access to those services, and investigate affected hosts for anomalous authentication events, originate requests, process or command execution under the Asterisk account, and suspicious outbound network activity.