AI-Generated Code Overwhelms Open-Source Review and Security Controls
Emerging Technology Risk · 2 sources · Updated 2mo ago · First seen Sep 17, 2026
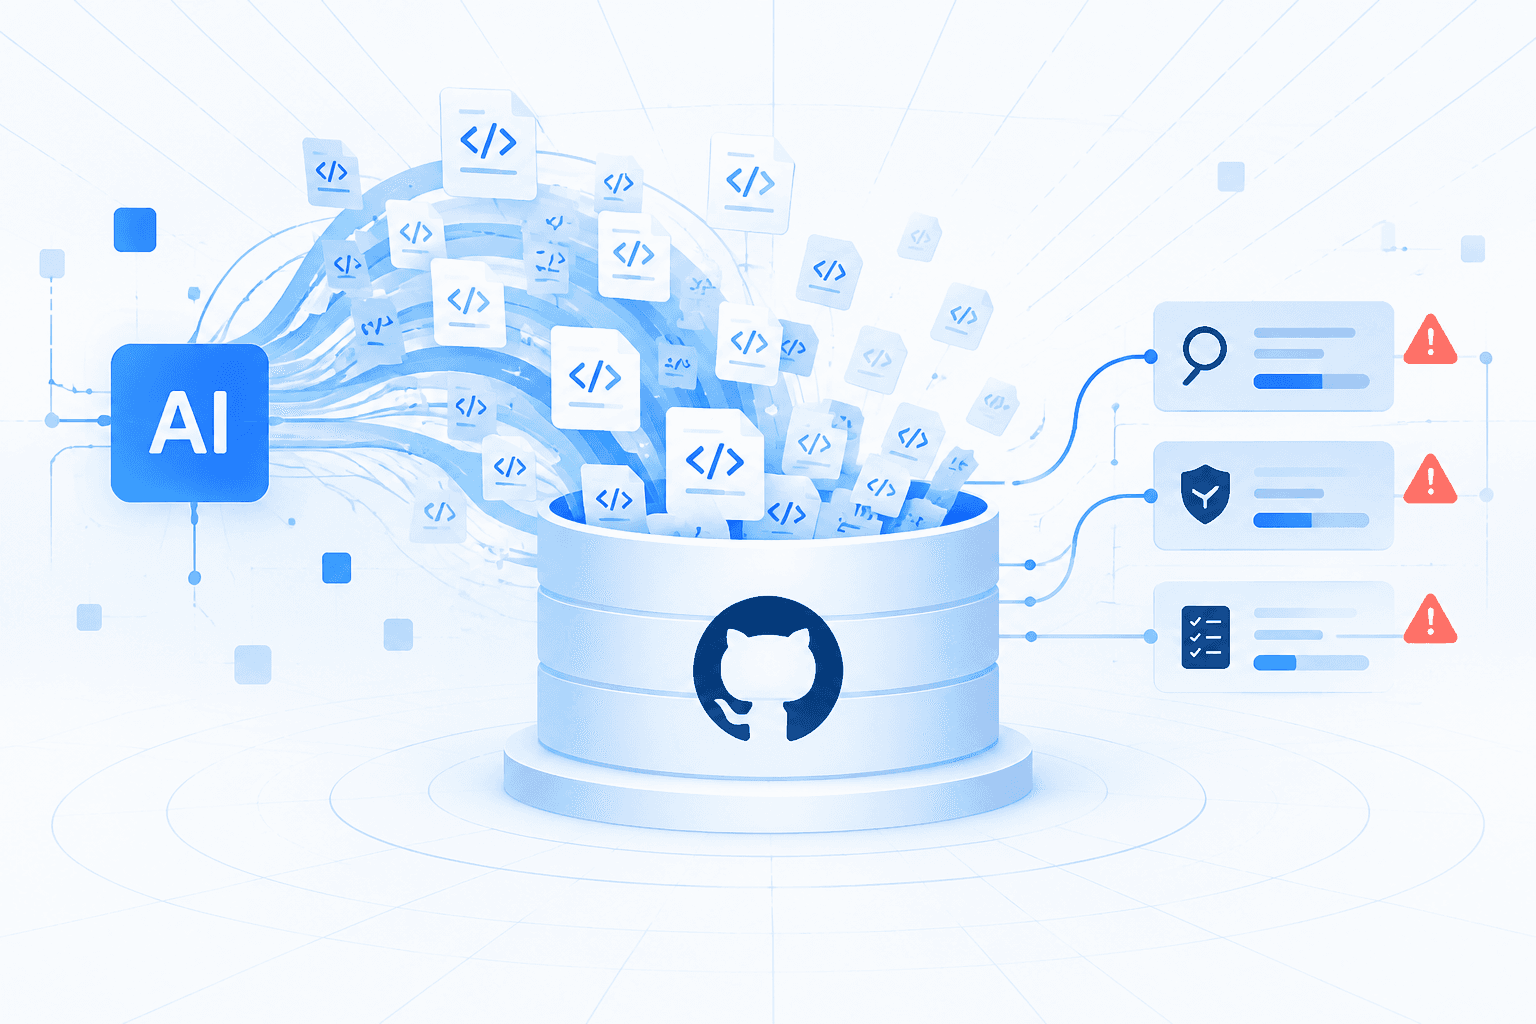
AI coding tools are accelerating software contribution and vulnerability remediation, but they are also expanding the volume of code that maintainers and enterprise engineering teams must validate. Open-source projects—many operating with limited funding and staff—face added exposure from AI-assisted flaw discovery and exploitation, malicious packages, incomplete software bill of materials adoption, and poor visibility into the dependencies organizations rely on.
Security leaders are being urged to treat AI-generated code as disposable implementation governed by explicit requirements, specifications, and tests rather than trusting it as inherently reviewable. AI-assisted review can help identify defects, including a generated regular expression vulnerable to catastrophic backtracking and application denial of service, but it does not remove the need for governance. Recommended controls include investing in project maintenance, documentation, secure packaging, dependency inventories, fundraising, and requirements-focused review while using automated tools to remediate issues and remove obsolete code.