Malicious Chrome and Edge Extensions Stole Data From 2.3 Million Users
Supply Chain Risk · 2 sources · Updated 2mo ago · First seen Sep 17, 2026
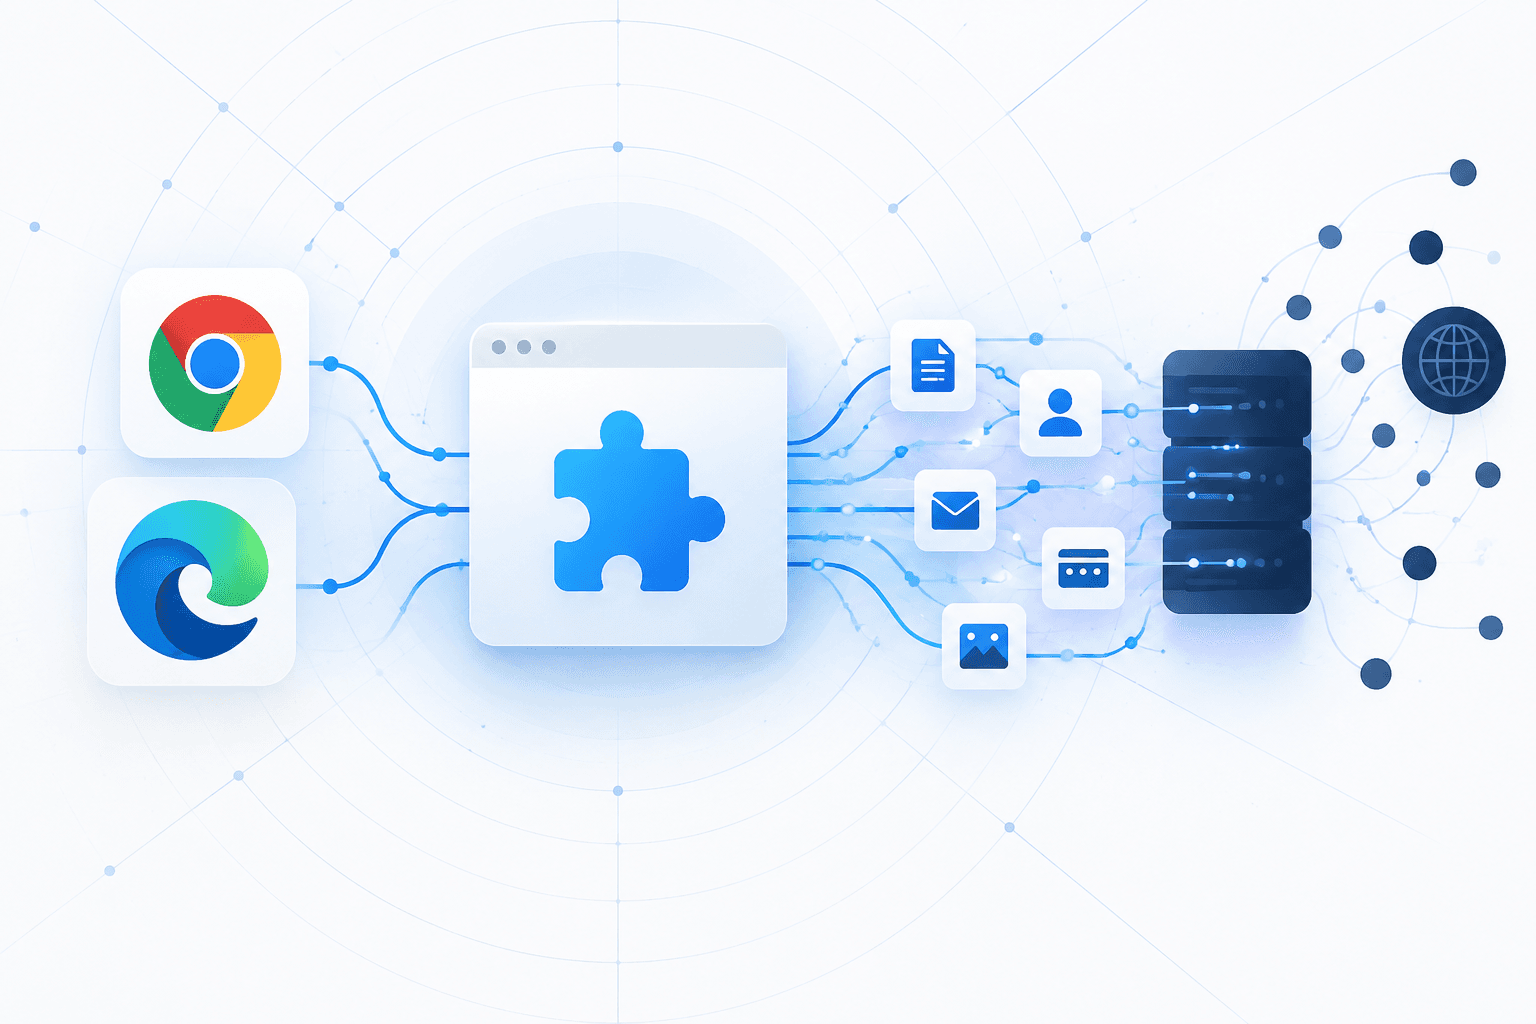
Researchers identified a campaign involving 19 malicious browser extensions distributed through the Google Chrome Web Store and Microsoft Edge Add-ons marketplace, with reported installations exceeding 2.3 million users. Fourteen extensions were published as apparently legitimate software, while five were acquired from their original developers and later updated with malicious functionality, leaving users unaware that ownership and code had changed.
The extensions contacted command-and-control infrastructure to retrieve replaceable modules, bypassed Content Security Policy controls, and injected code into targeted web pages. They could steal credentials, payment data, Facebook and LinkedIn information, browsing history, cryptocurrency assets, and hardware-wallet seed phrases; some also overlaid pages with ClickFix lures that impersonated browser-update notices and persuaded victims to run malicious commands, potentially extending compromise beyond the browser.