
Loading story…
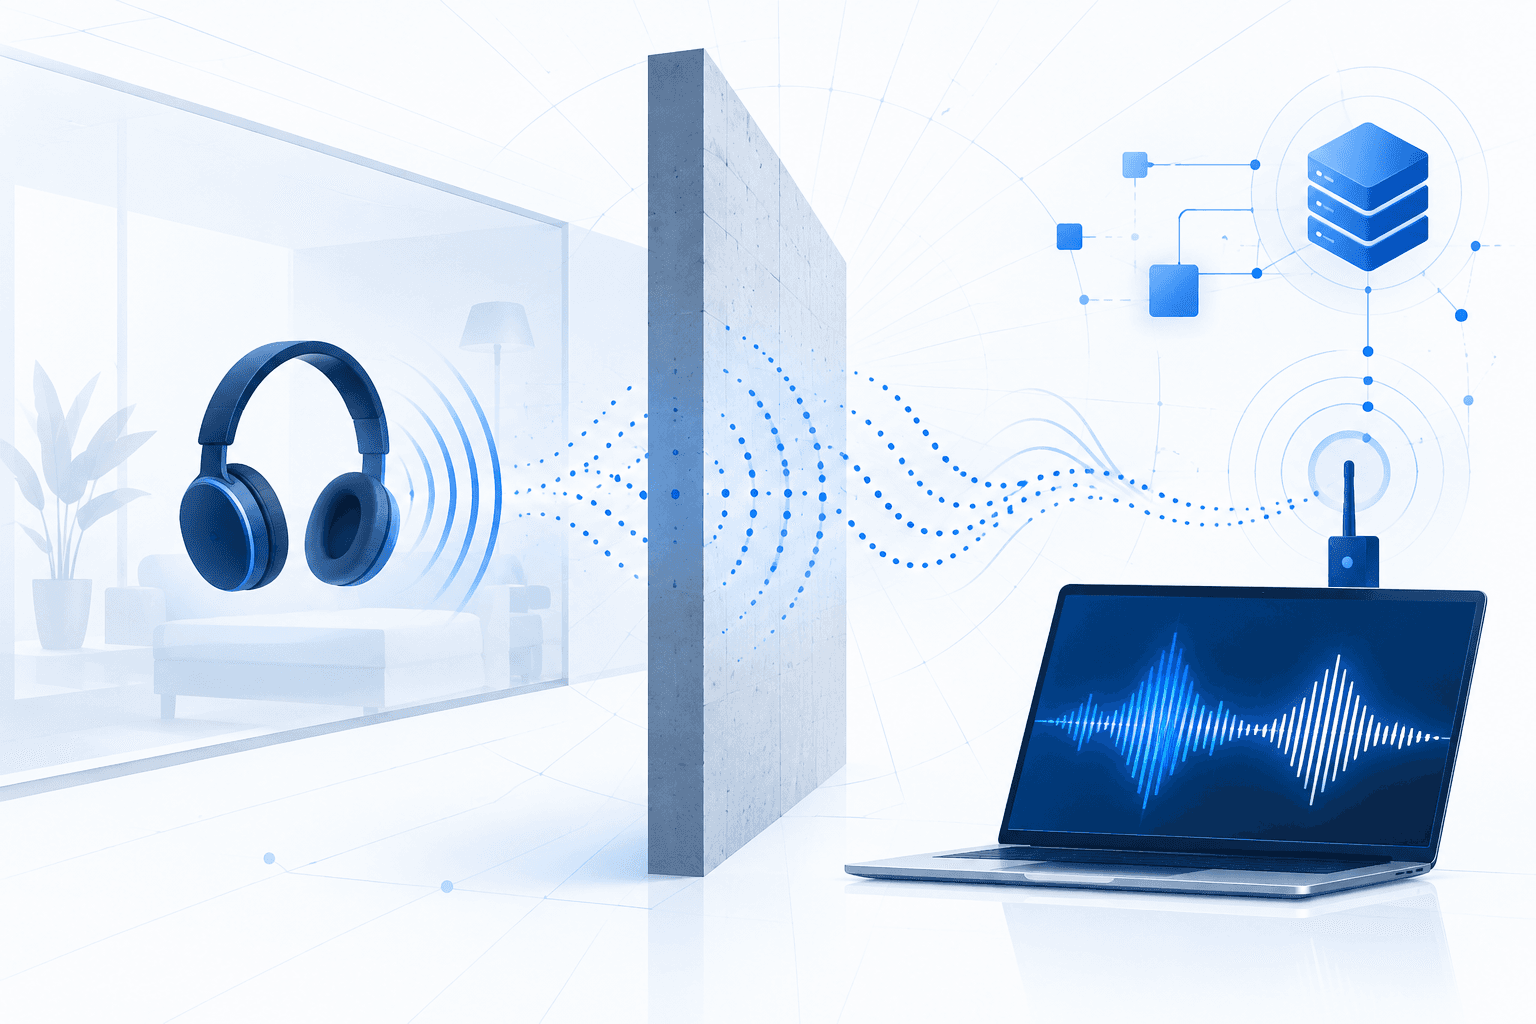
Researchers at Hong Kong University of Science and Technology and Hong Kong Polytechnic University demonstrated InjectEave, an active electromagnetic side-channel attack that injects RF signals into susceptible analog hardware and captures the resulting leakage. The technique exploits non-linear components to transform otherwise weak target signals into detectable emissions, enabling attackers to recover audio and infer device activity despite encryption and other digital protections.
Tests against 11 commercial headphone models, a VoIP handset, smart fans, and smart lamps found that most targets were reachable from more than two meters away, including through walls. Using RF amplification, the researchers recovered intelligible headphone audio at distances of up to 30 meters. Organizations using affected analog audio or smart-device hardware should assess physical exposure and favor hardware mitigations such as electromagnetic shielding, filtering, and twisted-pair wiring.
See affected versions and whether adversaries are exploiting it.
2 events from the most recent confirmed update back to the earliest known activity.
Researchers from the Hong Kong University of Science and Technology and Hong Kong Polytechnic University presented InjectEave at USENIX Security 2026. The technique injects RF signals into nonlinear analog hardware to induce detectable leakage that can recover audio or reveal device activity.
The researchers tested InjectEave against 11 commercial headphones, a VoIP handset, smart fans, and smart lamps, reporting attacks on a majority of tested devices from more than two meters away and through walls. They also demonstrated intelligible headphone-audio recovery at up to 30 meters using an RF amplifier.
See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Researchers at the Hong Kong University of Science and Technology (Guangzhou) and Hong Kong Polytechnic University disclosed **InjectEave**, an active electromagnetic side-channel technique that recovers audio played through wired and wireless headphones from up to 30 meters away, including through concrete walls. Instead of relying on weak passive emissions, an attacker transmits a tuned RF carrier that nonlinear components—such as amplifiers, ADCs, and power converters—mix with low-frequency audio signals, causing the audio to be re-emitted on a measurable carrier; the demonstrations used commercially available SDR equipment. The researchers also observed injection-induced leakage from smart-home power consumption and analog sensor inputs. In a closed-loop scenario involving a Flyingvoice VoIP landline, they combined eavesdropping with AI voice cloning and synthesized-audio injection, demonstrating both confidentiality and integrity risks. The findings identify analog circuitry and connected-device wiring as an attack surface that can bypass protections aimed at digital communications and may not be fully addressed by conventional cryptography or ordinary EM shielding.
Sep 8, 2026
Researchers disclosed three vulnerabilities in Bluetooth audio devices built on Airoha systems-on-chip that can allow an attacker within radio range to gain unauthorized access to device memory and communications. The flaws, tracked as **`CVE-2025-20700`**, **`CVE-2025-20701`**, and **`CVE-2025-20702`**, stem from missing authentication in GATT and Bluetooth BR/EDR components and weak permission controls in a proprietary protocol, affecting headphones and earbuds sold by brands including **Sony, Bose, Jabra, JBL, Marshall, Beyerdynamic, and Teufel**. ERNW researchers said the bugs can be chained to hijack the Bluetooth link between a phone and an audio device, issue commands to the paired phone through the **Hands-Free Profile**, eavesdrop on conversations, and potentially overwrite firmware for remote code execution on the accessory. The attack requires proximity because exploitation is limited by Bluetooth range, but defenders were urged to apply vendor firmware updates and investigate or restart devices showing abnormal Bluetooth behavior.
Jul 24, 2026
Apple has released **Beats Firmware Update `1B211`** to fix a high-severity Bluetooth vulnerability in **Beats Studio Buds** that could let an attacker within wireless range listen through the earbuds’ microphone under limited conditions. The flaw, tracked as **`CVE-2025-20701`**, affected devices while they were **unpaired and actively seeking a pairing request**, allowing pre-pairing eavesdropping. Apple said the issue originated in **open source code** and noted that Apple software was among the affected projects. The bug was identified in **Airoha** system-on-chip code by researchers **Dennis Heinze** and **Frieder Steinmetz** of **ERNW GmbH**, who linked it to missing authentication in the Bluetooth **BR/EDR** radio. ERNW said the flaw could be chained with **`CVE-2025-20700`** and **`CVE-2025-20702`** to enable broader attacks against vulnerable headphones, including issuing phone commands, extracting link keys, accessing call history and contacts, and placing calls, though such attacks require close proximity and substantial technical skill. The update is delivered automatically when the earbuds are paired with an **iPhone, iPad, or Mac**, placed on a charger, and kept within Bluetooth range.
Jun 29, 2026