
Loading story…
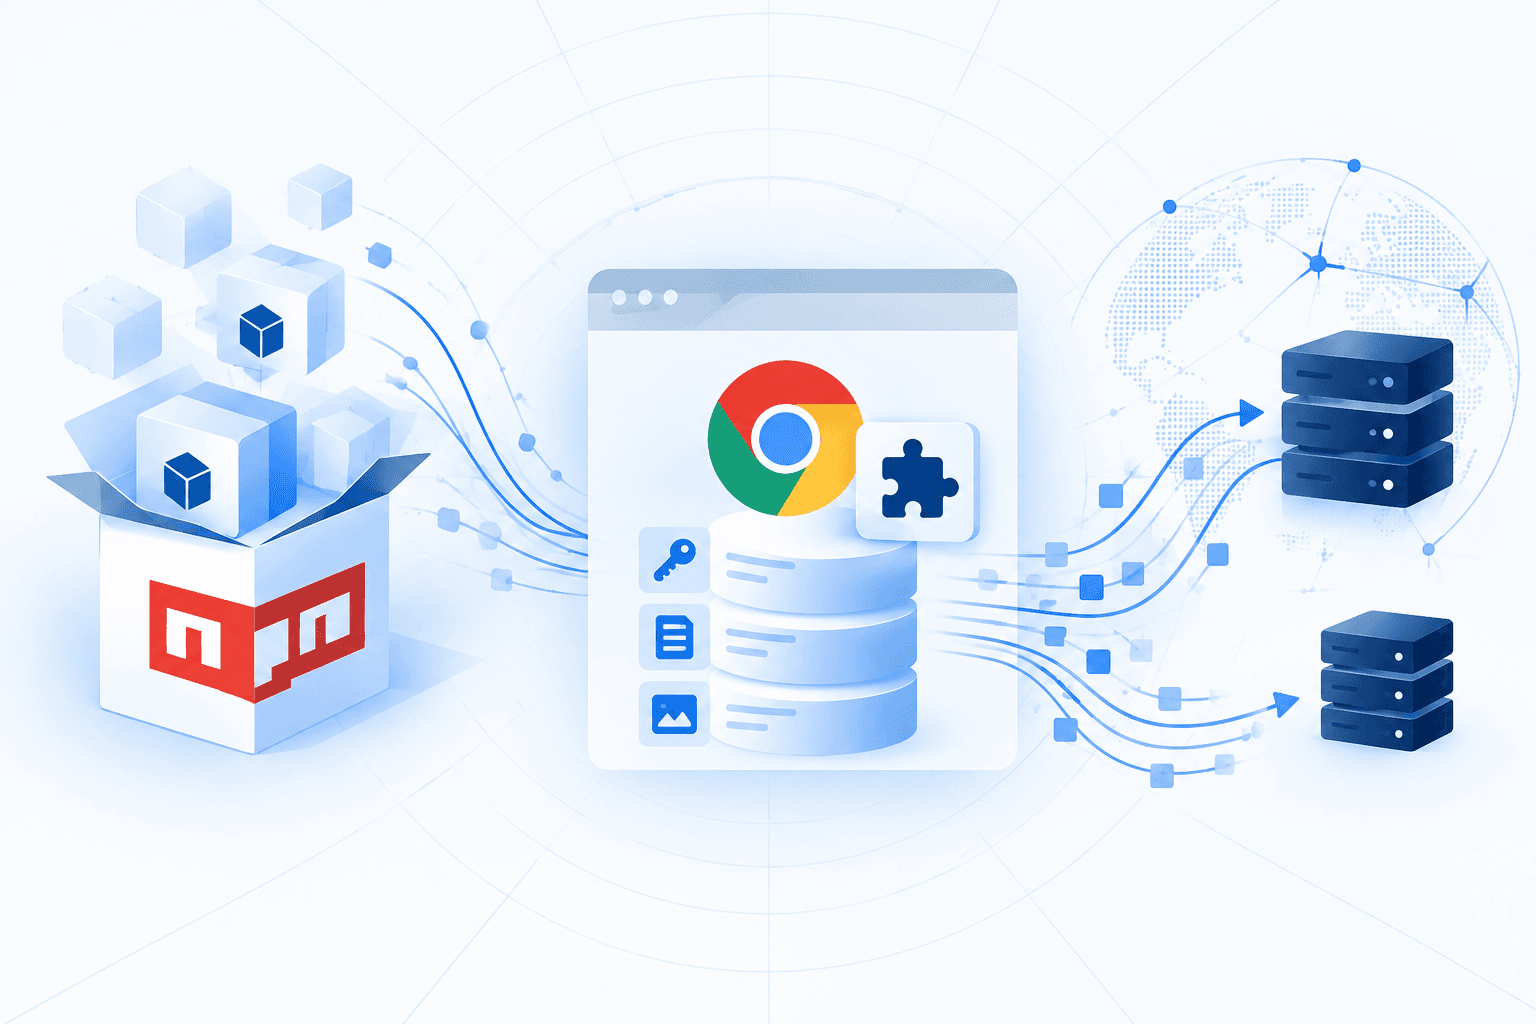
Researchers identified 13 malicious npm packages distributing WeaselBiscuit, a previously undocumented lightweight JavaScript information stealer. The malware executes when an affected package is imported, then uses Npoint.io dead-drop URLs to retrieve its payload and configuration, profile the host, and exfiltrate Chrome extension storage from Windows, macOS, and Linux devices.
When directed by its command-and-control infrastructure, WeaselBiscuit can also collect clipboard contents and record keystrokes on Windows. Its functionality and operational tradecraft overlap with BeaverTail and OtterCookie malware used in the DPRK-linked Contagious Interview campaign, although researchers said the available evidence does not support definitive attribution to North Korea.
Trace attribution and downstream blast radius.
4 events from the most recent confirmed update back to the earliest known activity.
Cisco Talos identified the malicious node-nvm-ssh npm package, which displayed characteristics associated with both BeaverTail and OtterCookie malware, in October 2025.
NTT Security Holdings publicly documented OtterCookie, malware combining information-stealing functions with remote command execution, in December 2024.
The cross-platform BeaverTail information stealer and downloader was active in the DPRK-associated Contagious Interview campaign from at least late 2022, targeting software developers, IT professionals, and cryptocurrency users.
Researchers identified 13 malicious npm packages delivering the previously undocumented WeaselBiscuit JavaScript stealer. The malware runs when an affected package is imported, loads in memory from Npoint.io dead-drop URLs, and collects Chrome extension storage across Windows, macOS, and Linux; it can also capture clipboard data and keystrokes on Windows when directed by its C2 server.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
See attribution and downstream blast radius, and whether this package or vendor reaches your builds.
3 references tracked. Mallory keeps watching after this page renders.
mkd-cirt.mk
Open sourcethehackernews.com
Open sourceopensourcemalware.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
A malicious npm campaign used the account **`gemini-check`** to publish trojanized packages including **`gemini-ai-checker`**, **`express-flowlimit`**, and **`chai-extensions-extras`**, disguising them as legitimate developer utilities while delivering a staged JavaScript payload from Vercel-hosted infrastructure. Researchers linked the malware to **OtterCookie**, a modular Node.js backdoor associated with the DPRK-linked **Contagious Interview** activity cluster, citing overlaps in payload design, remote access capability, and data-theft behavior. The packages were downloaded more than 500 times in total, and while **`gemini-ai-checker`** was removed, the other packages were still available at the time of reporting. The malware executed code in memory to reduce detection and then stole browser credentials, cryptocurrency wallets, files, clipboard contents, and developer secrets. It also explicitly targeted directories tied to AI coding tools including **Cursor**, **Claude**, **Gemini CLI**, **Windsurf**, **PearAI**, and **Eigent**, enabling theft of API tokens, conversation logs, source code, SSH keys, and cloud credentials. The campaign shows a software supply-chain intrusion aimed directly at developers, with a particular focus on compromising AI-assisted development environments and the sensitive access they contain.
Jun 29, 2026
North Korea-linked threat actors have significantly expanded the 'Contagious Interview' campaign, targeting software developers in the crypto and Web3 sectors by uploading 197 new malicious npm packages designed to distribute an updated version of the OtterCookie infostealer. These actors, posing as recruiters on platforms like LinkedIn, use sophisticated social engineering tactics such as fake job interviews and trojanized demo projects to lure victims on Windows, Linux, and macOS. The campaign leverages a full delivery infrastructure, including a threat actor–controlled GitHub account and Vercel-hosted staging sites, to store and deliver malware, with command and control servers used for data theft and remote tasking. The campaign's payloads include the BeaverTail and OtterCookie infostealers and the InvisibleFerret RAT, and the malicious npm packages have been downloaded over 31,000 times, highlighting the scale and persistence of the operation. Technical analysis reveals that the attackers have built a robust malware delivery system, using their GitHub account to host repositories and fetch the latest payloads from Vercel, while maintaining separate C2 infrastructure for exfiltration and tasking. At least five npm packages, including 'tailwind-magic' and its variants, have been directly linked to this campaign. The operation demonstrates the increasing sophistication of North Korean supply chain attacks, with a focus on compromising developers in high-value sectors through open-source ecosystems. Security researchers continue to monitor the evolving tactics and infrastructure associated with this campaign, warning organizations and developers to exercise heightened vigilance when interacting with unsolicited job offers and npm packages.
Jun 29, 2026
Researchers reported a broad software supply chain campaign targeting developers and cryptocurrency users through hijacked packages, browser extensions, and compromised maintainer accounts across ecosystems including **npm**, **Go**, **Chrome**, and **Packagist**. Socket linked the activity to North Korean actors associated with the **Contagious Interview** operation and identified 108 malicious packages and extensions spanning 162 release artifacts, while JFrog separately analyzed hijacked npm packages `html-to-gutenberg` `4.2.11` and `fetch-page-assets` `1.2.9` that were uploaded with malicious code. The activity appears to rely on account hijacking rather than compromise of GitHub itself, and some attacker infrastructure reportedly remains active even after certain packages were removed. The malware chain used unusual delivery and evasion techniques aimed at developer workstations, including a **VS Code folder-open task** instead of standard npm lifecycle scripts, JavaScript hidden in a fake font file, and encrypted payload retrieval from blockchain transaction data on **TRON**, **Aptos**, and **BNB Smart Chain**. Researchers said the campaign deployed components including **BeaverTail**, **DEV#POPPER RAT**, **OmniStealer**, a `socket.io` backdoor, and a Python infostealer to steal browser credentials, password-manager contents, cryptocurrency wallet data, developer secrets, and operating system credential-store material across **Windows**, **macOS**, and **Linux**. Security firms warned that affected developer systems and credentials should be treated as fully compromised.
Aug 3, 2026