ShinyHunters Defaces Clop Leak Site and Claims Theft of Onion-Service Keys
Threat Actor Intelligence · 20 sources · Updated 1mo ago · First seen Sep 19, 2026
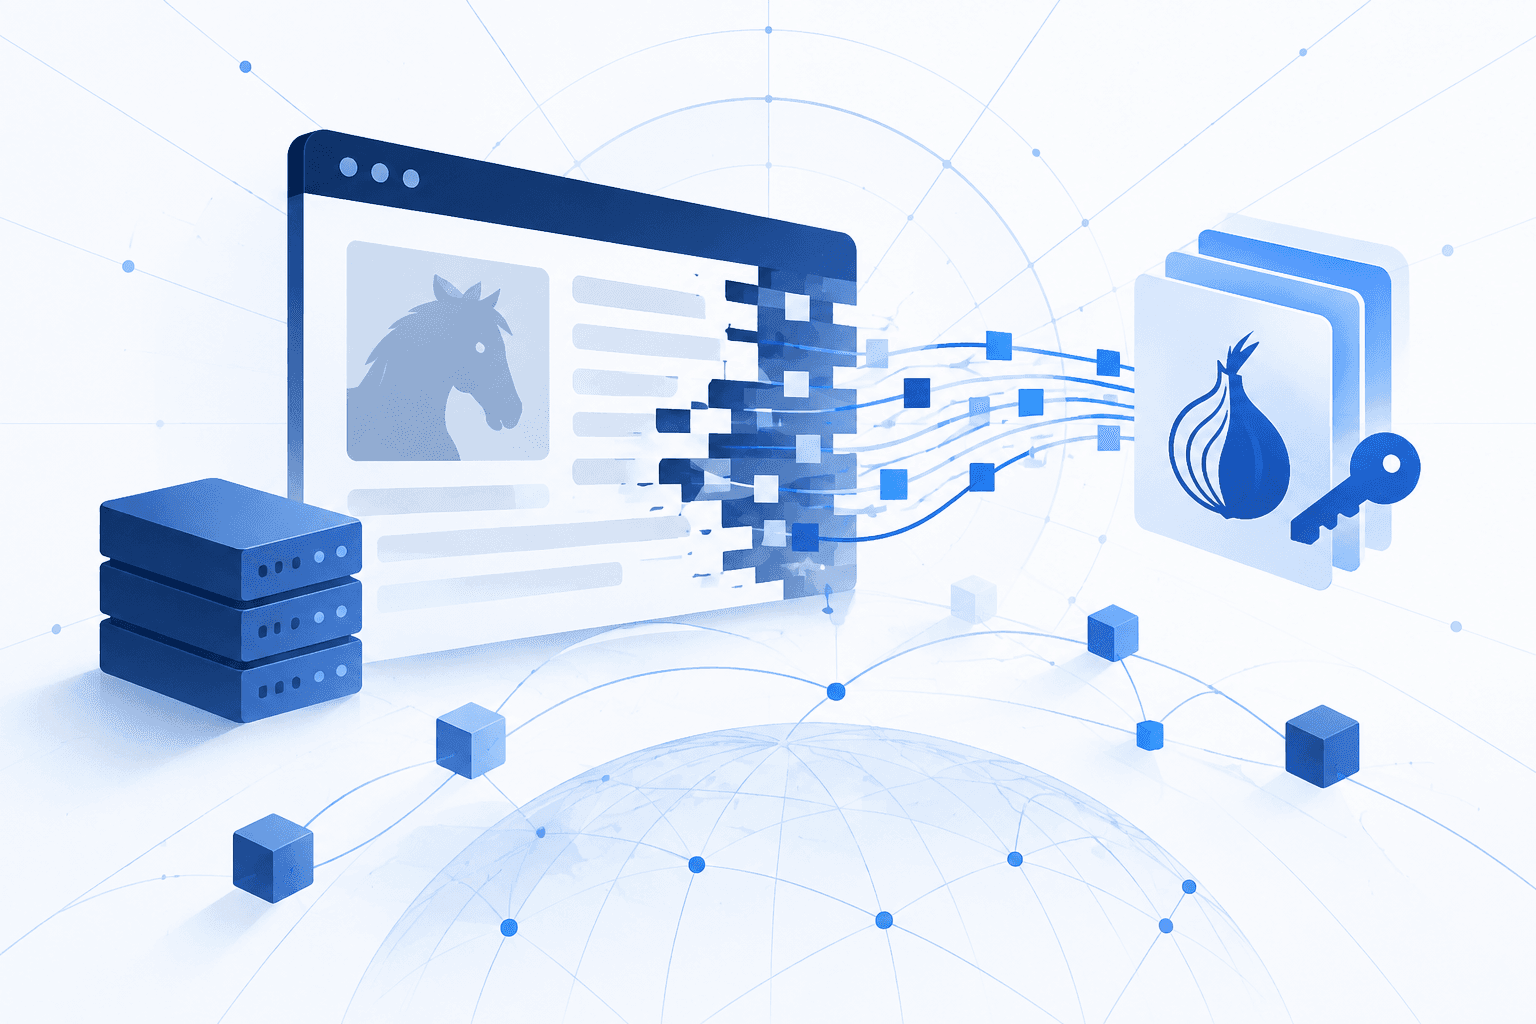
ShinyHunters allegedly breached and defaced the Tor-based data-leak site of the Clop/Cl0p ransomware operation following a dispute between the cybercrime groups. The group said it exploited an unauthenticated file-upload flaw in Grav CMS, first placing a taunting text file on the site and then replacing it with an Umbreon-themed defacement page.
ShinyHunters claimed it obtained full server access and stole Clop source code, Grav CMS plugins, logs, server data, and private keys for the operation's onion service. It has threatened to extort Clop using the purportedly stolen material; however, the asserted access and data theft have not been independently verified. The conflict is reportedly tied to Clop's alleged threats and its 2025 Oracle E-Business Suite extortion campaign involving CVE-2025-61882.