Cloudflare Automatic Key Exchange Cuts Origin TLS Handshake Retries
Emerging Technology Risk · 2 sources · Updated 2mo ago · First seen Sep 20, 2026
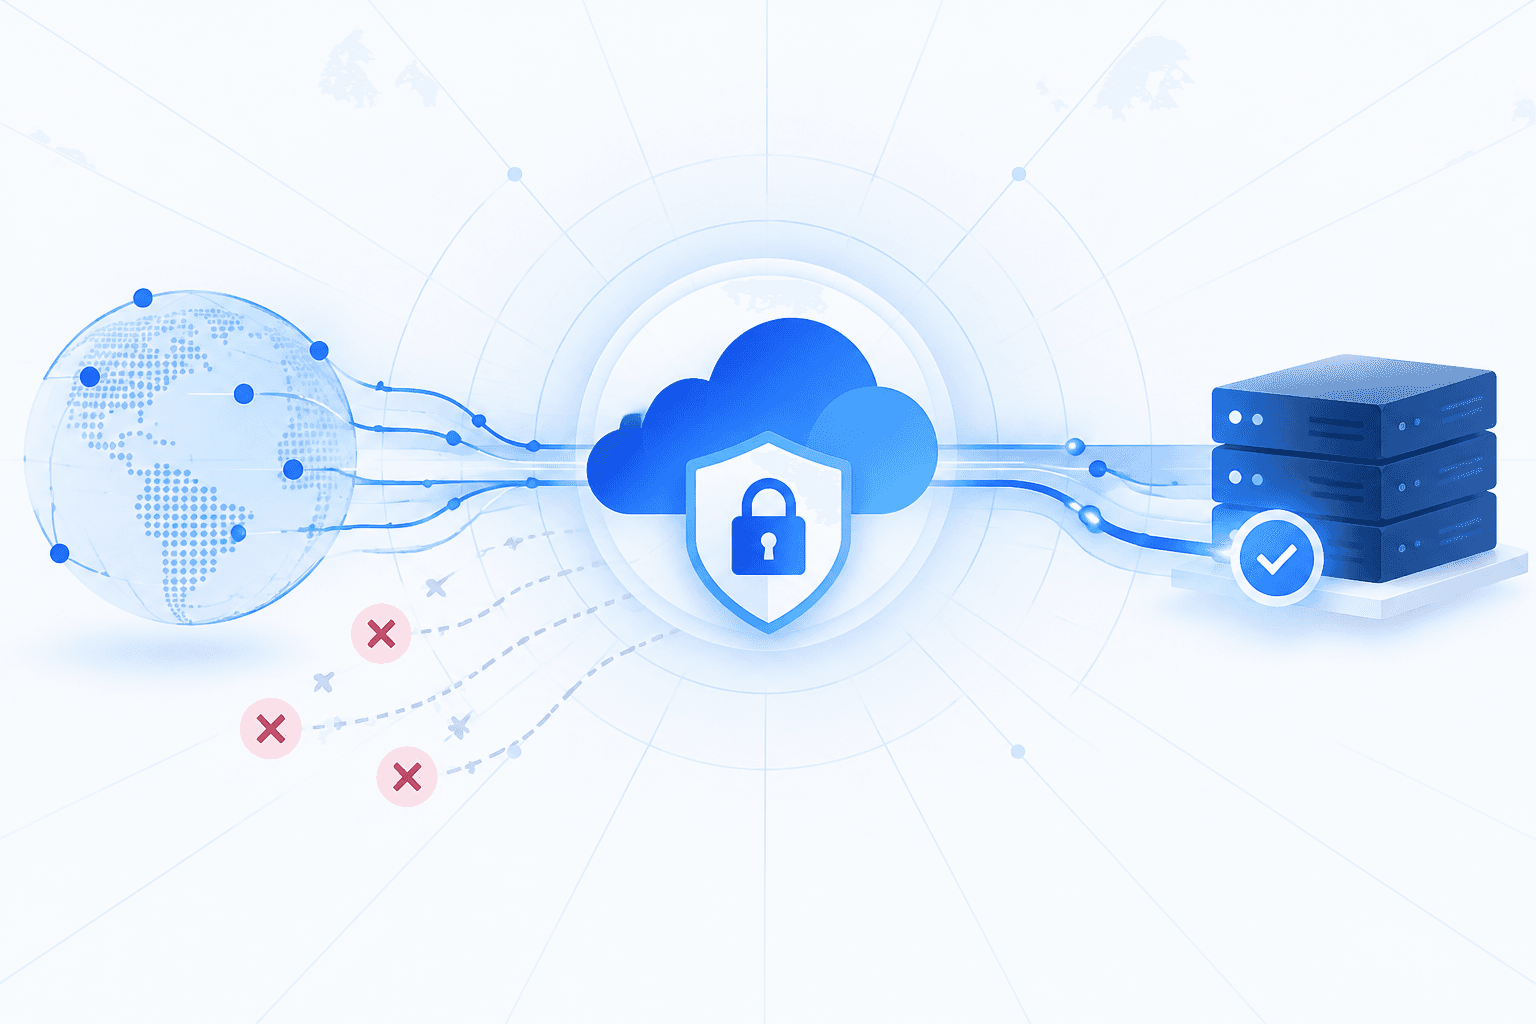
Cloudflare deployed Automatic Key Exchange for TLS connections between its edge network and customer origins, replacing a universal X25519 key-agreement assumption with per-origin measurements of supported and preferred key-exchange groups. The system probes origins outside production traffic, refreshes results daily, and gradually applies learned settings with rollback controls when connection failures or retry rates increase.
For scanned origins, the change reduced TLS HelloRetryRequest rates from roughly 52% to 3.7% and cut more than 150 ms from p90 handshake latency. It also enables most compatible X25519MLKEM768 post-quantum hybrid handshakes to complete in one round trip, although legacy origins may reject the larger ClientHello key share and strict TLS compliance policies can prevent TLS 1.3 connections where no mutually permitted algorithm exists.