PAYLOAD Ransomware Uses Active Directory GPOs for Encryptionless Extortion
Threat Actor Intelligence · 11 sources · Updated 1mo ago · First seen Apr 16, 2026
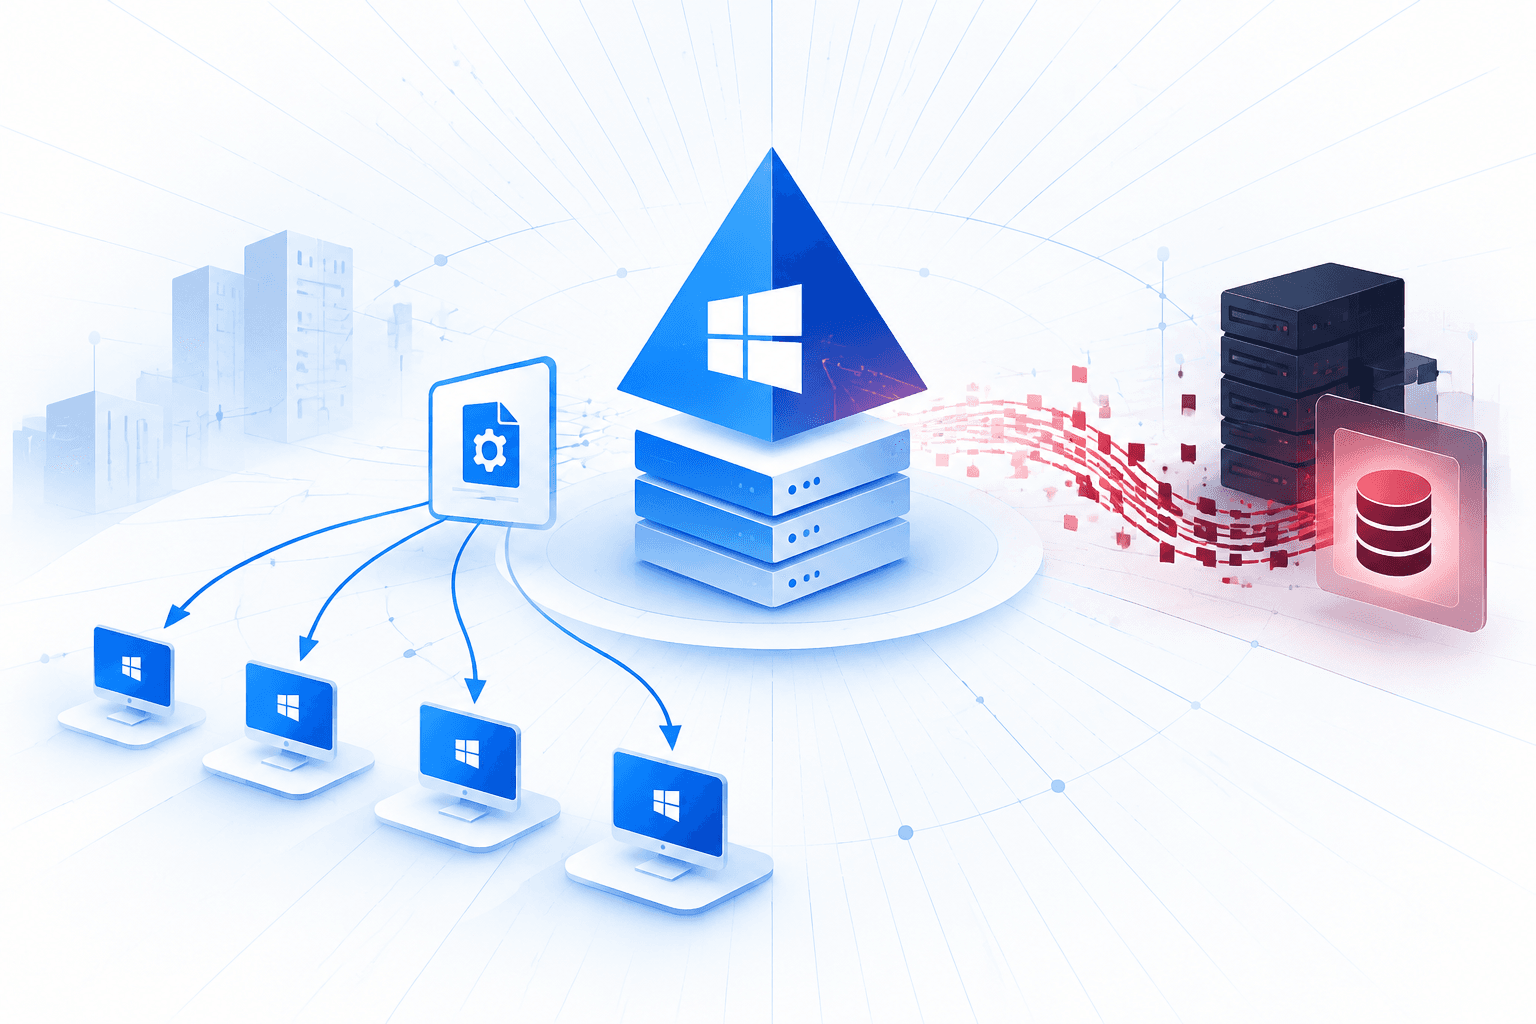
A PAYLOAD ransomware affiliate compromised a Middle Eastern manufacturing organization in April 2026 using a valid domain credential through a FortiGate SSL VPN. After obtaining domain-admin-equivalent Group Policy permissions, the actor linked malicious GPOs at the Active Directory domain root to distribute ransom notes, alter endpoint wallpapers and lock screens, set a ransom logon banner, disable local Administrator accounts, and disable Windows Firewall. Investigators found no encrypted Windows files, persistent endpoint malware, or active malicious processes; Active Directory and SYSVOL served as the attack control plane. The attackers exfiltrated data from file servers and other systems, later publishing it on the dark web, while an ESXi-targeting PAYLOAD sample was identified on Linux servers.
The intrusion reflects the growth of encryptionless extortion, in which operators steal data and coerce victims without necessarily deploying file-encrypting malware. Extortion activity reached 6,182 reported incidents in 2025, while ransomware leak sites claimed 4,737 victims; attackers commonly combine stolen credentials, privilege escalation, legitimate administrative tooling, and centralized deployment mechanisms such as Group Policy. Organizations should prioritize MFA and monitoring for remote access, least-privilege controls over GPO administration, auditing of domain-root GPO changes and SYSVOL, rapid credential containment, and defenses against data exfiltration alongside endpoint ransomware controls.