Meta Muse macOS Zero-Day Lets Local Malware Hijack Dictation and Steal Accounts
Vulnerability Disclosure · 15 sources · Updated 1mo ago · First seen Sep 21, 2026
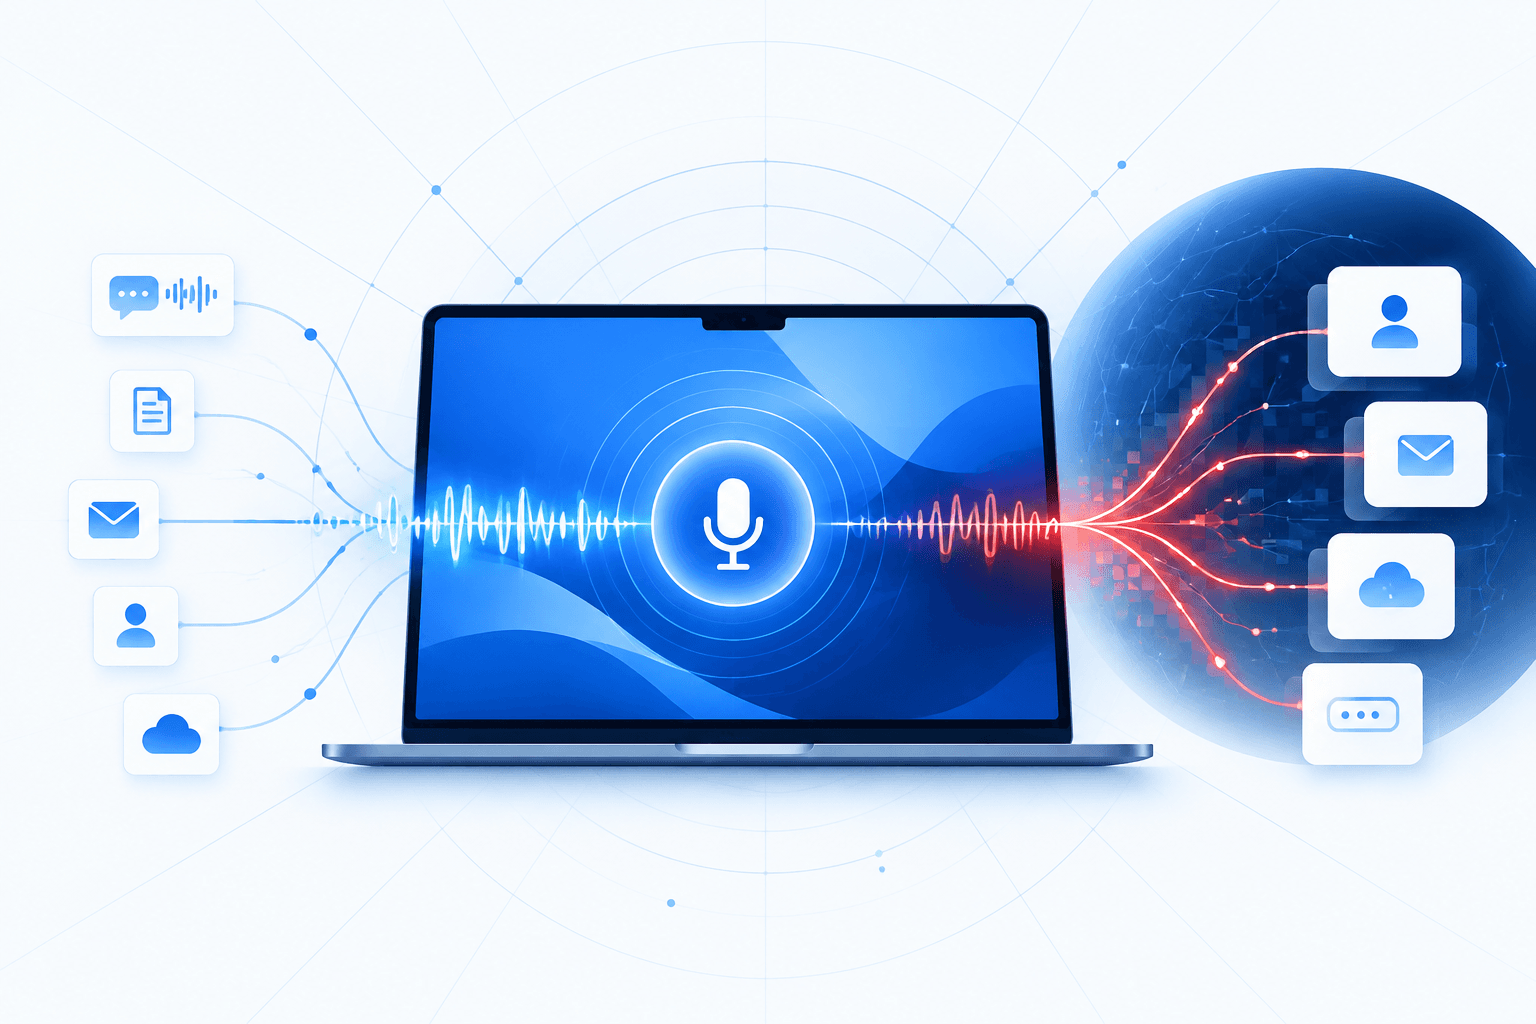
A zero-day vulnerability dubbed not-a-mused in Meta's Muse AI application for macOS lets any unprivileged process already running on a device modify undocumented Muse settings, including endo_voyager_dictation_endpoint. Malware can redirect dictated audio and AI prompt traffic to an attacker-controlled transcription endpoint, exposing sensitive voice data and enabling prompt injection.
The redirected requests can also disclose a token that authenticates the victim's Muse account, allowing an attacker to take complete control of it. Researchers warn that Muse's broad user-granted permissions can let local malware effectively bypass macOS permission separation and abuse access available to the assistant; Meta had not responded publicly, while Amazon reportedly began blocking Muse from its website.