Teams Help-Desk Impersonation Delivers SynkLoader to Steal Windows Passwords
Social Engineering & Fraud · 2 sources · Updated 2mo ago · First seen Sep 22, 2026
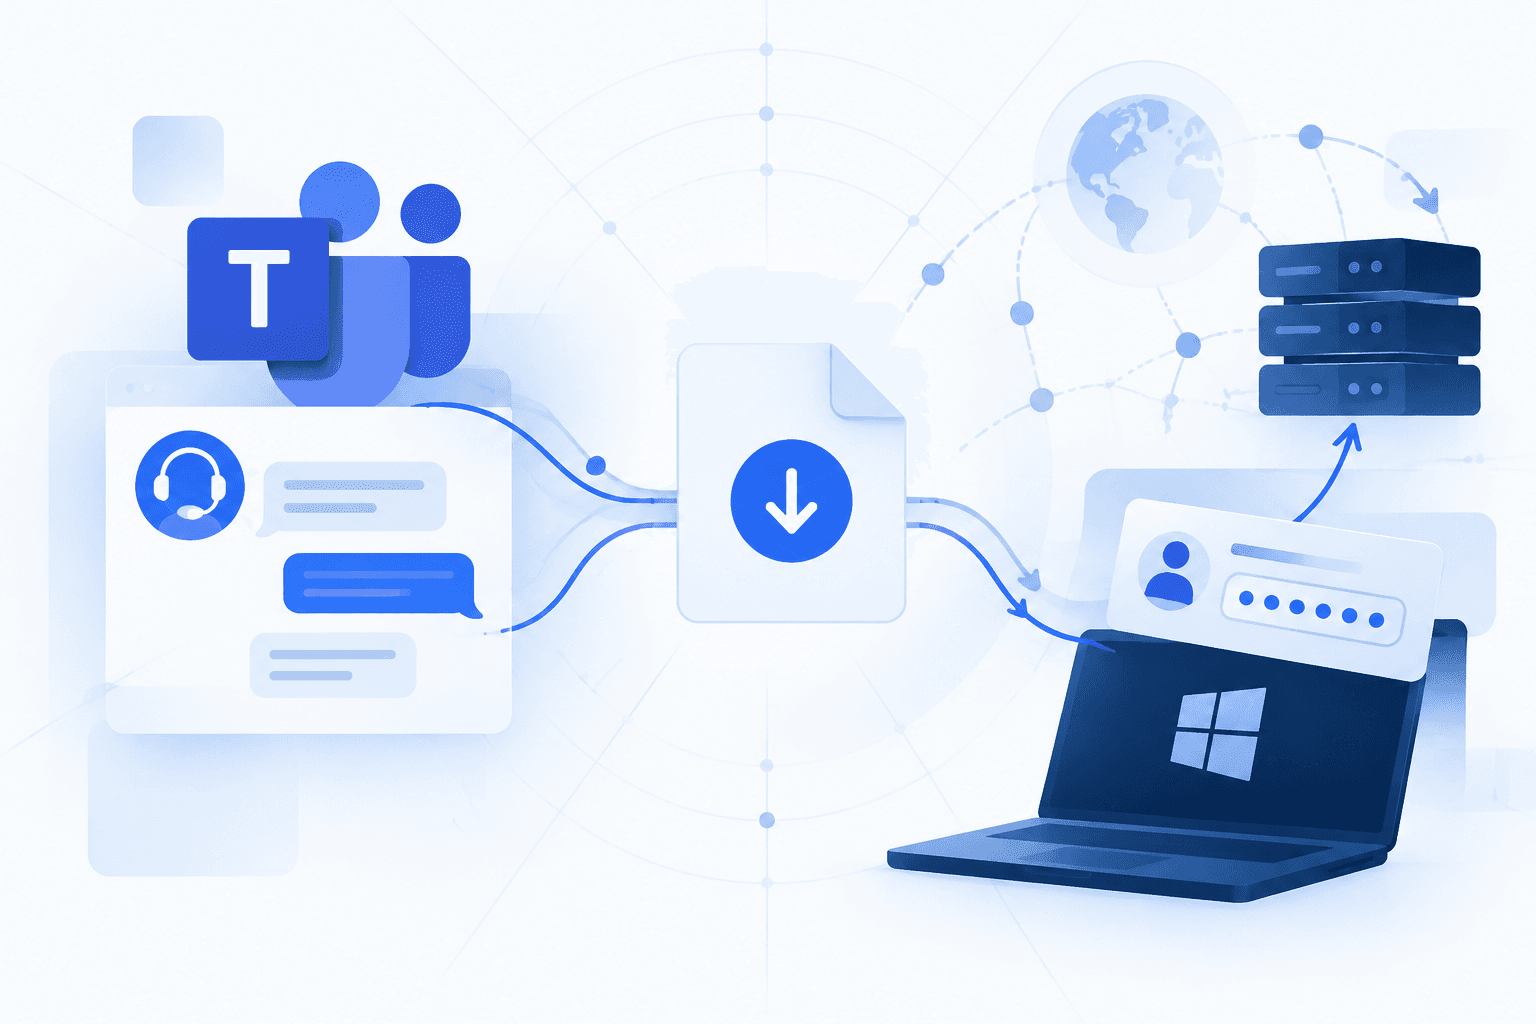
Threat actors are using Microsoft Teams external chats to impersonate internal IT help-desk staff, persuading employees to install malware or grant remote access. The campaign relies on attacker-controlled Microsoft 365 tenants and trusted-looking display names such as “IT Service Desk,” exploiting permissive cross-tenant communication rather than a Microsoft Teams software vulnerability.
One reported operation delivered SynkLoader through a malicious MSI sent in a Teams phishing message. SynkLoader establishes persistence through scheduled tasks and deploys a PhishLocker component that displays a counterfeit Windows lock screen to capture plaintext credentials. Organizations should limit Teams external communications to trusted domains, ensure external-sender indicators are visible, and require employees to independently verify unsolicited support contacts.