
Loading story…
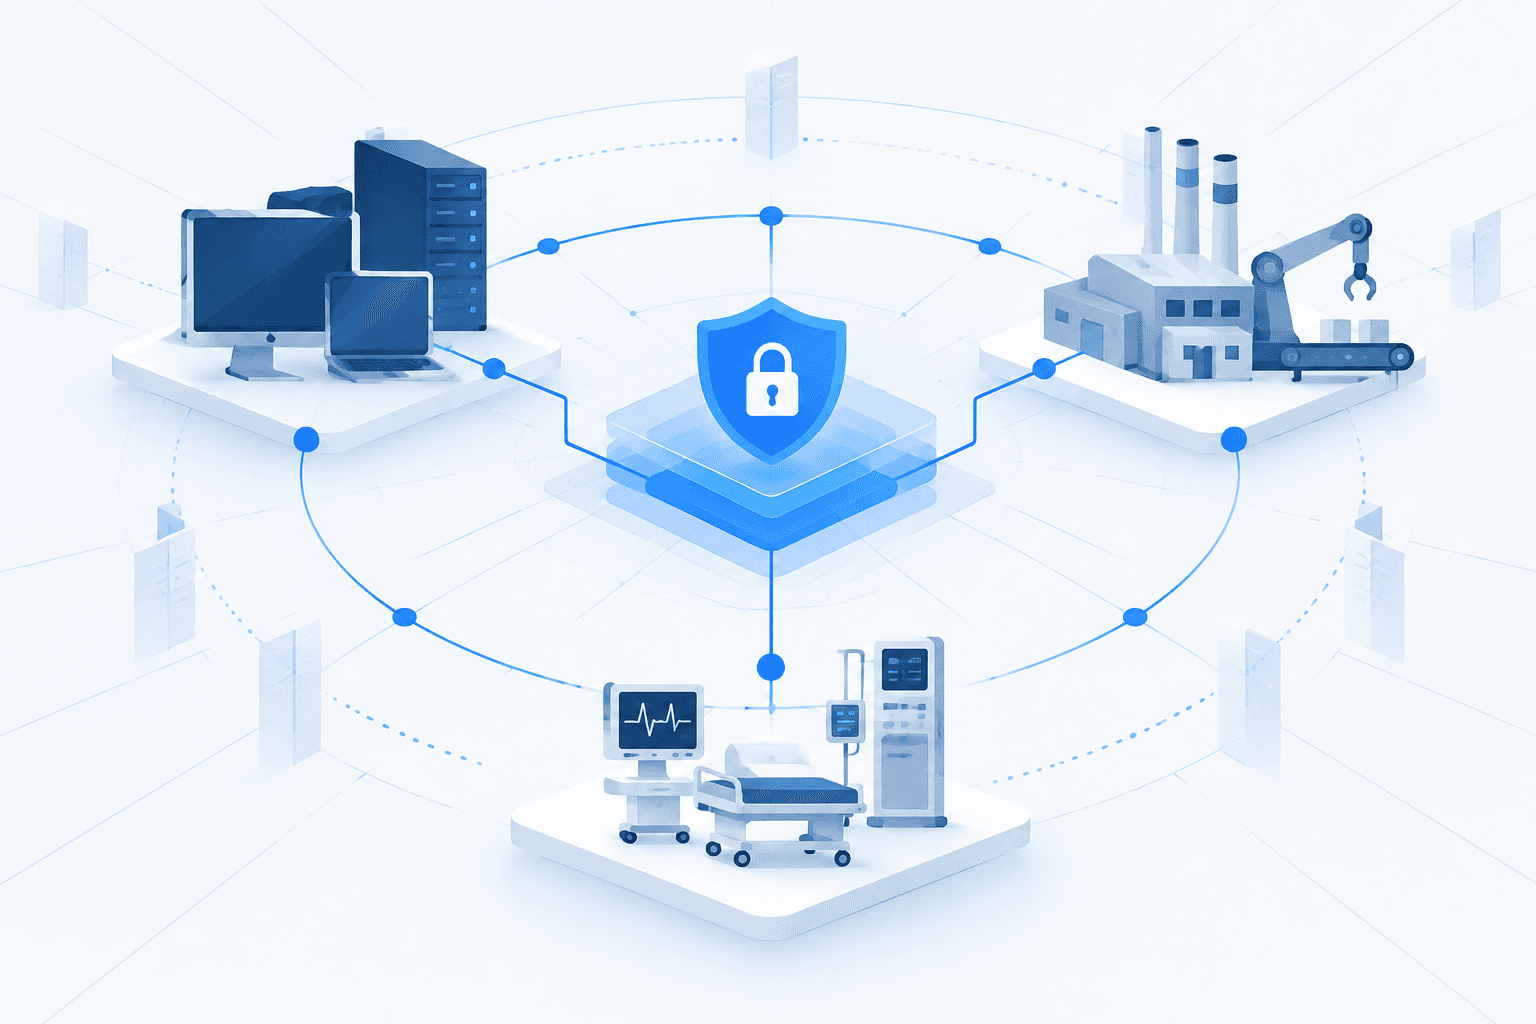
Forescout Vedere Labs analyzed 47,700 network segments encompassing more than 2.5 million devices at 209 organizations and found extensive mixing of enterprise IT, operational technology (OT), IoT, and internet-of-medical-things (IoMT) assets. Only 13% of segments containing OT devices were dedicated exclusively to OT, while only 6% of IoMT-containing segments were limited to medical devices; IP cameras and point-of-sale environments were among the most frequently co-segmented with workstations and servers.
The mixed and oversized segments increase the potential blast radius of a single compromised device, enabling lateral movement from exposed or weakly secured connected assets into corporate or critical operational systems. Forescout cited ransomware and camera compromises as examples of this risk and urged organizations to maintain continuous asset inventories, identify risky device-convergence zones, isolate critical OT and IoMT assets in smaller purpose-built segments, restrict unnecessary inter-segment traffic, and monitor for segmentation drift.
Get the actors, campaigns, and ATT&CK mapping behind it.
4 events from the most recent confirmed update back to the earliest known activity.
The pro-Russian hacktivist group NoName057(16) conducted examples of exposed IP-camera compromises against Estonian and Canadian targets in late August and early September.
Forescout tracked more than 300 instances of hacktivist groups gaining control of exposed IP cameras at targeted organizations.
The Akira ransomware group used poorly segmented IP cameras to bypass endpoint detection and response controls, demonstrating how camera access could provide a route into corporate networks.
Forescout Vedere Labs analyzed 47,700 network segments across 209 organizations, finding that OT, IoMT, IoT, and enterprise IT devices were frequently co-segmented. The study found that only 13% of OT-containing segments and 6% of IoMT-containing segments were exclusively dedicated to those device categories.
Get the adversaries, campaigns, and ATT&CK mapping behind this technique, with detections ready to deploy.
3 references tracked. Mallory keeps watching after this page renders.
itsecurityguru.org
Open sourcesecurityweek.com
Open sourceinfosecurity-magazine.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Enterprises are increasingly exposed to cybersecurity risks due to the proliferation of unmanaged and diverse extended Internet of Things (xIoT) and operational technology (OT) devices within their networks. Research analyzing over 10 million devices across 700 organizations found that two-thirds of networked devices are not traditional IT assets, but rather include network gear, OT, IoT, and medical equipment. Common high-risk device types such as VoIP phones, IP cameras, point-of-sale systems, and uninterruptible power supplies are often widespread yet remain unmanaged, creating significant security blind spots. The diversity of device functions, vendors, and operating system versions further complicates risk management, making it challenging for security teams to identify, patch, and mitigate vulnerabilities effectively. Manufacturers, in particular, face heightened OT security challenges due to legacy technology, lack of asset visibility, and the growing number of access points resulting from mergers and acquisitions. The complexity of managing access permissions, especially with multiple users sharing admin accounts, increases the difficulty of incident response and overall security posture. Despite increased awareness of these risks, the combination of device diversity, legacy systems, and human factors continues to present substantial obstacles to securing enterprise and manufacturing environments against cyber threats.
Jun 29, 2026
Recent research highlights that enterprise networks are increasingly vulnerable due to a high prevalence of legacy, end-of-life (EOL) systems, unpatched devices, and poor network segmentation. Telemetry from over 27 million devices across 1,800 enterprises reveals that 26% of Linux and 8% of Windows systems are running unsupported operating systems, with 39% of IT devices lacking active endpoint security. Additionally, a significant portion of devices operate outside IT control, and 77% of corporate networks are poorly segmented, allowing low-security devices to share network space with high-value assets, increasing the risk of lateral movement by attackers. Simultaneously, critical infrastructure sectors such as energy, healthcare, government, and transportation are experiencing a surge in cyberattacks targeting IoT and Android devices. Attackers are exploiting the interconnectedness of these industries for financial gain, with the U.S. being the primary target. The rise in attacks underscores the need for stringent tracking of user behaviors, robust access controls, accurate asset inventories, and improved network segmentation to mitigate risks posed by unmanaged and vulnerable devices in both enterprise and critical infrastructure environments.
Jun 29, 2026
Industrial and building-automation environments continue to expose **operational technology (OT)** services directly to the public internet, increasing the likelihood of unauthorized access and disruption. An *Intelligence-Driven Active Defense Report 2026* cited by Palo Alto Networks/Siemens/Idaho National Laboratory data indicates internet exposure is growing sharply, with *Cortex Xpanse* reporting **110M+ observations** of exposed OT devices in 2024 and fingerprinting **19.6M unique OT devices/services** across **1.77M IPv4 addresses**; the highest concentrations were observed in the **US, China, and Germany**. Frequently observed exposed products included **Tridium Niagara**, **Linear eMerge**, and **Saia PCD Web Server**, and common exposure points included standard web ports `TCP/443` and `TCP/80` alongside OT/building-automation-associated ports such as `TCP/502`, `UDP/47808`, and Niagara-related ports like `TCP/4911` and `TCP/5011`. Similar internet-exposure risk was observed in healthcare, where Rapid7 Labs reported **30+ UK-based systems** responding to **DICOM** requests over `TCP/104` (the default medical imaging port) from the public internet. Rapid7 stated it used *Project Sonar* to validate service responsiveness only and did not attempt to access records, but warned that externally reachable DICOM services—especially without VPN restriction or encryption—are readily discoverable via routine scanning and were not designed for hostile networks. Prior research cited in the report indicates misconfigured or poorly controlled **PACS/DICOM** deployments can leak sensitive metadata (including patient identifiers) and may be susceptible to data reconstruction or modification, creating both **cybersecurity** and **patient safety** risk.
Jun 29, 2026