
Loading story…
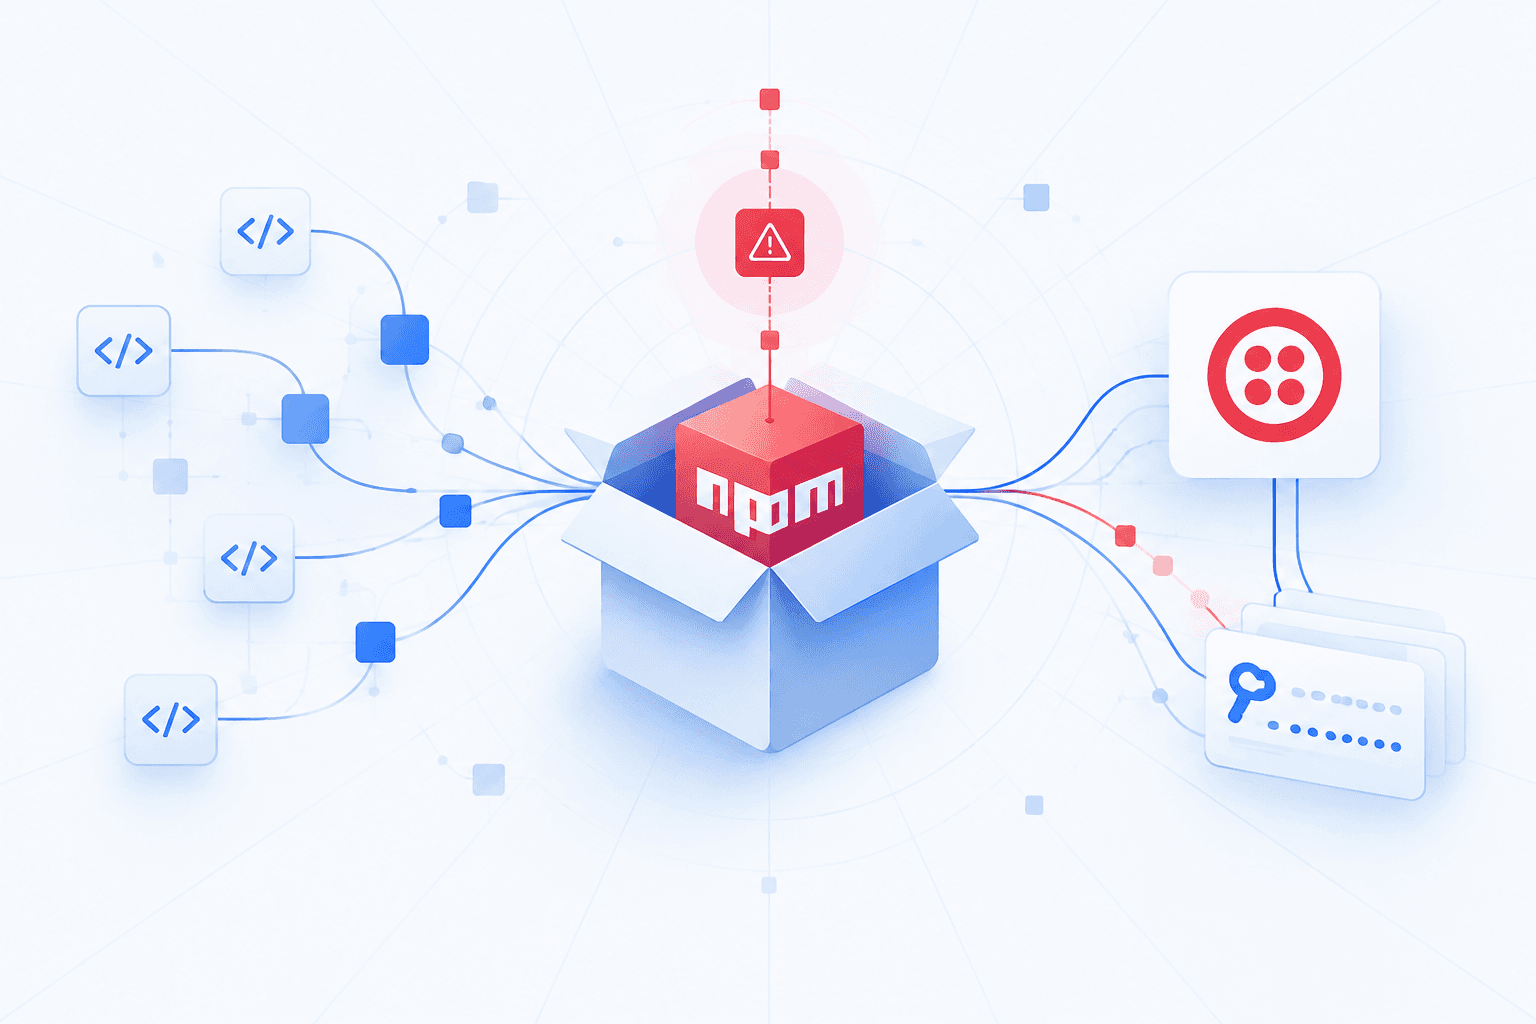
A malicious npm package, tw-pkgprobe-7731, impersonated an authorized Twilio HackerOne bug-bounty research tool to target developers integrating Twilio APIs. Published in 11 rapid-fire versions by the unrelated npm account twdepprobe7731, it profiled developer environments and exfiltrated host and environment data through a webhook; version 1.0.4 specifically attempted to steal ACCOUNT_SID and AUTH_TOKEN credentials.
Some releases searched for Twilio account-SID-related directories and attempted to inject a custom proof-of-concept package into installed packages and node_modules; later versions also performed OSINT against Twilio-related hosts and the AWS instance-metadata endpoint. ReversingLabs said the package violated Twilio's bug-bounty rules and naming requirements, assessed the campaign as likely low sophistication due to its unobfuscated code and weak impersonation, and reported that npm removed the package after notification.
Trace attribution and downstream blast radius.
5 events from the most recent confirmed update back to the earliest known activity.
Later package versions reverted to basic environment probing, while the final releases probed Twilio-related hosts for OSINT and attempted to request AWS instance metadata from 169.254.169.254. The AWS metadata was not used or exfiltrated, according to ReversingLabs.
Version 1.0.4 attempted to exfiltrate the Twilio process.env.ACCOUNT_SID and process.env.AUTH_TOKEN values through a webhook, credentials that could enable unauthorized API activity, communications, and billing charges.
Versions 1.0.1 through 1.0.3 searched for directories associated with targeted Twilio account SIDs, scanned installed npm packages and node_modules directories, and wrote custom package.json and index.js files into targeted locations.
The unrelated npm account twdepprobe7731 published tw-pkgprobe-7731, falsely presenting it as an authorized Twilio HackerOne research probe. Its initial version checked for a Twilio development environment and exfiltrated collected environment and host data to an external webhook when the check succeeded.
npm removed the tw-pkgprobe-7731 packages after ReversingLabs notified the registry of the malicious campaign.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 11 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
See attribution and downstream blast radius, and whether this package or vendor reaches your builds.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Security researchers have uncovered multiple campaigns involving malicious npm packages designed to steal developer credentials and sensitive information from Windows, macOS, and Linux systems. In one operation, ten typosquatted packages impersonated popular libraries such as TypeScript, discord.js, ethers.js, and others, using sophisticated obfuscation, fake CAPTCHA prompts, and postinstall hooks to deploy an information stealer that harvested credentials from system keyrings, browsers, and authentication services. The malware executed in a new terminal window to evade detection and sent stolen data, including IP addresses, to external servers. Another large-scale campaign, dubbed 'PhantomRaven,' involved 126 npm packages and over 86,000 downloads, targeting authentication tokens, CI/CD secrets, and GitHub credentials. These packages leveraged remote dynamic dependencies to fetch and execute payloads during installation, profiling infected devices and exfiltrating secrets for potential supply chain attacks. The attackers employed techniques such as slopsquatting, where AI-generated package recommendations led developers to install non-existent, malicious packages. Some packages impersonated tools from GitLab and Apache, and many remained available on npm at the time of reporting. The campaigns highlight the ongoing risks in the npm ecosystem, with attackers exploiting both user trust and platform weaknesses to compromise developer environments and CI/CD pipelines. Security experts warn that the theft of tokens and credentials could enable further attacks, including the introduction of malicious code into legitimate projects and broader supply chain compromises.
Jun 29, 2026
Multiple malicious npm packages have been discovered targeting developers by employing advanced obfuscation techniques and typosquatting to mimic popular legitimate packages such as *TypeScript*, *discord.js*, *ethers.js*, *nodemon*, and *Claude Code*. Security researchers revealed that these packages use up to four layers of obfuscation—including eval wrapping, XOR encryption, URL encoding, and control flow manipulation—to evade static analysis and conceal credential-stealing malware. The attack chain often begins with deceptive tactics, such as displaying fake CAPTCHAs, and proceeds to exfiltrate sensitive information like IP addresses and credentials to attacker-controlled servers. In one notable case, a package impersonating the official Anthropic CLI was found to proxy commands and data back to the threat actor, enabling both credential theft and remote command execution. These incidents highlight the persistent risks posed by weak validation and oversight in the npm ecosystem, allowing threat actors to publish lookalike packages that are difficult to distinguish from legitimate ones. The sophisticated payloads not only target local developer environments but can also compromise CI/CD pipelines, amplifying the potential impact. Security experts emphasize the need for improved package metadata validation and greater vigilance among developers to mitigate the risk of supply chain attacks through open-source dependencies.
Jun 29, 2026
A coordinated software supply-chain campaign used 17 malicious npm and PyPI packages to impersonate SDKs for **PaySafe**, **Skrill**, and **Neteller**, targeting developers and CI pipelines that installed the fake libraries. The packages harvested environment variables containing API keys, tokens, passwords, and cloud credentials, then exfiltrated the data to an **ngrok**-backed command-and-control endpoint hosted on AWS infrastructure. Socket reported that the npm variants only triggered exfiltration when a Paysafe API key was present, while the PyPI packages activated more broadly through malicious `__init__.py` placement. The malware used layered obfuscation to conceal its infrastructure and included sandbox-evasion checks based on CPU count, hostname, and username to avoid analysis. The activity reflects a broader pattern of attackers planting malicious developer tooling and lookalike packages to compromise build and development environments. Defenders were urged to block the identified package names, investigate outbound connections to the reported ngrok domain, and rotate any secrets exposed in affected environments.
Jul 12, 2026