
Loading story…
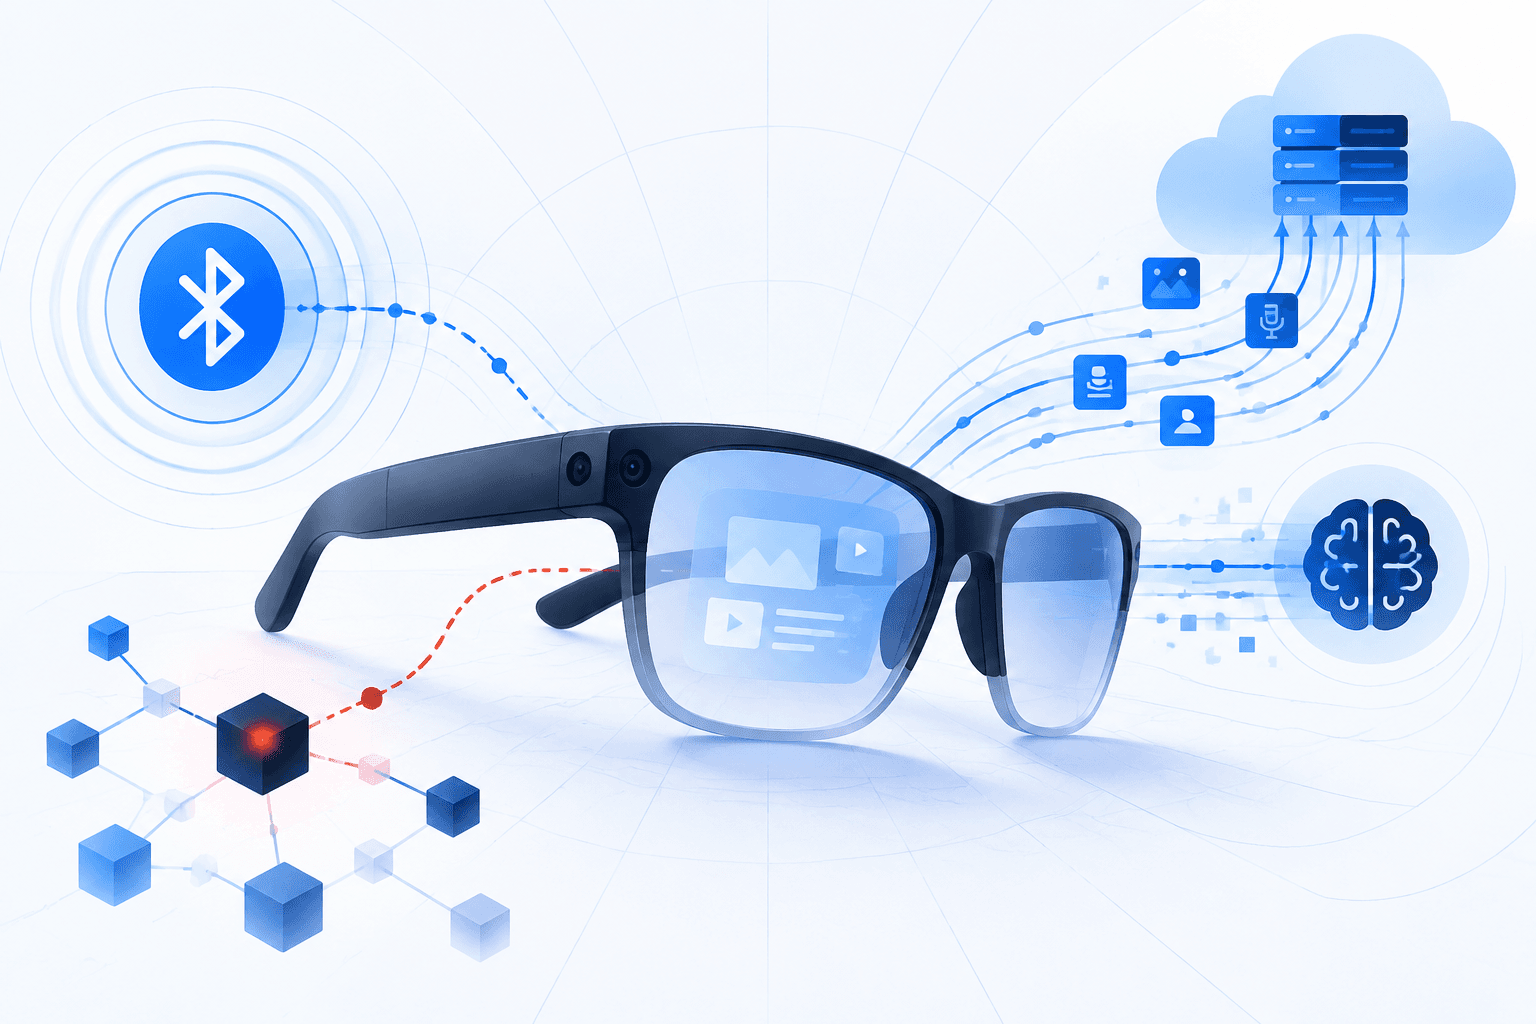
Researchers at NSB Cyber and Abstract Shield found more than a dozen security and privacy flaws affecting two low-cost smart-glasses products, their companion application, and an associated website. The most serious issue, unauthenticated Bluetooth pairing, could let a nearby attacker connect to powered-on, unpaired glasses, take photos or recordings, copy stored media, intercept traffic between the device and phone, or impersonate the glasses in the owner’s app. A Bluetooth-visible device identifier combined with a website weakness could also reveal a user’s email address and date of birth.
The researchers reported that voice, text, image, and other AI inputs were transmitted to a server in Shenzhen and could be forwarded onward; their analysis indicated Chinese sovereign AI models may be involved. The findings add to wider privacy concerns around camera-equipped smart glasses, including facial-recognition capabilities, and may raise obligations under Australian privacy law and the Cyber Security Act. Whether the products are subject to Australia’s smart-device security standards depends partly on whether they were manufactured on or after 4 March 2026.
Track how attackers are adapting to this technology.
2 events from the most recent confirmed update back to the earliest known activity.
After ABC News shared the researchers' findings, HeyCyan developers reportedly attempted to patch some of the identified security issues. Most of the vulnerabilities reportedly remained unaddressed.
NSB Cyber and Abstract Shield identified more than a dozen security and privacy issues in two inexpensive smart-glasses products, their companion app, and an associated website. The findings included unauthenticated Bluetooth pairing, potential access to recordings and stored media, exposure of personal data through a device identifier and website weakness, and AI inputs sent to a Shenzhen server.
Follow how adversaries are adapting to this technology, and where it touches your stack today.
4 references tracked. Mallory keeps watching after this page renders.
malware.news
Open sourcemalwarebytes.com
Open sourceabc.net.au
Open sourcemalwarebytes.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.

An Android app called **Nearby Glasses** was released to alert users when certain camera-equipped smart glasses are nearby by scanning **Bluetooth Low Energy (BLE)** advertising traffic for **manufacturer company IDs** (Bluetooth SIG-assigned identifiers) rather than device names, MAC addresses, or service UUIDs, which can be inconsistent or randomized. The app, developed by **Yves Jeanrenaud** (Darmstadt University of Applied Sciences), runs as a foreground service and triggers notifications when detected devices meet a configurable RSSI threshold (reported default around `-75 dBm`, roughly 10–15 meters in open space). Reported monitored IDs include Meta/Luxottica and Snapchat-related identifiers, and users can add custom hex values to expand detection. Reporting highlighted that the approach can generate **false positives**, particularly from other Bluetooth devices made by the same vendors (e.g., other Meta hardware), and the project documentation warns against using detections to harass people. The app’s emergence is framed as a response to growing privacy concerns and reported misuse of smart glasses for **non-consensual recording** and demonstrations of **real-time facial recognition** using glasses paired with public data; coverage also notes legal and regulatory risk areas (e.g., state wiretapping laws) and ongoing debate over the effectiveness of recording indicator lights and the potential for those indicators to be disabled.
Jun 29, 2026
Smart eyewear devices such as Meta Ray Ban glasses, equipped with microphones, cameras, and AI connectivity, present significant privacy and data security risks when used in hospital settings. These devices can inconspicuously record or livestream protected health information (PHI), including patient images and conversations, often without the knowledge or consent of those being recorded. The presence of a small LED indicator is insufficient as a safeguard, especially since third-party products exist to obscure the light, making unauthorized recording even harder to detect. Healthcare organizations face challenges as these are often unmanaged devices brought in by patients or staff, bypassing institutional controls and oversight. The direct connectivity of these glasses to social media platforms like Facebook and Instagram increases the risk of inadvertent or malicious disclosure of sensitive information, potentially violating HIPAA/HITECH regulations. The inconspicuous nature of smart glasses differentiates them from more obvious recording devices like smartphones, heightening the risk of unnoticed privacy breaches in clinical environments.
Jun 29, 2026
Investigations reported by Swedish outlets *Svenska Dagbladet* and *Göteborgs-Posten* found that recordings captured by **Meta Ray-Ban smart glasses**—including video and audio—are being reviewed by human contractors as part of AI training and quality assurance workflows. Workers employed by **Sama**, a Meta subcontractor in **Nairobi, Kenya**, described routinely handling highly sensitive content inadvertently recorded by users, including bathroom visits, undressing, sex/pornography, and private conversations, as well as incidental capture of **bank cards** and other identifying details; interviewees said they feared reprisals for raising concerns and described strict on-site controls intended to prevent leaks. Following the reporting, the UK’s privacy regulator, the **Information Commissioner’s Office (ICO)**, confirmed it is contacting Meta to ask questions about the devices and associated data-handling practices. While Meta’s terms reportedly disclose that some interactions may be reviewed by humans to improve the system, the reporting and worker accounts suggest the review pipeline can include intimate or identifying moments that wearers may not expect to be viewed by third parties, raising regulatory and reputational risk around consent, transparency, and safeguards for bystander and user privacy.
Jun 29, 2026