Macfinger ClickFix Campaign Delivers Atomic macOS Stealer via Compromised Websites
Malware Intelligence · 4 sources · Updated 2mo ago · First seen Sep 23, 2026
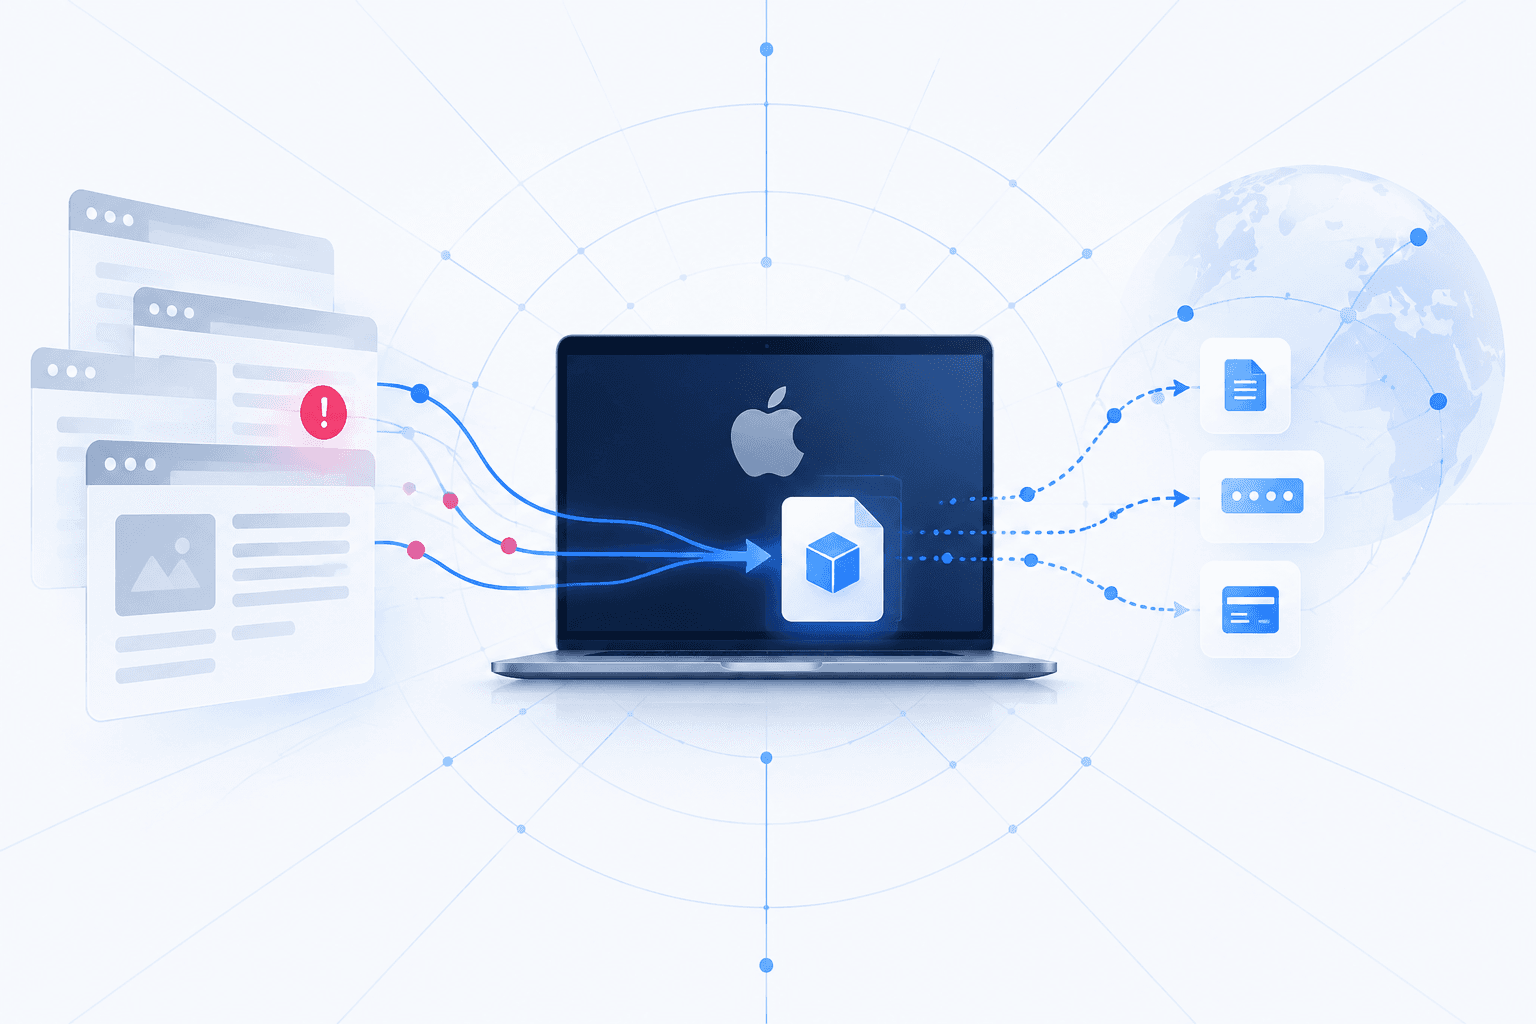
The Macfinger ClickFix campaign compromises legitimate websites by injecting JavaScript that fingerprints visitors and selectively presents macOS users with a fake bot-protection page. The page uses ClickFix-style instructions to trick victims into executing a malicious shell script, which retrieves architecture-specific Mach-O payloads for Apple Silicon or Intel-based Macs.
Post-compromise activity includes repeated telemetry and credential-submission requests to command-and-control infrastructure. Ransom-ISAC assessed the final payload as a variant of Atomic macOS Stealer (AMOS), though observed indicators differ from previously tracked AMOS activity; investigators have released IOC, packet-capture, and collected-file archives to support detection and analysis.