ClickFix macOS Campaign Abuses Script Editor to Deploy Atomic Stealer
Malware Intelligence · 9 sources · Updated 4mo ago · First seen Apr 9, 2026
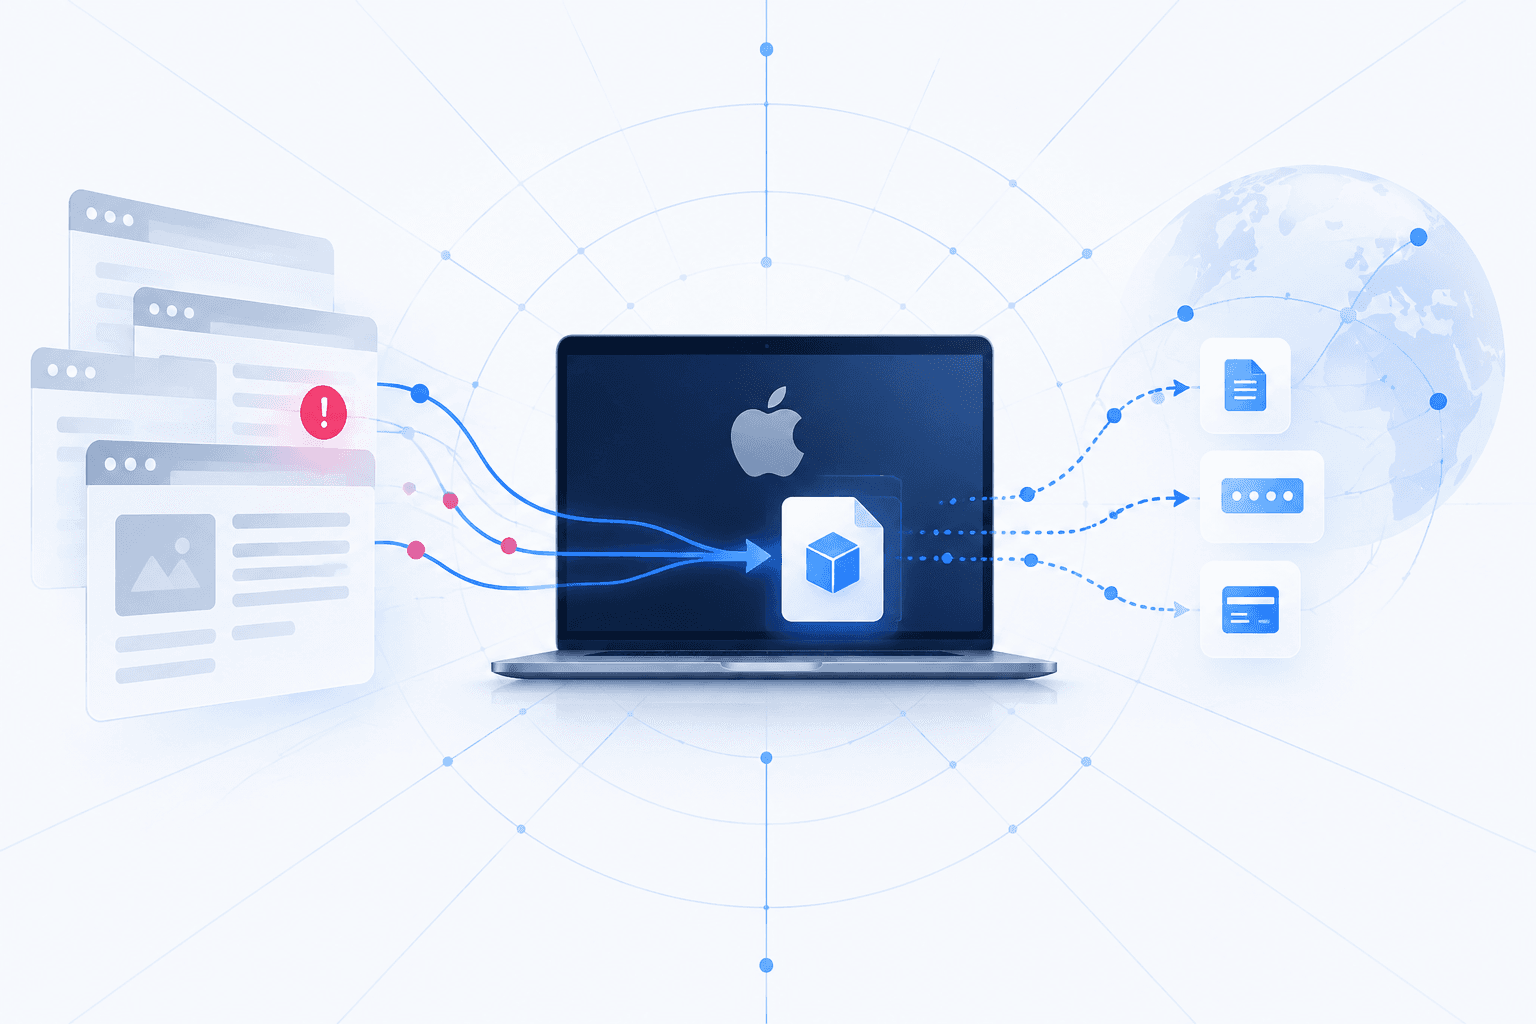
Researchers identified a ClickFix-style campaign targeting macOS users that swaps Terminal-based execution for Script Editor to bypass newer Apple protections. Victims are lured to fake Apple-themed pages such as “Reclaim disk space on your Mac,” which invoke the applescript:// URL scheme and open Script Editor with a pre-filled AppleScript. If the user runs it, the script conceals a malicious shell command that decodes a URL, uses curl with TLS certificate validation disabled, and pipes the response directly into zsh for in-memory execution.
The activity, discovered by Jamf Threat Labs, ultimately downloads and launches a Mach-O variant of Atomic Stealer, an infostealer built to harvest browser credentials, saved passwords, cryptocurrency wallets, and other sensitive data from macOS systems. Researchers said the campaign appears to be an adaptation to Apple’s paste-command scanning protections added in macOS 26.4 for Terminal abuse; while newer macOS versions also warn about unidentified scripts, the attack can still succeed if users follow the prompts. Reported infrastructure tied to the campaign includes dryvecar.com, storage-fixes.squarespace.com, and cleanupmac.mssg.me.