Public Exploit Enables Host-Root Escape From Unpatched Ubuntu Containers
Patch & Detection Intelligence · 2 sources · Updated 2mo ago · First seen Sep 23, 2026
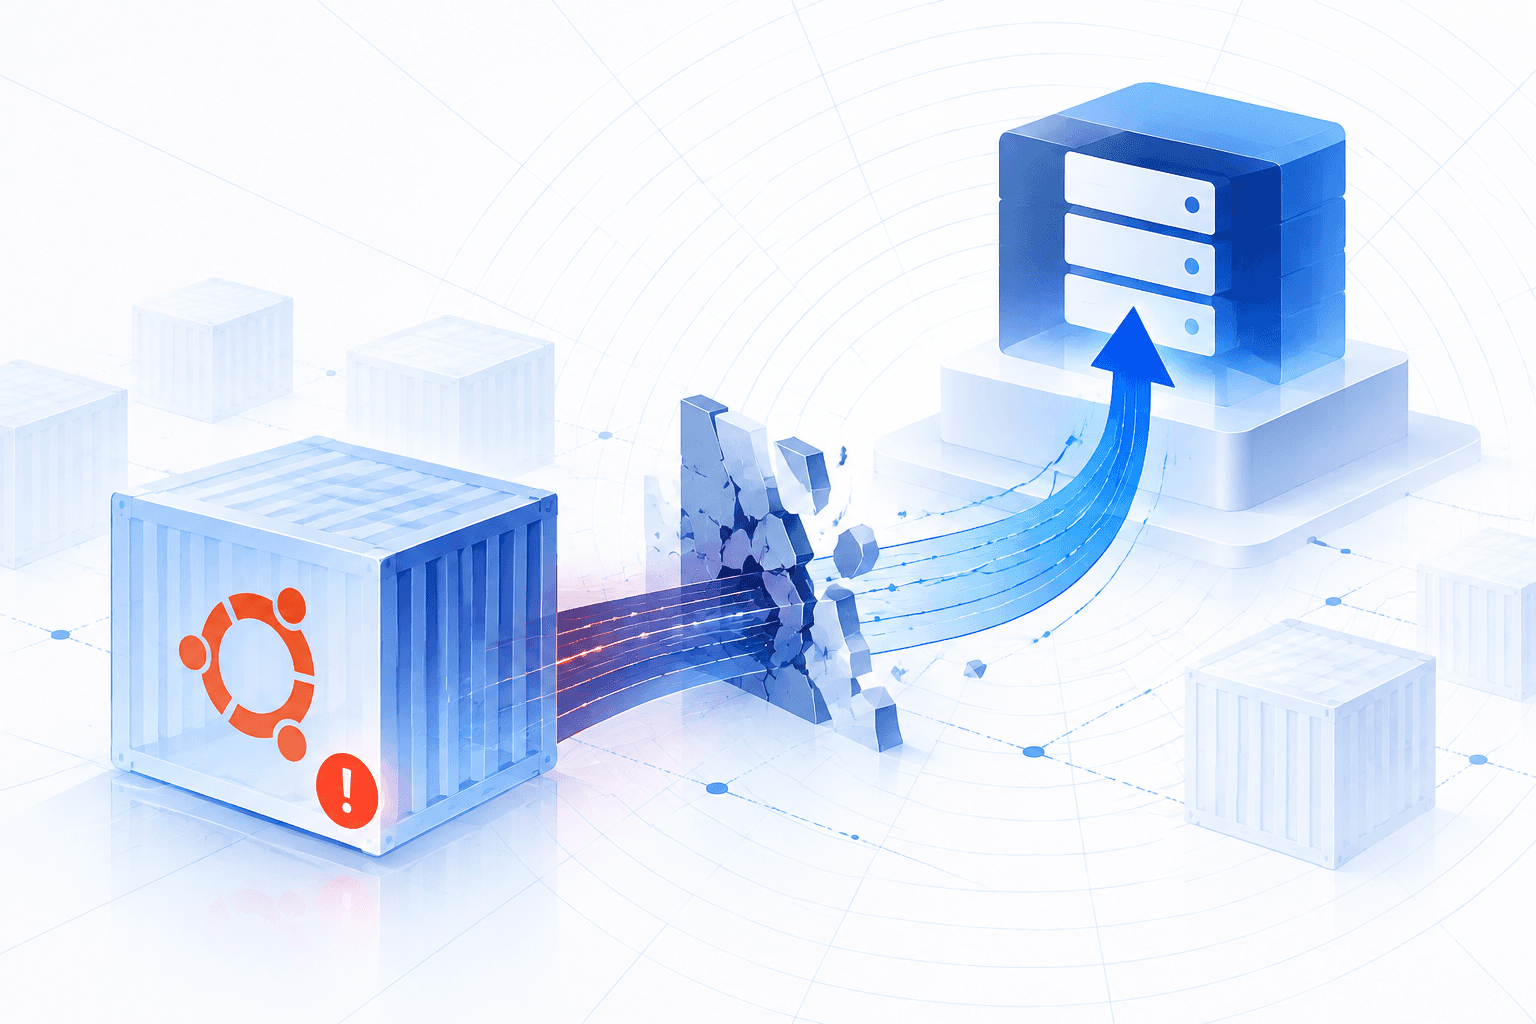
A public exploit targets CVE-2026-80521, a use-after-free vulnerability in the Linux kernel's AF_UNIX socket garbage collector that lets an unprivileged process escape a default Docker or Kubernetes container and obtain root privileges on its host. The bug leaves a stale scc_entry list pointer after a unix_vertex is freed, enabling the socket garbage-collection walk to dereference freed memory and bypass container namespace, cgroup, and seccomp isolation.
DepthFirst released research and working exploit code targeting Ubuntu 26.04; Ubuntu 26.04, 24.04, and 22.04 LTS—including affected cloud-kernel variants—reportedly had not distributed fixes. The vulnerability is reachable through ordinary AF_UNIX socket calls allowed by default Docker and Kubernetes seccomp profiles. Upstream fixed the issue in Linux 7.1.10 and 7.2; organizations should deploy patched host kernels and reboot, while using reduced capabilities, PFN-interface restrictions, resource limits, or microVM isolation as interim mitigations. No confirmed in-the-wild exploitation has been reported.