Mallory
← Back to News
loader-delivery-mechanismcybercrime-service-ecosystemvoice-social-engineeringpersistence-method

Sauron Loader Sold to Russian-Speaking Criminals Targets German Organizations

Malware Intelligence · 6 sources · Updated 2mo ago · First seen Sep 24, 2026
Sauron Loader Sold to Russian-Speaking Criminals Targets German Organizations

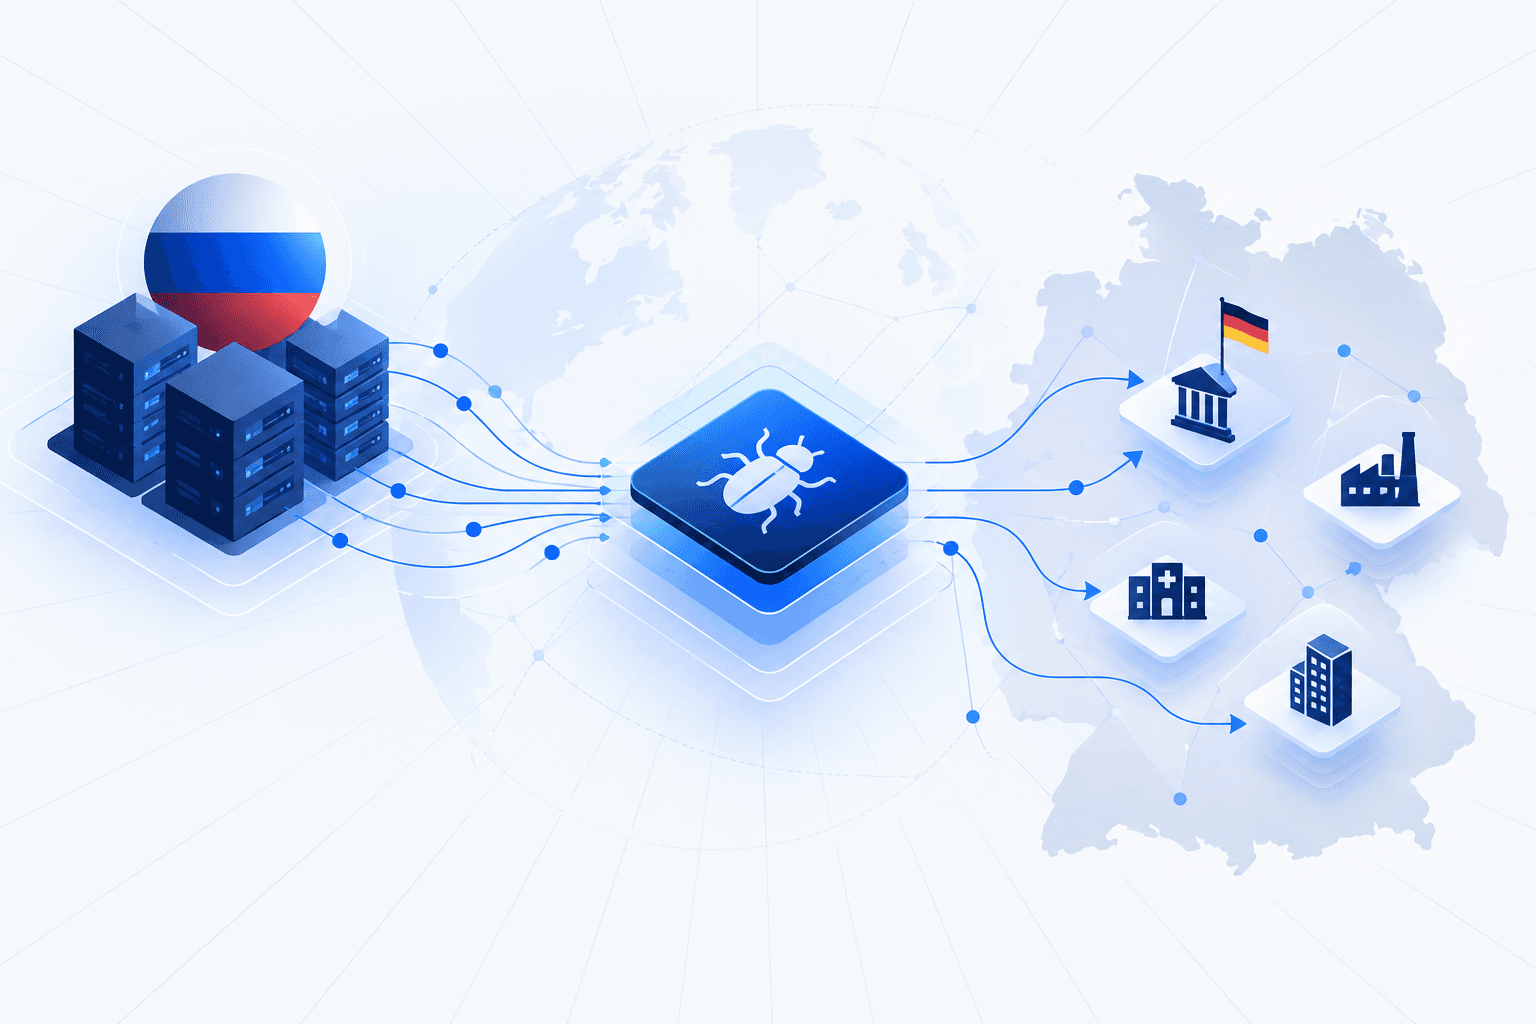
Researchers identified Sauron Loader, a previously undocumented C++ malware loader used as the final payload stage in multiple attacks on organizations in Germany. Marketed by the alias S4ur0n as a malware-as-a-service offering on Russian-speaking underground forums, it claims to prohibit attacks against CIS countries and public-sector entities. Observed intrusions began with ClickFix lures or vishing, including email-bombing victims before attackers called while impersonating IT support staff.

Sauron Loader establishes persistence with a scheduled task, uses DLL side-loading and in-memory decryption to reduce detection, and communicates with command-and-control infrastructure over HTTPS protected by custom Salsa20 encryption and RSA signatures. It can download and execute additional payloads, run commands, install drivers, inject shellcode, and capture and exfiltrate screenshots—capabilities that could support ransomware deployment, including operations associated with groups such as Qilin. Organizations should harden help-desk identity-verification processes, train staff against ClickFix and support-call social engineering, monitor scheduled-task creation and DLL side-loading, and investigate unusual HTTPS traffic and screenshot-collection behavior.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

4 events
  1. Reported Sep 25, 20262mo ago

    DCSO publishes Sauron Loader detection indicators

    DCSO CyTec published detection material for suspected Sauron Loader infections, including hashes for the analyzed MSI and malicious DLLs and reported command-and-control endpoints such as api.namsb-show.com and api.quinlantours.com.

    Sauron Loader Malware Uses DLL Side-Loading and In-Memory Decryption to Evade Detection | Cryptika Cybersecurity
  2. Reported Sep 24, 20262mo ago

    DCSO analyzes Sauron Loader MSI sample

    DCSO analyzed an MSI-delivered Sauron Loader sample that used DLL side-loading through legitimate rnpkeys.exe, in-memory code decryption, and a scheduled task named “keyroll” for persistence. The analysis identified encrypted HTTPS C2 communications, broad payload-execution support, and screenshot collection and exfiltration capabilities.

    Sauron Loader: A New Loader Lurking in Underground Forums - Malware Analysis - Malware Analysis, News and Indicators
  3. Reported Sep 24, 20262mo ago

    Sauron Loader used against organizations in Germany

    DCSO observed Sauron Loader as the final-stage payload in multiple attacks against German organizations. The campaigns used ClickFix and vishing initial-access methods, including email bombing and IT-support impersonation.

    Sauron Loader: A New Loader Lurking in Underground Forums - Malware Analysis - Malware Analysis, News and Indicators
  4. Reported Sep 24, 20262mo ago

    Sauron Loader advertised on underground forums

    An actor using the alias “S4ur0n” advertised Sauron Loader as a malware-as-a-service offering for Russian-speaking cybercriminals, claiming restrictions against targeting public-sector organizations and post-Soviet states.

    Sauron Loader: A New Loader Lurking in Underground Forums - Malware Analysis - Malware Analysis, News and Indicators
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Malware

1 linked

Organizations

1 linked
German organizations

Observables

12 linked

Indicator values are masked on this page. View all 12 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.